Cryptocurrency Posts
Crypto Briefing
Despite macroeconomic challenges, improving Bitcoin network health suggests a reduced likelihood of a prolonged bear market.
The post CryptoQuant analysis suggests bear cycle return is unlikely despite macro headwinds appeared first on Crypto Briefing.
The shift in trading dynamics highlights the growing influence of cryptocurrency on traditional markets, challenging established investment norms.
The post Strategy’s trading volume surpasses Berkshire Hathaway’s, marking a new era for Bitcoin proxy stocks appeared first on Crypto Briefing.
The escalation in Black Sea tensions threatens commercial shipping and complicates Ukraine's strategic goals, impacting Crimea recapture odds.
The post Russian drone strike on Tanzania-flagged ship kills one, injures three: Ukraine appeared first on Crypto Briefing.
Ripple's integration into AI payment protocols could significantly enhance XRP's role in automated transactions, boosting its utility and adoption.
The post Ripple adds XRP payments to Stripe and Coinbase’s x402 AI standard in new developer kit appeared first on Crypto Briefing.
Ripple's integration of XRP into AI-driven systems could accelerate its adoption, signaling a shift towards innovative financial solutions.
The post Ripple integrates XRP payments with Stripe and Tempo’s AI standard appeared first on Crypto Briefing.
Bitcoin Magazine
Bitcoin Magazine
Peter Schiff: “The Fed Has Already Lost The Battle Against Inflation” & BTC vs GOLD Debate
Peter Schiff says the bond market didn’t break recently, it broke in 2020, and everything since has been a slow unwind. Across this conversation with Grace Remington and Sean Hagan, he connects rising Treasury yields, the Fed’s expected rate decision, the dollar’s loss of purchasing power, and the central bank rush into gold. He argues that a stock selloff driven by higher rates would be deeply bearish for Bitcoin and the broader crypto market, and that political capital in Washington has already turned against it. The episode ends with Schiff and the hosts going head to head on whether anything actually backs Bitcoin.
00:00 — Peter Schiff says the bond market already broke in 2020
01:44 — How long the Treasury bear market could realistically last
04:18 — What Schiff would enact to actually bring inflation down
06:32 — Spending cuts, higher rates, and the recession nobody will accept
07:39 — Are we in the early stages of a dollar crisis?
08:26 — Rate hike odds and whether Warsh surprises the market
10:51 — Why Schiff calls it a cosmetic hike with no credibility behind it
12:33 — Why gold ran to 5,500 while Bitcoin lagged 23% off its highs
14:20 — Bitcoin priced in gold and the case that it peaked in 2021
17:29 — Tokenized gold vs Bitcoin: counterparty risk and what backs money
DISCLAIMER: The views and opinions expressed in this show are those of the participants and do not necessarily reflect the official policy or position of BTC Inc., Bitcoin Magazine, or any affiliated entities. This content is provided for informational and educational purposes only and should not be construed as investment, legal, tax, or accounting advice. Nothing contained in this show constitutes a solicitation, recommendation, endorsement, or offer to buy or sell any securities or financial instruments. Viewers should consult their own advisors before making financial or business decisions.
This post Peter Schiff: “The Fed Has Already Lost The Battle Against Inflation” & BTC vs GOLD Debate first appeared on Bitcoin Magazine and is written by Patrick Green.
Bitcoin Magazine
Bitcoin Price Wobbles Before Settling After Fed Raises Rates
Bitcoin’s price swung before settling largely unmoved over a 24-hour period after the Federal Reserve hiked interest rates — as expected — for the first time since 2023.
The leading cryptocurrency was recently priced at nearly $75,813 after dropping as low as $75,355 in the hour after the U.S. central bank gave its decision to increase the benchmark federal funds rate to a range of 3.75% to 4%.
Over a seven-day period, the coin is down nearly 4%.
Traders had bet there was a more than 90% chance that the Fed would raise interest rates ahead of its September meeting. Major Bitcoin trades therefore likely happened before Wednesday.
Speaking to reporters on Wednesday, Federal Reserve Chair Kevin Warsh didn’t reveal much about the central bank’s next moves but made it clear that price stability in the U.S. was its number one priority.
“The decision we made today was a sober decision, serious decision, responsible decision, one that we have been preparing for and thinking about in my 110 or 120 days here,” Warsh said.
He added: “The plain fact is that inflation is too high, and has been for too long. This summer’s inflation readings do not tell me that underlying trends have meaningfully improved.”
Wash — who has previously praised Bitcoin — said last month in his first major speech as head of the U.S. central bank that inflation was too high and had to be brought down.
The new chair is seemingly going against President Donald Trump’s wishes; the president has repeatedly called for lower interest rates and even threatened to fire the ex-Chair of the Federal Reserve for refusing to do so.
In a post on his Truth Social platform last week, the president wrote: “We should have the LOWEST RATE of any country in the World, like ‘the old days.'”
When asked by reporters about what he would say to the president, Wash replied: “I’ve got nothing for you on a discussion with the president.”
Bitcoin typically does well in a low interest rate environment because there is more liquidity to buy the asset.
The U.S. is currently in the midst of an affordability crisis and war in the Middle East has pushed up the price of oil, in turn compounding the problem as the cost of everyday goods in the world’s largest economy rises.
This post Bitcoin Price Wobbles Before Settling After Fed Raises Rates first appeared on Bitcoin Magazine and is written by Mathew Di Salvo.
Bitcoin Magazine
CFTC Chairman Says Agency Will Write Crypto Rules After Clarity Act Vote Fails
Commodity Futures Trading Commission Chair Mike Selig has said that the top regulator will go ahead and use its powers to advance crypto legislation despite the Clarity Act being blocked.
In a Wednesday statement released on X, Selig said that the regulator would still help U.S. President Trump “get the job done.”
Lawmakers blocked the Clarity Act on Tuesday in a procedural vote, with the long-awaited legislation missing the 60 votes needed to advance it. The bill aims to formally divide oversight between regulators, distinguishing which digital assets are securities, commodities or stablecoins.
“Americans deserve regulatory clarity, legal certainty, and consumer protections in crypto asset markets,” Selig wrote.
“President Trump promised to deliver a future-proof crypto asset regulatory market structure one way or the other, and we will help him get the job done using our existing statutory authorities.
“The U.S. is and will remain the crypto capital of the world. The CFTC is locked in and ready to ship its rules for the new frontier of finance.”
President Donald Trump last month urged lawmakers to pass the Clarity Act, calling the legislation “very powerful” — but Republicans said that Democrats were deliberately holding it back.
Regulators are now more crypto-friendly since President Trump appointed them and took the White House and are widely expected to continue pushing rules that help the crypto space.
The Securities and Exchange Commission last month proposed its own framework for crypto asset offerings, pressing ahead despite a vote on the Clarity Act stalling.
Despite being passed by the House of Representatives last year, the Clarity Act was in a deadlock for most of this year after the banking lobby clashed with lawmakers and crypto businesses over whether platforms like Coinbase should be able to pay customers yield.
Some lawmakers have sought to change wording in the bill regarding ethics, and a new bill started circulating in July. The draft bans government officials from promoting and making money from crypto.
But other Democratic lawmakers said it still fell short; a number of pro-crypto Republicans accused Democrats of deliberately playing politics and delaying the bill.
This post CFTC Chairman Says Agency Will Write Crypto Rules After Clarity Act Vote Fails first appeared on Bitcoin Magazine and is written by Mathew Di Salvo.
Bitcoin Magazine
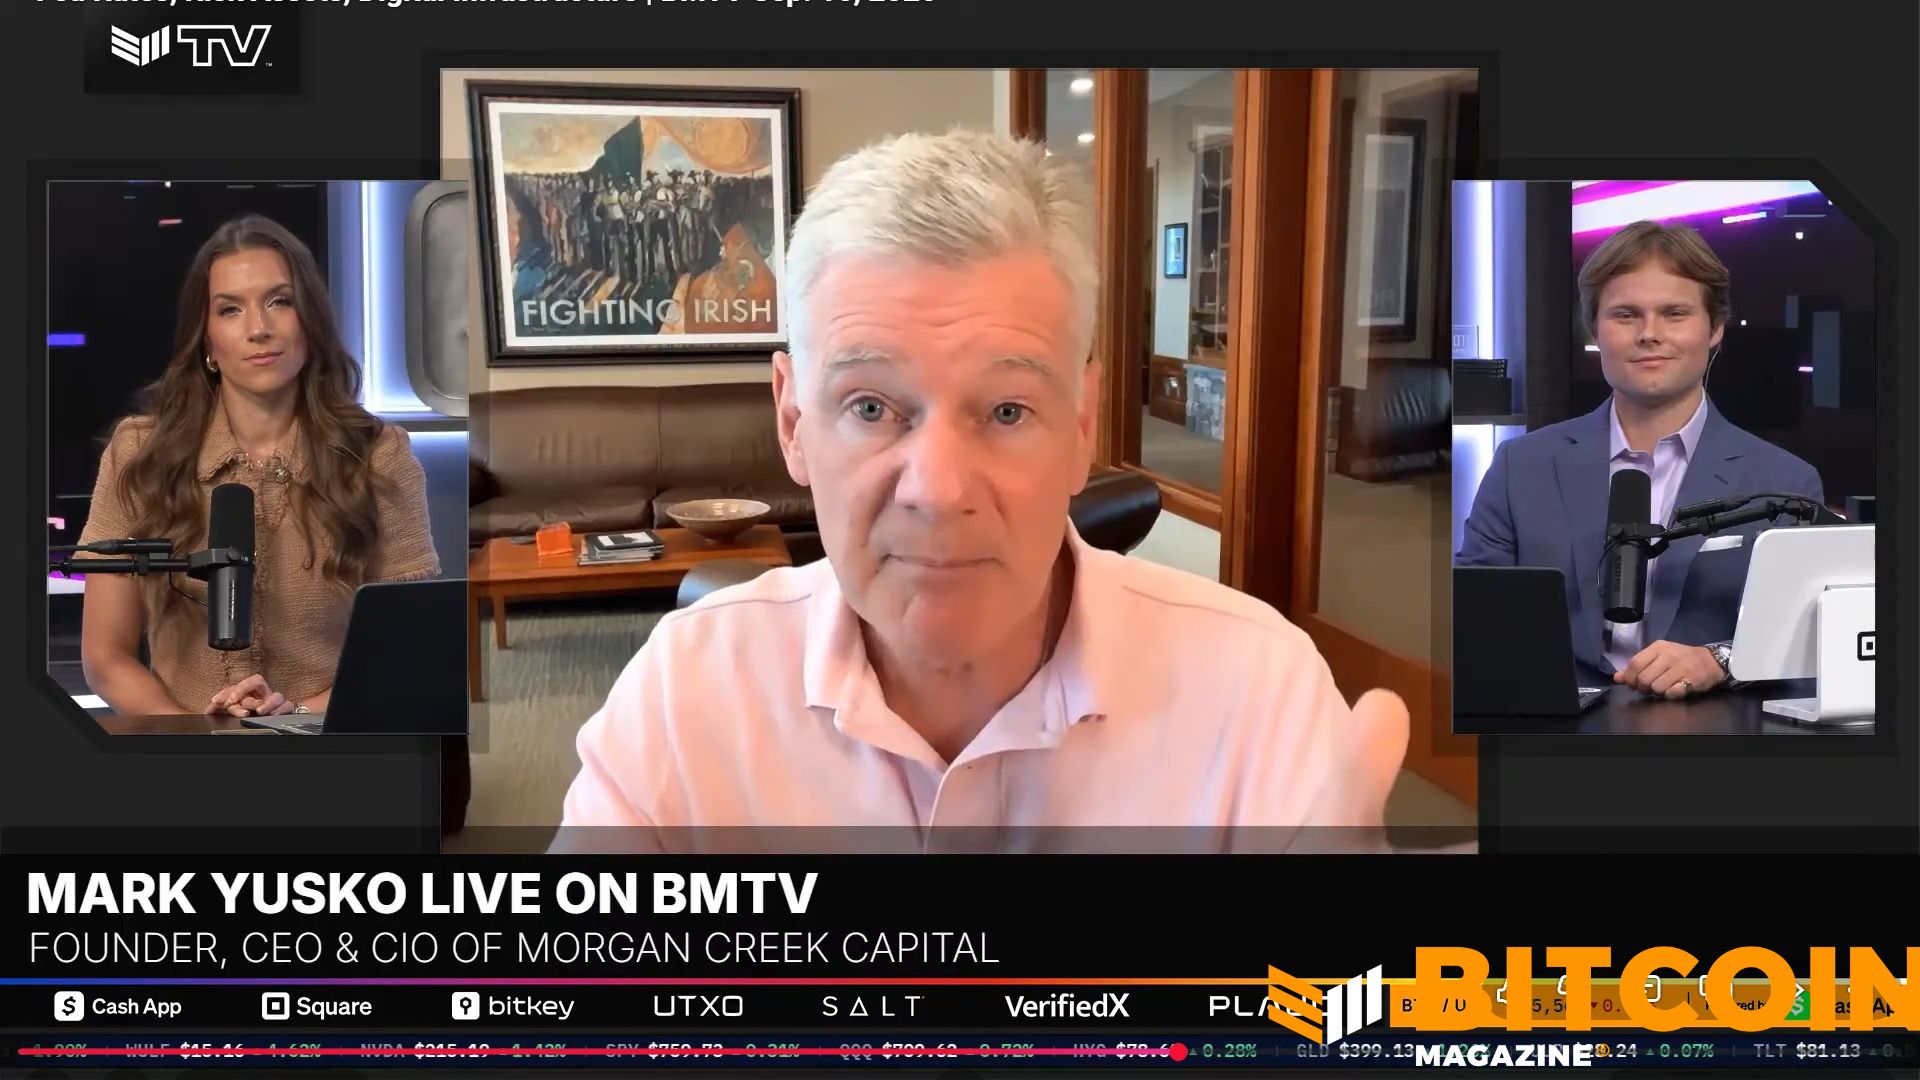
Bitcoin Is on Sale and Should Be Accumulated, Says Morgan Creek Capital CEO
Morgan Creek Capital CEO Mark Yusko has said that bitcoin’s fair value is $105,000 based on Metcalfe’s Law.
Speaking on Bitcoin Magazine TV on Wednesday, the investment management firm said that now was the best time to buy the leading cryptocurrency as it is “on sale.”
Metcalfe’s Law, an observation by Internet entrepreneur Robert Metcalfe, states that the value of a network is proportional to the square of the number of users. Bitcoin touched a high in October 2025 of $126,080 but was recently trading 40% lower than that, at $75,701.
JUST IN: Morgan Creek Capital CEO Mark Yusko says Bitcoin's fair value is $105,000 based on Metcalfe's Law
— Bitcoin Magazine (@BitcoinMagazine) September 16, 2026
Bullish! pic.twitter.com/zSpYHOCD3L

“So the fair value of bitcoin today, based on Metcalf’s law — Tim Peterson runs a model that tracks this really nicely — it’s about $105,000, but it’s $75,000,” Yusko said.
“Okay, so it’s on sale — you should accumulate things that are on sale.”
Yusko went on to say that bitcoin was the best way to protect one’s value and that investing in companies wasn’t good for the long-term.
“The problem is over a 30-year period, equity, 85% of companies disappear over 30 years. It’s amazing stat,” he said.
“What you really need is something to protect your value — and historically, for 5,000 years, there was one asset: gold.”
“Now we’ve got gold and bitcoin,” he added.
Bitcoin started rallying in August following news that the U.S. Treasury would at least double the size of its liquidity-support buyback operations. The announcement hurt the dollar but non-yielding assets have benefited.
Since then, some experts have said that the so-called debasement trade — when investors buy an asset as a way to hedge against a currency losing value — is back and will benefit bitcoin.
The trade was hot last year, and helped bitcoin’s run, but the digital asset lost steam after October as traders turned their attention to stocks related to artificial intelligence.
This post Bitcoin Is on Sale and Should Be Accumulated, Says Morgan Creek Capital CEO first appeared on Bitcoin Magazine and is written by Mathew Di Salvo.
Bitcoin Magazine
The Quantum Issue: To Freeze Coins Or Not
Bitcoin’s quantum debate is quite a quagmire. This is not merely a technical debate regarding the trade-offs of different types of cryptography and their strengths against a theoretical quantum computer. It is a debate about which properties of Bitcoin’s ethos are strongest when it is faced with a difficult dilemma: uphold the promise that valid coins remain spendable by their owners, or favor supporting the security of the system by not allowing a significant portion of its monetary supply to be raided via a vulnerability that was well known for many years.
The conundrum at the crux of this controversy is that every serious option violates a principle that Bitcoin users care about. Doing nothing may preserve today’s consensus rules while allowing future quantum-capable actors to take coins whose owners never consented. Freezing vulnerable coins may prevent that theft, but it retroactively invalidates long-standing spending conditions. A forced migration to quantum-resistant signatures may be prudent engineering, but it can also look like a deadline-backed confiscation regime. The debate is ugly because there is no clean path that perfectly preserves property rights, economic predictability, censorship resistance, backward compatibility, and user sovereignty all at once.
This is why I consider the problem to be fascinating. It’s multifaceted: simultaneously technical, sociological, philosophical, and economic in nature. Thus any serious discussion of the problem must consider every angle.
Throughout this essay I’ll be making the case that the quantum migration debate is far more nuanced than just a question between freezing or not freezing vulnerable bitcoin. Rather, it’s a question of how to minimize total property-rights violations once elliptic curve signatures no longer reliably authenticate rightful ownership.
The Quantum Threat
Bitcoin’s current authorization scheme to ensure that funds are only spent by their rightful owners depends on elliptic-curve cryptography. Legacy ECDSA signatures and Schnorr signatures both use the secp256k1 elliptic curve. Under ordinary classical computing assumptions, deriving a private key from a public key is computationally infeasible. A cryptographically relevant quantum computer running Shor’s algorithm changes that assumption: once a public key is available, a sufficiently capable quantum attacker could derive the corresponding private key and sign a transaction to spend the funds that would be accepted as valid by the network. Quantum computers threaten to break the public-key-to-private-key hardness assumption behind ECDSA and Schnorr.
That distinction matters because not all Bitcoin outputs expose the same information at the same time. Some output types reveal a public key immediately and remain vulnerable indefinitely. Others hide the public key behind a hash until the owner spends. This creates two broad attack classes. A long-range attack targets outputs whose public keys are already visible on-chain, such as old pay-to-public-key outputs and Taproot outputs. A short-range attack targets coins at the moment of spending: the owner broadcasts a transaction, the public key becomes visible, and a fast quantum attacker attempts to derive the private key quickly enough to replace or front-run the transaction.
The mining threat is different. Grover’s algorithm can in theory speed up brute-force searching for a valid block hash, but it only provides a quadratic speedup while Shor’s algorithm provides a superpolynomial speedup. Thus the competitive advantage is far less practical to bother using a quantum computer for mining.
The Quantum Quantum Threat
Amusingly, the threat of quantum computers is itself in a quantum state of superposition. A quantum computer worth worrying about may or may not be built and no one can prove or disprove that it will happen. Quantum skeptics don’t dispute that Shor’s algorithm could break ECC. They claim there is no good reason to believe we will ever build the kind of powerful, fault-tolerant quantum computer needed to run Shor’s algorithm at a cryptographically relevant scale.
Everyone agrees that breaking ECC isn’t possible with today’s noisy quantum processors. It requires many reliable logical qubits, extremely low error rates, lengthy computations with high coherence, and quantum error correction running successfully at scale.
A strong skeptical argument is that the quantum fault-tolerance threshold theorem depends on assumptions that may not be physically satisfiable with the required precision. Such assumptions include sufficiently independent noise, sufficiently accurate gates, limited unwanted interactions, and the ability to keep errors below an acceptable threshold across a huge system. Mikhail Dyakonov argues that the theorem assumes idealized conditions and does not tell us the real engineering precision needed to satisfy every assumption in an actual device.
Gil Kalai’s criticism is more structural. His argument is that realistic quantum systems may suffer from correlated noise and noise accumulation that prevent the formation of high-quality quantum error-correcting codes. In his 2011 paper, he proposes that physical realizations of quantum codes, correlations in stochastic systems, and accumulated noise could lead to failure of scalable quantum computers.
This may be the strongest skeptic argument: quantum error correction works only if the noise is tameable. If real high-qubit systems generate adversarially correlated errors, then adding more qubits may very well make the computer more fragile and unreliable.
Quantum scalability is a major unknown. Skeptics argue that progress from 50, 100, or 1,000 physical qubits does not automatically extrapolate to millions of physical qubits or thousands of logical qubits. Quantum systems are analog, delicate, and coupled to their environment. The engineering challenge is not just “make more qubits”; it is “make more qubits while suppressing crosstalk, leakage, correlated errors, calibration drift, thermal effects, measurement errors, fabrication variation, and control noise.” This is why critics reject simple timeline extrapolations. They view “we increased qubit count by X this decade, so we will break ECC by year Y” as weak reasoning.
Finally, quantum computer demonstrations have shown that current devices can only outperform classical simulations on carefully selected sampling tasks. Critics have a good point that this says little about executing long, structured algorithms like Shor’s algorithm with enough reliability to recover a 256-bit ECC private key.
Why Post-Quantum Migration Matters
Assuming that a cryptographically relevant quantum computer appears, merely adding the option for Bitcoiners to use post-quantum cryptography won’t be sufficient to stop a quantum attack. The total set of quantum-vulnerable bitcoin includes early pay-to-public-key coins, coins controlled by reused public keys, Taproot outputs, and cases where public keys or extended public keys have been revealed outside the chain. One striking figure is the concentration of BTC in old P2PK outputs, which are a tiny fraction of UTXOs by count but represent a much larger share of value, about 1.7 million BTC. Broader estimates via on-chain analysis of output types, activity patterns, and known ownership lead us to believe that at least 2.6 million BTC would remain vulnerable even if all active Bitcoin users migrated their wallets to post-quantum cryptography.
As such, even with opt-in post-quantum (PQ) cryptography, we should expect there to be a systemic risk sized pool of vulnerable coins lingering indefinitely. These coins could be employed by a quantum attacker to harm the system in a wide variety of ways – not just via selling them and dropping the spot price of BTC. Thus, protecting those vulnerable coins from a quantum threat requires some sort of rule changes that would effectively “lock out” a quantum attacker.
The rhetoric around this issue often uses terms like “confiscation,” “burning,” “freezing,” “stealing,” or “recovery,” but these describe different mechanisms. A freeze would not transfer coins to the state, miners, developers, or some recovery fund. In its most basic form, it would mean changing consensus rules so that certain outputs can no longer be spent using vulnerable ECDSA or Schnorr signatures. That is why advocates sometimes say “burn” rather than “confiscate”: the coins are not reassigned; they become unspendable via their private key. But for a rightful owner who still has the original key, the practical effect can still feel confiscatory: a spend that used to be valid is no longer valid.
BIP-361 divides the migration concept into phases. First, once a quantum-resistant address type exists, the Bitcoin network would stop allowing new coins to be sent to quantum-vulnerable addresses. Later, after a multi-year window, legacy ECDSA and Schnorr spends would become invalid. Finally, there remains the question of recovery options for users who can prove, without solely relying upon broken ECC, that they are the legitimate owner – such as through a zero-knowledge proof derived from a seed phrase or HD wallet structure. The proposal’s primary purpose is not to pick a post-quantum signature algorithm; rather the goal is to create incentives and deadlines so that users, exchanges, custodians, wallets, and institutions actually migrate in a timely fashion and thus allow us to deprecate ECC in order to prevent a quantum attack.
The Case for Freezing
The strongest pro-freeze argument starts from a simple claim: a quantum attacker who derives a private key from a public key is not the legitimate owner in any morally meaningful sense. Under this view, “just let vulnerable coins be taken” is not neutrality; it is allowing a new class of actors to loot old outputs because the protocol failed to strengthen a lock that is known to be weak. Freeze advocates argue that the resulting harm from allowing quantum theft is not just to negligent owners but to all holders, because a successful quantum sweep would redistribute wealth to whoever possesses early quantum capability. This is problematic because that amount of bitcoin in a single actor’s hands who spent relatively little resources to obtain them can be quite dangerous for the ecosystem’s security. Bitcoin’s security model assumes economically rational participants that are incentivized to protect the value of their coins, but a quantum-capable actor has the potential to break that assumption. The pro-freeze position is that Bitcoin should not reward the first entities to break ECC with ammunition that could be leveraged to harm the system.
This argument is especially true for coins believed to be lost. If lost coins are suddenly recoverable by quantum attackers, the circulating supply effectively increases. That does not violate the formal 21 million cap, but it does change the economic landscape: coins that the market may have treated as inert can re-enter circulation, possibly rapidly and in concentrated hands.
The pro-freeze side also argues that the threat is not limited to ordinary profit-seeking. A quantum-capable adversary could attack Bitcoin politically, destabilize markets, undermine public confidence, grief the network for many years, or even acquire enough hashrate to 51% attack the network. Analysis of the game theory in play shows that we can’t simply assume an attacker sweeps vulnerable BTC to sell it and ride off into the sunset; there is a far wider range of strategies and undesirable outcomes.
A related argument is about market panic. Pieter Wuille’s comments in the mailing-list debate sharpen this point: the medium-term danger may be not only an actual cryptographically relevant quantum computer, but the credible belief that one may exist soon. If markets come to believe that a large share of Bitcoin’s supply can be seized at any moment, merely offering voluntary post-quantum outputs may not be enough to restore confidence. A credible plan to disable vulnerable spends could itself be a sufficient reassurance mechanism.
The pro-freeze camp also sees deadlines as necessary because voluntary migration is likely to be slow. People procrastinate; institutions move slowly; hardware wallets, exchanges, custodians, estate plans, multisig coordinators, and cold-storage procedures all need time to implement changes and plan for migrations. Matt Corallo has argued that Bitcoin should add a simple post-quantum capability well in advance of it being necessary, because wallets need to start embedding or committing to quantum-resistant public keys long before any later emergency decision about freezing vulnerable UTXOs becomes credible.
There is also a fiduciary responsibility argument. Public companies, ETFs, custodians, and exchanges will be unable to ignore a known migration deadline. A locked-in consensus change gives compliance departments and risk committees something concrete to act on. It also turns an abstract future threat into a project plan: upgrade software, generate new addresses, move funds, verify backups, communicate with customers, and complete migrations before a known date. BIP-361 explicitly argues that exchanges and custodians would face fiduciary and legal pressure to act once a deadline exists.
It’s also worth noting that all of this migration planning is applicable to more situations than just the emergence of a cryptographically relevant quantum computer. Most of the arguments in this debate apply to ANY situation where ECC is known to have been weakened. Generally speaking, cryptography tends not to withstand the test of time and any given cryptographic algorithm tends to be weakened over long time frames (decades) as researchers find flaws and develop new techniques that break prior assumptions.
Finally, freezing advocates argue that Bitcoin has always depended on users enforcing rules that protect the system as a whole. A soft fork that objectively disables a known-insecure spend path is not the same as arbitrary political confiscation, in their view. The proposed line is not “these people are disfavored” but “these script types require cryptography that no longer meets the bar for Bitcoin’s security assumptions.” If the rule is mechanical, objective, announced years in advance, and paired with a viable migration path, proponents argue that it is more akin to replacing a broken lock than blacklisting an owner.
Anti-freeze Arguments
The strongest anti-freeze argument starts with the opposite premise: Bitcoin’s social contract is that a valid coin remains spendable by the holder of the corresponding key under the consensus rules accepted when the coin was received. Retroactively invalidating that spend path crosses an inviolable line. It turns “not your keys, not your coins” into “not your upgraded-by-deadline, not your coins.” Even if no one else receives the frozen coins, the original owner loses practical control. That is why critics describe forced freezing as confiscatory, not merely protective.
This objection is not just sentimental. Bitcoin’s credibility depends heavily on the expectation that developers and node operators will not pick winners and losers among UTXO owners. A freeze aimed at “vulnerable coins” may be technically objective, but it still targets a subset of owners based on past address choices, wallet design, dormancy, or inability to act. Critics worry that once the network accepts retroactive invalidation for one reason, future coalitions may find other reasons: sanctions, theft recovery, inheritance disputes, state pressure, “obviously” lost coins, or other emergencies.
A second objection is that freezing cannot distinguish between lost coins, careless owners, dormant owners, imprisoned owners, dead owners with heirs, users in hostile jurisdictions, timelocked arrangements, forgotten cold storage, and deliberately long-term savers. Bitcoin has many users whose goal is to avoid being forced to stay online and responsive to policy changes. A person who stored coins safely for decades should not necessarily lose them because the rest of the network later declared their storage method obsolete. It’s worth noting that there is an incentive conflict between active current holders who benefit from reducing the effective supply and inactive rightful owners who may be unable to take action to defend themselves.
A third objection is uncertainty. A cryptographically relevant quantum computer may arrive later than expected, may not arrive in the form feared, may remain secret for some time, or may be countered by less drastic tools. If Bitcoin permanently burns millions of coins and the threat does not materialize on the assumed timeline, the network will have committed an irreversible self-inflicted property-rights violation. Critics therefore argue that premature freezing is worse than measured preparation.
A fourth objection is governance and legitimacy. Freezing vulnerable coins would be one of the most controversial consensus changes in Bitcoin’s history. Some have warned that announcing a freeze of old UTXOs could damage Bitcoin’s image more than a quantum attack itself and could produce a major fork in which one side accepts the freeze and another preserves old spendability. In that scenario, the “solution” creates a new political attack surface: exchanges, custodians, miners, and users must choose which chain’s property-rights model they prefer.
A fifth objection is legal risk. Some participants in the mailing-list debate warned that developers, companies, or miners involved in consciously changing code to freeze funds could face liability claims from owners whose coins become unspendable. Even if those claims ultimately fail, the legal process itself could chill development, divide institutions, and make consensus coordination harder.
A sixth objection is technical humility. Post-quantum cryptography is real, but not free. NIST has standardized ML-DSA, SLH-DSA, and ML-KEM, with more work continuing, yet Bitcoin has unusual constraints: every byte matters, verification cost matters, wallet compatibility matters, and consensus failures are catastrophic. Chaincode’s comparison of candidate schemes in their quantum deep dive report shows why the choice is not trivial: post-quantum signatures and keys can be much larger than Schnorr or ECDSA, and schemes differ sharply in maturity, signature size, public-key size, signing cost, verification cost, and assumptions.
That makes critics wary of forcing migration before the destination is mature. A bad post-quantum migration could reduce throughput, raise fees, bloat the UTXO or witness data burden, introduce new cryptographic assumptions, or force another migration later if the chosen algorithm weakens. Conventional Schnorr signatures are tiny compared with many hash-based post-quantum signatures, while lattice based cryptography has other trade-offs and maturity questions. On a related note, given the larger data sizes of signatures, this will increase the cost of transacting on chain and could price out less wealthy users.
Doing Nothing vs Doing Something
As I stated over a year ago in my first essay on this topic: if quantum computing becomes a threat to Bitcoin’s elliptic curve cryptography (ECC), an inviolable property of Bitcoin will be violated one way or another.
You’re probably familiar with the fundamental principle coined by Andreas Antonopoulos:
“Not your keys, not your coins.”
I posit that the corollary to this principle is:
“Your keys, only your coins.”
The point is that keys don’t merely authorize spending, but that signatures are supposed to be unforgeable evidence of control by the legitimate keyholder. A quantum-capable entity breaks the corollary of this foundational principle. We secure our bitcoin with the mathematical probabilities related to extremely large random numbers. Your funds are only secure because truly random large numbers are safe from being discovered by anyone else in the world.
The do-nothing position is often caricatured as “let quantum thieves steal everything.” Taking a noninterventionist stance against quantum theft is certainly principled: Bitcoin is a voluntary bearer asset governed by rules, and users are responsible for managing known risks. If a coin is encumbered by a script that becomes weak over decades, perhaps that is no different from losing a seed phrase, using weak entropy, trusting an insecure custodian, or failing to follow any number of other best practices. Under this view, the network’s job is not to guarantee the security of every historical locking script forever; rather it’s to enforce the rules as written.
This camp can also state that total supply is the only guarantee of the network, not effective circulating supply. The 21 million cap does not say “21 million minus coins assumed lost.” It says no more than 21 million coins will be issued. If a lost-looking coin later moves because its key is found, inherited, cracked through poor entropy, or recovered through quantum attack, the total issued supply has not changed. That argument is unsatisfying to people who see quantum funds sweeping as theft, but it is internally consistent: protocol rules define validity, not subjective moral beliefs about rightful ownership.
The do-nothing side also values operational simplicity. Any freezing rule requires defining what constitutes a vulnerable bitcoin redeem script, choosing activation dates, coordinating wallets and miners, communicating to users, handling edge cases, and absorbing political fallout. Doing nothing avoids a contentious consensus change. If post-quantum tools become available, users who care can migrate voluntarily, while users who do not migrate bear their own risk.
But the weakness of the “pure do-nothing” perspective is that it treats quantum theft as an individual-risk problem when it may actually become a system-risk problem. If enough coins are exposed, and if the market believes a capable attacker can use them to harm the ecosystem, the damage is not confined to owners who failed to migrate. It affects public confidence in the system which then cascades into negative pressure on the exchange rate, thermodynamic security (miner revenue,) and the revenue of many Bitcoin businesses. That is why even many people uncomfortable with freezing still support early preparation.
Apathetic “code is law” Bitcoiners are free to do nothing, but they should not delude themselves into thinking that they can stop others from trying to do something.
Alternative Proposals
Because “freeze all vulnerable UTXOs” and “do nothing” are both brutal in their own ways, much of the interesting work is in alternative proposals that would help users retain their property rights in the face of a quantum threat.
- We could prevent new vulnerable outputs while not yet freezing old ones. This is the least coercive part of forced migration. Once a safer output type exists, consensus or policy rules could discourage or even disallow sending bitcoin into vulnerable locking scripts. That reduces future damage without immediately invalidating old property claims. BIP-361 includes this as Phase A, and several critics are more open to this kind of forward-looking restriction than to permanent retroactive burns.
- Alternatively, the network could enforce a temporary lock rather than permanent burn. Boris Nagaev suggested that if old EC spends must be disabled, the lock could include a future re-enable height or some other mechanism that gives the community time to build recovery paths. Conduition explored how such a phase might interact with P2QRH/P2MR-like outputs and warned that simply banning all EC checks could accidentally affect hybrid constructions unless the rule is designed carefully. The appeal of a temporary lock is political as much as technical: it signals emergency containment rather than permanent confiscation.
- Another option is rate-limiting, represented by the Hourglass proposal. Hourglass V2 focuses on old P2PK coins and would restrict spending so that only one P2PK input could be spent per block, with a net limit of one BTC per block from those outputs. Its authors present it as a way to avoid both immediate burning and unconstrained quantum liquidation: coins are not destroyed, but their ability to flood the market is throttled. The proposal estimates that unconstrained P2PK sweeping could be extremely fast, while the one-BTC-per-block design would stretch full P2PK movement over decades.
Hourglass has its own critics. Opponents argue that it still violates permissionless spending by imposing special restrictions on a class of otherwise valid coins. It may also create a long-running race between legitimate owners and quantum attackers rather than resolving ownership. Some critics say that if the quantum threat is real, taking decades to clear exposed P2PK outputs gives attackers plenty of time; if the threat is not real, the rule is needless interference. - There is the concept of commit-delay-reveal, sometimes discussed through Guy Fawkes-style constructions. The basic idea is that a user first commits to a future spend in a way that a quantum attacker cannot exploit immediately, waits for the commitment to become deeply confirmed, and later reveals the secret needed to validate the spend. This can prevent a short-exposure quantum attacker from seeing a public key and instantly stealing the coin before confirmation. Chaincode describes commit-delay-reveal as opt-in and potentially useful, while the Optech summary notes that these schemes can let safely spendable bitcoins avoid destruction and reduce migration urgency.
- Quantum safe funds recovery without EC signatures, especially for HD wallets, should be feasible. Or Sattath and others discussed “signature lifting” ideas where the owner proves knowledge of a seed or derivation path rather than proving control through the vulnerable public key. Olaoluwa Osuntokun built a proof-of-concept using zk-STARKs to prove that a Taproot BIP-86 output key was generated from a BIP-32 seed path. This would certainly be a last resort scenario for procrastinators to recover funds, given that the latest optimized version of the scheme requires a 200 KB proof. It would certainly price out recovery of small UTXOs, because a best case scenario would likely cost several hundred dollars in transaction fees but could easily run into the thousands or tens of thousands at higher transaction fee rates.
This recovery path is attractive because it changes the moral shape of the debate. If rightful owners can later recover frozen coins through non-EC proofs, freezing no longer has to mean permanent destruction. But the costs are serious: large proofs, complex verification, privacy leakage, wallet-derivation assumptions, inability to cover every historical wallet type, and the danger of adding novel cryptography to Bitcoin consensus. Critics of the zk-STARK approach emphasized that megabyte-scale proofs and multi-second verification times are difficult to reconcile with Bitcoin’s conservative design.Though further research is already finding optimizations that are more efficient. - Dual-signature or market-driven migration. Marc Johnson and others suggested enabling quantum-resistant outputs, allowing optional dual signatures, giving fee or policy incentives, and letting users choose their own risk instead of imposing a hard loss deadline. This approach preserves property rights better than forced freezing, but it won’t solve the systemic-risk problem if too many high-value coins remain exposed.
Tricky Technical Trade-offs
The migration debate cannot be fully separated from the choice of quantum-resistant signatures because the size of signatures will affect the system throughput. NIST’s post-quantum standards provide a serious foundation: FIPS 204 standardizes ML-DSA, FIPS 205 standardizes SLH-DSA, and FIPS 203 covers ML-KEM for key establishment. But Bitcoin needs digital signatures and script-compatible ownership proofs, not just general-purpose cryptographic standards. A scheme suitable for TLS or government communications is not automatically ideal for a blockchain with limited block space and global verification requirements.
Hash-based signatures are conservative and appealing because their assumptions are simple, but they are large. Lamport-style signatures can be enabled in some form with script upgrades such as OP_CAT, but the Taproot key-path problem remains: if a Taproot output has a quantum-vulnerable key path, placing a Lamport signature in the script path does not make the whole output quantum safe unless the vulnerable key path is removed or disabled. BIP-347’s OP_CAT discussion explicitly notes this problem.
Lattice signatures such as ML-DSA offer more compact signatures than many hash-based options, but they bring different assumptions and implementation risks. Falcon-style signatures are compact but historically more delicate to implement. SPHINCS+/SLH-DSA is conservative but large. Experimental schemes may be attractive on paper but too immature for Bitcoin consensus. This is why a credible migration plan likely needs algorithm agility, test deployments, wallet experiments, careful fee modeling, and perhaps multiple acceptable post-quantum paths rather than a single rushed winner.
The block space problem is severe but not intractable. Chaincode estimates that migrating all UTXOs would take roughly 76 to 142 days if migration consumed all block space, and 305 to 568 days if it consumed 25% of block space. That is just raw migration throughput; it does not include human coordination, wallet upgrades, institutional approvals, support for air-gapped signing, hardware replacement, accounting workflows, etc.
A full timeline for UTXO set migration is measured in years, not weeks. Chaincode’s high-level estimate sketches a best case of roughly five years and a worst case closer to fifteen years for research, BIP work, implementation, deployment, and migration. The same report notes that in an emergency the timeframe could potentially be accelerated to 2 years, but historical emergency protocol fixes are not really analogous because the quantum migration problem touches every layer of the ecosystem.
The Ethics of Property Rights
The moral disagreement comes from two competing definitions of ownership.
The anti-freeze side supports a “code is law” perspective: ownership means control under the consensus rules. If an output is spendable by an ECDSA or Schnorr signature, then disabling that spend path violates the owner’s property rights. The network does not know whether a coin is lost, abandoned, inherited, intentionally dormant, or inaccessible for temporary reasons. Therefore, freezing is collective punishment imposed on a subset of users for failing to follow a new migration demand.
The pro-freeze side says ownership cannot mean “anyone who can break the cryptography gets the coin.” Bitcoin’s signatures are intended to authenticate the legitimate keyholder, not to create a prize for whoever first builds a machine that defeats the authentication scheme. If quantum capability turns public keys into private keys, then an EC signature no longer carries the same moral information it carried before. Under this view, refusing to freeze is not neutrality; it is a security failure to knowingly allow a compromised authentication mechanism to transfer wealth.
Both positions are coherent. The first protects rule stability and bearer-asset finality. The second protects the deeper intent of the locking script. The painful point is that Bitcoin’s consensus rules are the only practical arbiter. The protocol cannot read intent. It can only accept or reject transactions according to rules. Any attempt to encode “rightful ownership” after ECC breaks either becomes overly broad, relies on new proofs, or leaves some victims behind.
I submit that property rights have been violated on Bitcoin before. Allow me to introduce you to the Value Overflow Incident as it is commonly known.
On August 15 2010, it was discovered that block 74,638 contained a transaction that created 184,467,440,737.09551616 bitcoin for three different addresses. Two addresses received 92.2 billion bitcoins each, and whoever solved the block got an extra 0.01 BTC that did not exist prior to the transaction. This was possible because the code used for checking transactions before including them in a block didn’t account for the case of outputs so large that they overflowed when summed.
A new version of the client was published within five hours of the discovery that contained a soft-forking change to the consensus rules that rejected output value overflow transactions. The blockchain was forked. Although many unpatched nodes continued to build on the “bad” blockchain, the “good” blockchain overtook it at a block height of 74,691 at which point all nodes accepted the “good” blockchain as the authoritative source of Bitcoin transaction history.
The bad transaction no longer exists for people using the chain with the greatest cumulative proof of work. Therefore, the bitcoins created by it do not exist either.
Thus, from a pure property rights perspective, the person who followed the rules of the network at the time had their property confiscated from them because the overwhelming majority of other actors on the network considered their action to be undesirable and a threat to the network.
Anti-freeze folks will likely say that this is not a problem because the INTENT of protocol rules is what matters, and the intent was for the network to guarantee a maximum supply of 21 million BTC. I would tend to agree, and make the counter-claim that the INTENT of using ECC to secure BTC is to ensure that it’s infeasible for anyone to guess your private key.
Economic Stakes
A sudden sweep of funds by a quantum-capable entity could affect Bitcoin through several channels.
- Coins thought dormant would re-enter circulation, increasing the effective bitcoin supply.
- Markets could panic before any actual sweep if credible evidence appears that a CRQC exists or is near.
- Miners could be affected if price falls sharply, because their budget is tied to block subsidies and fees in BTC terms converted into operating revenue.
- Exchanges and other businesses could face operational stress and massive drops in revenue if customer deposits are exposed or if market structure breaks under uncertainty.
“Lost coins only make everyone else’s coins worth slightly more. Think of it as a donation to everyone.” – Satoshi Nakamoto
If true, the corollary is:
“Quantum recovered coins only make everyone else’s coins worth less. Think of it as a theft from everyone.”
If a large amount of BTC is permanently lost, remaining holders benefit from a lower effective circulating supply. If quantum attackers revive those coins, remaining holders lose that benefit. Critics of freezing respond that this is exactly why active holders have a conflict of interest: they may prefer burning dormant coins because it makes their own coins scarcer. That is not a trivial objection. A freeze can be framed as protecting the network, but it can also be framed as enriching active holders at the expense of inactive ones.
That conflict is why the specific definition of vulnerable coins matters greatly. Freezing only ancient P2PK outputs with already exposed public keys is easier to justify than freezing every vulnerable output, because the funds are far more likely to be lost. Freezing Taproot outputs is more complicated politically because Taproot is recent and intentionally adopted by users who were following modern wallet guidance. Freezing reused outputs raises another problem: the vulnerability may come from user behavior rather than address type. Freezing based on on-chain public key leakage is also a half measure because the chain can not know what was leaked off-chain; many wallets share their xpubs with third parties, for example.
A broad freeze could therefore be both underinclusive and overinclusive. It could miss off-chain exposed keys while capturing dormant but legitimate owners. A narrow freeze could reduce the worst risk but leave enough vulnerable value to sustain panic. This is why I believe the optimal solution is complex and requires a multi-phased approach, rescue proofs, and objective script rules rather than discretionary address lists.
Herding Cats
Bitcoin is an anarchic system of rules without rulers. It has no authority that can dictate changes to consensus rules. A rule to deprecate ECC would need broad agreement among node operators, miners, exchanges, wallets, custodians, merchants, and users. In formal terms, many proposals are soft forks: they make previously valid spends invalid under stricter rules. But in social terms, a soft fork that disables old coins is much heavier than an ordinary tightening rule. It directly affects property expectations.
This governance problem gets worse under emergency conditions. If Bitcoin waits until there is credible proof of a CRQC, the community may have to act during panic, misinformation, market stress, and adversarial pressure. But if Bitcoin acts too early, it risks freezing coins before the threat is real enough to justify it. Chaincode explicitly warns that planning and communication should happen before the threat becomes acute, while also acknowledging that stakeholder coordination, regulation, taxation, and user communication are major obstacles.
This creates a paradox. The best time to design a quantum migration is before it is urgently needed. The hardest time to persuade people to accept controversial measures is also before they are urgently needed. Once the emergency is obvious, technical and social options narrow dramatically. In short, because: Bitcoin moves slowly, some action must happen before the relevant computer arrives if we want a non-chaotic outcome.
A credible process therefore matters almost as much as the final rule. The community would need clear definitions, simulations, reference implementations, wallet support, testnet deployments, activation thresholds, recovery research, and communication to nontechnical users. Without that, an ECC deprecation proposal would look like coordination against dormant holders. With it, even opponents could at least evaluate concrete trade-offs instead of reacting to abstractions.
Governance Game Theory
The threat of a quantum attacker is similar to The DAO incident that Ethereum had to deal with in 2016. In other words: the ecosystem had time (about a month) to take action to stop an attacker from getting away with taking ownership of 5% of all ETH at the time. For 5% of all ETH to go into the hands of a malicious actor was considered to be a systemic risk.
To put this in context, from my own analysis of the blockchain I think a reasonable estimate for the number of lost coins with exposed public keys is roughly 2,600,000 BTC, or 13% of the current total supply. In other words, this is about how much BTC I expect would be unable to migrate to a quantum safe locking script if we come to consensus on implementing a post-quantum signature scheme.
However, note a crucial difference between the DAO situation and this one. With the DAO, the Ethereum community had to hard fork in order to regain control of stolen tokens. With a BIP-361 style change, it would be a soft fork. Which is to say:
Opposing the DAO fork was relatively easy: needed not to do anything and stayed on the chain with the original set of rules. That chain is now known as Ethereum Classic.
Opposing a quantum migration soft fork, assuming it has a supermajority of hashrate, would require dissenting users to coordinate a User Rejected Soft Fork, which has never been done before.
The Slippery Slope of Centralization
Some have stated that a forced migration proposal like BIP-361 is untenable because it would set precedent for “centralized planning” over who gets to use Bitcoin. In other words, this could lead to similar types of freezing to stop anyone who is considered a “bad actor” from using the system, such as in response to major thefts and hacks.
We already know that nothing about Bitcoin’s rules is truly immutable. It’s not possible to create a protocol that is impossible to change – the best you can do is to align incentives that make it unlikely to change. In the case of proposing changes as controversial as altering ownership / the money supply, you should expect that such proposals only have the slightest glimmer of being accepted if the alternative is expected to be detrimental to nearly all Bitcoiners.
As for the claim that it will lead to protocol-level confiscation in response to hacks and such, it’s simply not possible for an ecosystem as distributed as Bitcoin to coordinate a response fast enough to outpace an individual actor. To be more precise: trying to blacklist a specific address / set of addresses is infeasible because the “target” of such a protocol-level blacklist would simply move their funds faster than the ecosystem could coordinate freezing them.
Prior Precedents
The DAO was a special case in which a decentralized community actually had time to react to a massive theft, because The DAO’s smart contract essentially had a “cooldown rule” that made them have to wait for a month after initially redirecting funds into their own control before they could send them anywhere else, such as to “cash out.” As such, there was time to gather consensus from the wider ecosystem (they even conducted coin voting) in order to pass a pretty controversial hard fork.
What was the end result? We can actually observe how the market reacted. Despite all of the controversy, the economic reality was clear. Ethereum Classic, which abided by “code is law” and “do nothing” perspective, allowing the attacker to retain control of 5% of the network’s tokens, struggled to even reach 10% of the market value of interventionist Ethereum, which changed the rules of the network in order to return funds to their rightful owners.
As previously mentioned, Bitcoin also had the Value Overflow Incident in which bitcoin created by someone who was just “following the rules of the protocol” had them taken away by a coordinated consensus change.
These are stark examples of why I believe that economic incentives can and will trump moral and philosophical principles. Some will surely say that Ethereum and Bitcoin have little in common, and it’s certainly true that these different networks tend to have very different ethos and driving factors. But from an economic perspective, they share the same incentive structures with regard to a malicious entity controlling a substantial portion of the market cap. Bitcoin in 2026 is a very different ecosystem from Bitcoin in 2016. Consider all of the new entrants, many of which did not adopt BTC as a result of the libertarian standpoint.
It’s a pretty tough sell to get mainstream audiences to believe that bad actors should not be stopped if there is a means to do so. It’s an even tougher sell to tell companies and institutions that are making millions if not billions of dollars off of managing an asset that they should stand idly by and watch an existential threat to their business line carry out an attack that can be prepared for not just months, but potentially years or decades ahead of time.
Framing Matters
I think the worst possible framing of this debate is “quantum safety versus irresponsible users.” That trivializes the property-rights objection. Another terrible framing in my mind is “freezing is always theft, therefore no preparation is needed.” That trivializes the systemic-risk problem and overlooks the options we have to help protect property rights.
Matt Corallo has astutely pointed out that the debate over deprecating the use of vulnerable signatures is interesting because it can be framed in very different ways that sound the same on the surface.
- “Protect people’s property rights to the greatest extent possible.”
- “Don’t freeze anyone’s coins.”
The first perspective supports freezing ECC spends while also adding the maximum number of ways to safely recover funds (BIP-32 proofs, pre-Q-day commitments for non-BIP-32 wallets and timelocked coin wallets, etc).
The second stance actually minimizes the number of people who get to keep their coins and maximizes theft exposure. But it’s far simpler and avoids a controversial fork.
Thus I think this is not a binary debate of “to freeze or not to freeze.” Rather, a superior framing of the problem is: what is the optimal set of rules that minimizes property rights violations under conditions where the original cryptographic authentication mechanism is no longer reliable to authenticate rightful ownership?
Under that framing, deprecation of ECDSA signatures becomes more defensible if several conditions are met.
- There must be a widely reviewed quantum-resistant destination. Users cannot be coerced to migrate into a half-baked or experimental mechanism. The destination may be P2MR plus future PQ script paths, a standardized and well-vetted PQ signature type, a commit-reveal construction, or a hybrid. But it must be usable by ordinary wallets and institutions, not just technically imaginable.
- The migration window must be long enough for real-world users. Our block space throughput estimates show that raw transaction capacity is only one bottleneck. A serious deadline must account for wallet upgrades, hardware devices, multisig coordination, inheritance, institutional controls, cold storage logistics, and fee spikes. A five-year window may sound long in software terms but may be short for global bearer-asset migration.
- The deprecation rule should be as objective and narrow as possible. Freezing by named addresses or presumed identity would be poisonous. Freezing by clearly vulnerable spend conditions is more defensible, though still controversial. Even then, designers must avoid accidentally disabling hybrid or recovery constructions that still use EC operations in non-dangerous ways.
- Frozen funds rescue options are mandatory. A permanent burn maximizes clarity but also maximizes moral injury. Temporary locks, seed-knowledge proofs, commit-reveal paths, or other non-EC ownership proofs may preserve more of Bitcoin’s property-rights ethos. The current recovery ideas are not mature enough to rely on, but they are critical because they change a binary burn-versus-steal choice into a more humane migration path.
- The community should define warning criteria in advance while accepting that perfect evidence may never arrive. A public CRQC demonstration against secp256k1 would be too late for some attack classes. But vague fear is not enough to justify burning coins. Reasonable criteria might include credible advances in fault-tolerant quantum error correction, government migration deadlines, expert cryptanalytic consensus, observed market stress, or other public signals. The NSA and NIST transitions show that major institutions already consider post-quantum migration a serious planning problem, but institutional caution is not the same as proof that Bitcoin must freeze coins now.
A Goldilocks Problem
A common critique of BIP-361 (other than “quantum computers aren’t real”) is that it is “rushed.” I think this is due to people making incorrect assumptions around activation. No one is claiming that BIP-361 should be activated today or even soon… it’s not even possible until a PQC scheme is activated. Rather, the point of BIP-361 is to have a contingency plan in place in case it looks like the threat is real and a migration becomes desirable.
We settled on a five year migration timeframe for BIP-361 because there are cons to migrating too early and to migrating too late. Migrate too early and we may be imposing great costs upon the ecosystem when it’s not necessary. Also, since post-quantum schemes and quantum safe funds rescue schemes are under active research, migrating too soon could lock us into a suboptimal solution. Migrate too late and we leave the ecosystem open to a systemic threat that could cause massive harm and loss of confidence in the network. We also know it needs to be a multi-year approach because of how long it takes for protocol changes to propagate throughout the ecosystem.
I don’t expect anyone to seriously suggest BIP-361 for activation unless it looks highly likely that a cryptographically relevant quantum computer is less than 10 years away.
Deprecation of ECC could eventually become defensible, but only as a last-resort consensus choice after a viable migration path exists, after objective rules are specified, after a long public deadline is published, and after rough consensus is achieved that allowing vulnerable coins to remain spendable via ECC would create greater rights violations than disabling it.
The most intellectually honest conclusion is that both sides of this debate are defending Bitcoin’s principles, just with slightly different interpretations. The ECC deprecation side defends protocol security, system survival, and property rights against quantum attacks. The do-nothing side defends protocol rule stability, censorship resistance, and the rights of inactive users.
The Path Forward
Bitcoin’s quantum problem is not urgent in the sense that users should panic today. It is urgent in the sense that decentralized systems must solve hard coordination problems before they become emergencies. Waiting until a quantum attacker is visible will leave us with the worst set of possible choices.
The next steps for the foreseeable future do not include BIP-361. Rather, we should focus on preparation:
- reduce address reuse
- research recovery proofs
- reduce reliance on xpub sharing
- research more optimized PQ schemes
- activate opt-in quantum safe locking scripts
- develop multiple contingency plans to prepare for various scenarios
Bitcoin’s quantum migration debate is not a choice between respecting property rights and violating them. It is a choice between competing kinds of property-rights failure. We should treat the quantum threat as a realistic but unquantifiable systemic risk, but not use uncertainty as a premise for premature controversial changes.
Even if a cryptographically relevant quantum computer fails to emerge, showing that Bitcoin takes tail risks seriously will boost confidence in the network and reduce uncertainty about its future.
This piece is featured in the latest Print edition of Bitcoin Magazine, The Quantum Issue. We’re sharing it here as an early look at the ideas explored throughout the full issue.
This post The Quantum Issue: To Freeze Coins Or Not first appeared on Bitcoin Magazine and is written by Shinobi.
CryptoSlate
Chainflip will set affected liquidity providers’ active TRON USDT balances to zero under a restart plan responding to the 736,442.17 USDT exploit it disclosed on Sept. 12.
The cross-chain swap protocol will first record each provider’s pre-migration balance separately on-chain, preserving the amount Chainflip says it owes even though the active account will read zero. Repayment remains pending.
By Sept. 16, Chainflip said swaps and quoting had resumed across the rest of the network while TRON remained excluded. The service restart leaves providers on the affected route waiting for both the accounting migration and a recovery process.
Chainflip said the attacker removed the USDT from its TRON vault between 01:44 and 03:10 UTC on Sept. 12 by causing six liquidity-provider withdrawals to be paid twice.
The attack exploited how the protocol read instructions attached to TRON transfers. Chainflip said the attacker submitted a transaction its validators had already signed and added a malformed memo. Software monitoring the transfer interpreted the memo as a failed swap and issued a refund on top of the ordinary withdrawal.
The protocol said the TRON vault now holds far less USDT than providers are owed. The restart plan therefore separates the live account balance from the amount tracked for recovery.
How Chainflip will account for the shortfall
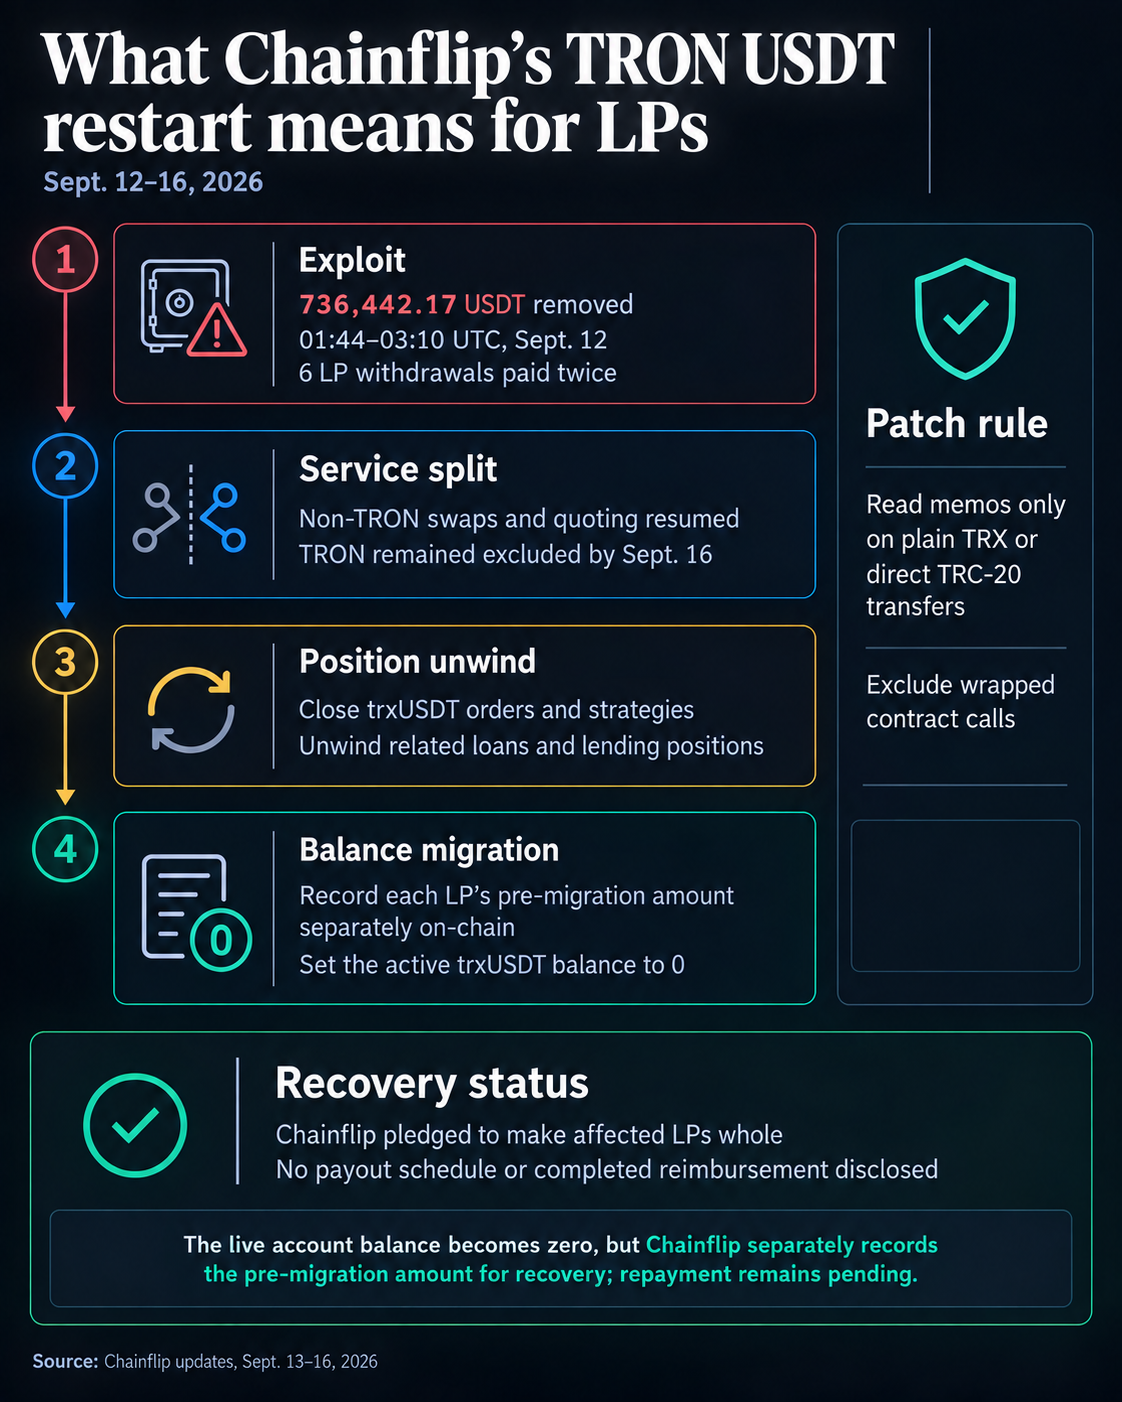
Chainflip’s migration plan calls for closing its open TRON/USDT orders and strategies and unwinding related loans and lending positions. The protocol and its software release use the label “trxUSDT” for USDT on TRON.
Each provider’s pre-migration trxUSDT amount will then be written to a separate on-chain balance before the active account balance is reset. Chainflip said this separate record keeps the amount owed available for future payouts.
The recorded amount is distinct from a completed reimbursement, and the provider’s live trxUSDT account will display zero after the migration.
Chainflip has pledged to make affected providers whole. Its public updates do not identify a funding source or payout schedule, document completed payments, or state a definitively recovered amount.
The protocol said it patched the vulnerability by limiting which TRON transfers can carry swap instructions in a memo. The new logic accepts memos attached to a plain TRX transfer or a direct TRC-20 token transfer. It excludes transfers wrapped inside another contract call, blocking the route used to trigger the extra refund.
Chainflip said all other funds were unaffected. The disclosed shortfall, position unwind, and balance reset apply specifically to trxUSDT liquidity providers.
The post Chainflip to reset TRON USDT provider balances to zero following $736,000 exploit appeared first on CryptoSlate.
Avalanche’s Helicon upgrade is scheduled to give validators shorter, auto-renewing commitments while raising the uptime cutoff for rewards and reducing returns at the shortest durations.
The network upgrade is set to activate on Avalanche Mainnet on Sept. 22 at 15:00 UTC. Validators must install AvalancheGo v1.15.0 beforehand to remain compatible with the upgraded chain.
What changes for validators
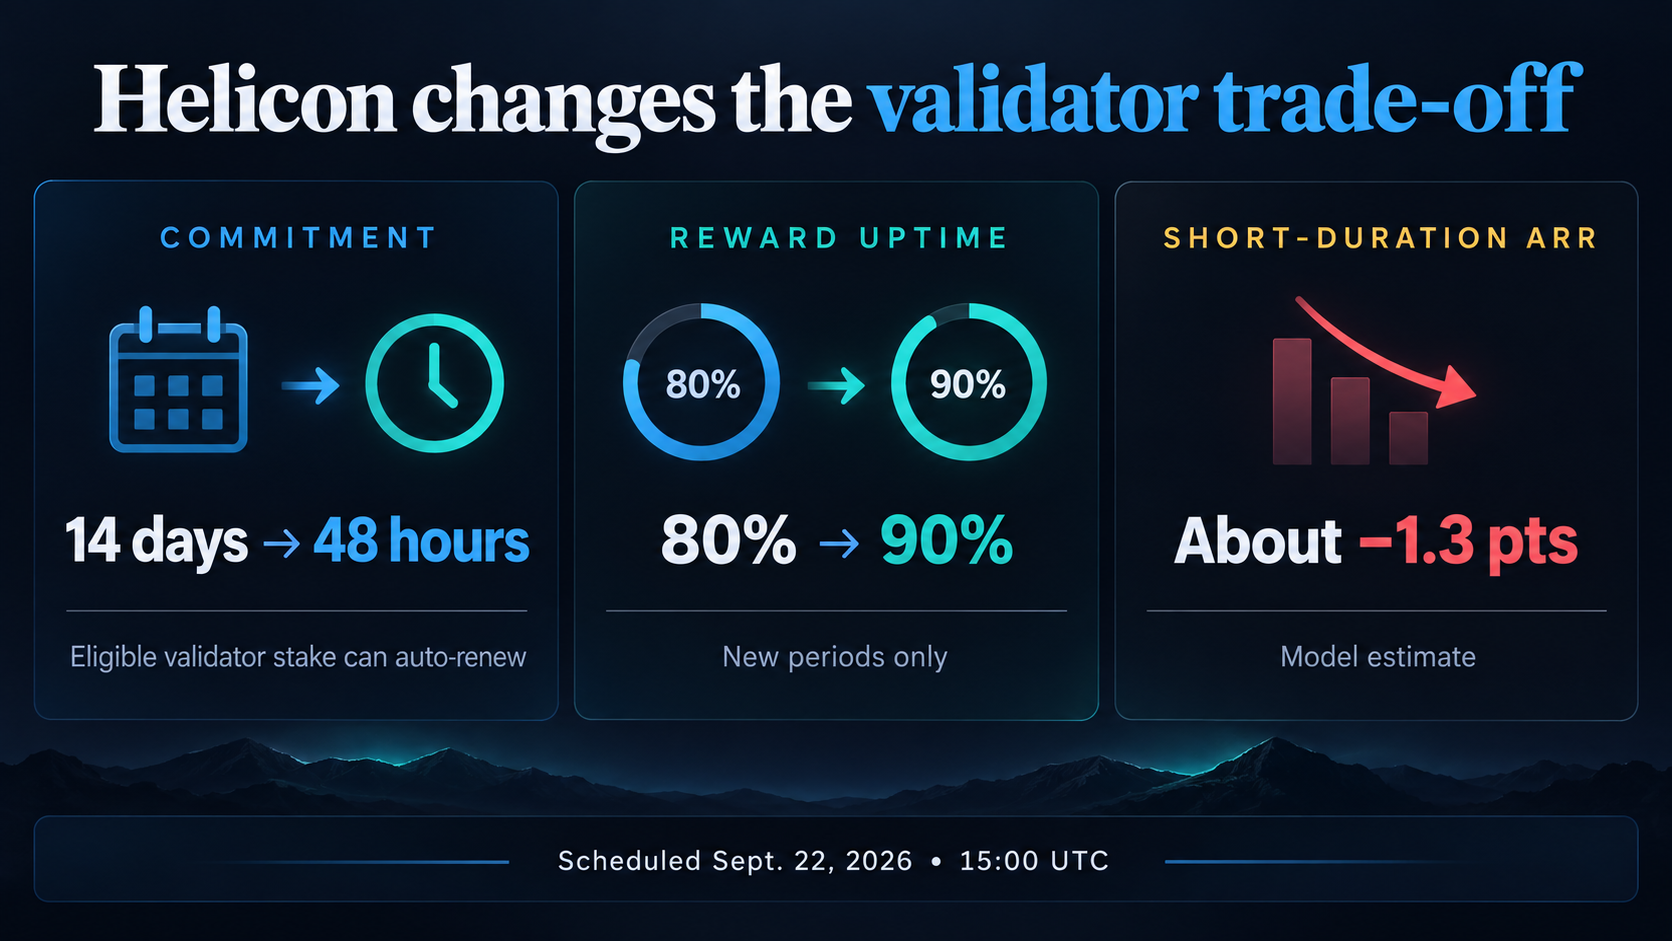
Helicon will cut the minimum Primary Network validation period from 336 hours to 48 hours. It will also let eligible validators automatically begin another cycle when the current one ends, reducing manual signing work and potential reward gaps from repeatedly leaving and rejoining the validator set.
Operators can choose how much of each cycle’s reward to compound into the next one and can update the configuration for a future cycle. That creates a way to combine brief capital commitments with continuous validation, instead of choosing between a long lockup and repeated manual restaking.
The feature applies only to the validator’s own stake. Delegations will not auto-renew, and each delegation must fit inside one validator cycle because the validator is not guaranteed to continue beyond that boundary.
Validation periods that start on or after Helicon activation must achieve at least 90% uptime to earn rewards, up from 80%. The rule is not retroactive: periods that began before activation remain subject to the existing 80% requirement even if they extend beyond Sept. 22.
Avalanche's uptime measurement will not change, and rewards will remain all or nothing. Falling below the applicable threshold forfeits the full reward for that period, though the validator’s principal is not slashed.
For a validator using auto-renewal, missing the threshold has an additional consequence. The position will not roll into another cycle, and the validator will exit. Its principal and rewards accrued in earlier cycles are returned, but the failed cycle’s reward is lost.
Short cycles reduce how long capital is committed, while the higher threshold raises the operational reliability required to collect each cycle’s reward and continue automatically. For operators, that links continuity to cycle-by-cycle performance without changing how Avalanche measures peer responsiveness or adding a partial-reward buffer.
How short-duration Avalanche rewards change
Helicon will also begin a 90-day adjustment to Avalanche’s reward curve. The protocol’s minimum consumption rate, an input that helps determine staking rewards, is scheduled to decline linearly from 10% to 7.5%. The maximum rate at the one-year duration will remain unchanged.
Avalanche’s modeling estimates that this adjustment will reduce the annualized reward rate at the shortest duration by about 1.3% after the phase-in. The exact realized yield will remain variable because it depends on factors including AVAX supply, duration, and compounding choices.
The same modeling projects annual AVAX inflation falling by roughly 0.5% to 1% and the stake-weighted average duration increasing by about two months. Those outcomes are estimates depending on how validators and delegators respond.
The mechanical trade-off is more certain: Helicon makes short, renewable validator commitments easier to use, but sets a lower reward at the short end while preserving the one-year rate and demands more reliable uptime for new validation periods.
The post Avalanche’s Helicon upgrade cuts validator lockups from 14 days to 48 hours appeared first on CryptoSlate.
Ethereum validators rely on independently built consensus clients to agree on the chain, and that diversity is a safety feature. If a defect affects a client used by too much of the network, Ethereum can stop finalizing blocks or, under more extreme conditions, finalize the wrong chain.
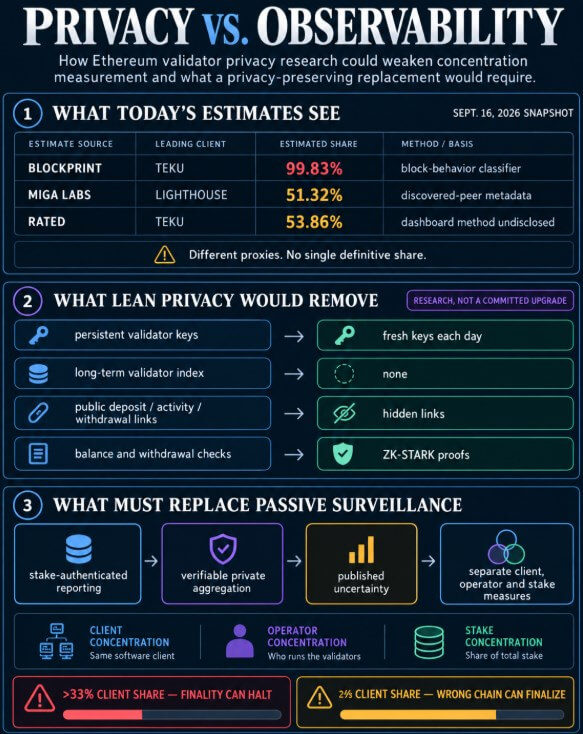
Yet a Sept. 16 snapshot of one client-diversity dashboard offered three incompatible answers about which client had the largest share. Clientdiversity.org showed Blockprint estimating Teku at 99.83%, Miga Labs estimating Lighthouse at 51.32%, and Rated estimating Teku at 53.86%.
Those are readings coming from different proxies, and one is attached to a tool its developer now calls defunct. Ethereum researchers are exploring stronger validator privacy.
A Lean-chain research proposal would use fresh validator keys each day and hide links between deposits, validator activity and withdrawals, weakening some of the traces used to measure operator and stake concentration.
The central question is whether Ethereum can replace imperfect surveillance with authenticated aggregate reporting before those persistent identifiers disappear.
Why the disputed numbers matter
Ethereum.org’s client-diversity guidance describes two distinct failure levels.
A bug in a consensus client used by more than 33% of nodes could prevent finality, a liveness failure that leaves users unable to rely on transactions as irreversible.
A critical bug in a client with a two-thirds majority could cause an incorrect split chain to finalize, a safety failure that could leave validators facing slashing or an expensive exit-and-re-entry process.
The public guidance uses node share as shorthand. Researchers seeking a consensus-risk measure care about the distribution across validators and their voting weight, because a simple count of visible machines does not show how much stake backs each client.
The Sept. 16 snapshot did not provide that clean, stake-weighted answer.
| Estimate | Largest displayed client | Displayed share | Underlying signal |
|---|---|---|---|
| Blockprint | Teku | 99.83% | Machine-learning classification from block behavior |
| Miga Labs | Lighthouse | 51.32% | Client metadata from discovered peers |
| Rated | Teku | 53.86% | Method not disclosed on clientdiversity.org |
Sigma Prime’s archived repository says the classifier is no longer accurate after Ethereum’s Electra upgrade and considers the project defunct. Clientdiversity.org nevertheless labeled the Blockprint panel as updated daily.
Miga measures a different signal. Its Ant crawler discovers peers and requests client metadata. Firewalls, refused connections, discovery gaps, and rotating peer IDs can limit coverage. One node can serve many validators, so a node sample does not reveal how much stake is behind each observation.
Rated’s documentation shows a separate attribution problem. For operator-level analysis, Rated groups validator keys by deposit address, then maps those groups to entities using transaction research, block graffiti and voluntary disclosure.
Rated says there is no standard method for that higher-order mapping. Its operator attribution is not an explanation of the client estimate displayed on clientdiversity.org, but it shows how much concentration analysis can depend on persistent public links.
Client concentration, operator concentration and stake concentration are related but not interchangeable. A large operator can diversify across clients, while nominally separate validators can share one operator, hosting provider, or software stack.
Ethereum Lean privacy would change what observers can measure
Buterin’s July research post proposes moving much of Ethereum’s per-validator accounting into zero-knowledge proofs. Under its privacy phase, the active validator registry would be rebuilt each day, validators would register fresh keys, and no long-term validator index would remain.
Balance updates and withdrawal conditions would be proven with ZK-STARKs. Deposits would use hiding commitments so a withdrawal address is not publicly linked to earlier validator activity.
Buterin described the result as strong validator anonymity. In the discussion, he also acknowledged that privacy can hide centralization, while suggesting that large operations may still leak enough aggregate data to be identifiable.
Ethereum’s broader privacy roadmap describes several protocol changes as active work or candidates under consideration, and says the roadmap is unfinished and subject to change.
Daily key changes would disrupt methods that assume a validator can be followed over time. Hiding deposit and withdrawal links would also erode deposit-address grouping used in some operator attribution.
Miga’s crawler observes network peers rather than relying on long-lived validator keys. A block classifier looks for behavior rather than identity. Neither method would automatically disappear because keys rotate, although new protocol and client behavior could make their signals less reliable.
Blockprint’s failure after Electra already shows how a protocol change can invalidate a fingerprint.
A 2025 USENIX study reported that four observer nodes located more than 15% of Ethereum validators in the peer-to-peer network during a three-day measurement. That experiment shows how network traces can reveal hosting concentration, but also why preserving those traces creates privacy and targeting risks.
A research path exists for publishing aggregate client shares without revealing each validator’s choice, but it does not yet solve authentication.
A Nethermind research project explored private voting for client reporting. Validators could encrypt their client choices, prove their ballots are structurally valid, and allow a set of authorities to recover only the aggregate. The design considered homomorphic encryption, distributed key generation, and zero-knowledge proofs.
An IETF research draft on verifiable distributed aggregation describes related cryptographic tools for private sums, histograms, groupings, and heavy hitters. These primitives can validate the form of a submitted measurement while hiding the individual input.
Multiplexed setups and distributed validators may also use more than one consensus or execution client, making an honest report more complex than a single label. Nethermind’s post identifies sampling, fake data, software attestation, decryption authorities, and performance as unresolved design questions.
Private client aggregate reporting could show whether a client crossed a warning threshold without revealing individual validators, yet still miss that one company controlled many unrelated keys. Client share and operator share need separate authenticated measurements. Neither the Lean post nor the private-reporting research specifies a complete operator-concentration system.
Ethereum can make validators more private without abandoning its client-diversity safety discipline, but measurement must become an explicit part of the privacy design. That means stake-authenticated reporting, verifiable aggregation, published uncertainty, and separate treatment of client, operator, and stake concentration.
Daily re-anonymization would expose how much the current picture already depends on incompatible estimates and public traces that privacy research is meant to remove.
The post Ethereum’s client diversity picture fractures under incompatible estimates appeared first on CryptoSlate.
Circle has scheduled the public launch of Arc for Sept. 16, giving USDC a network where the same dollar balance can fund both payments and transaction fees. That could remove a common obstacle to using stablecoins, giving Circle a possible way to attract additional USDC demand as it competes with Tether.
The public-mainnet rollout follows a private network that Circle said had more than 100 ecosystem and institutional builders in August.
Arc's public testnet opened on Oct. 28, 2025. Today's scheduled milestone is the move to a public production network, where its design can face a broader commercial test.
One balance for payments and fees
Arc is a layer-1 blockchain, meaning it operates its own network. Its documentation describes an Ethereum-compatible environment built around stablecoin transactions, with USDC as the asset used to pay network fees and transactions designed to become final in less than a second.
On many Ethereum-compatible chains, someone can have enough USDC to make a payment yet lack the separate token needed to pay the network fee. Acquiring that second asset adds another step before the payment can move.
Arc's USDC model combines those functions. A user holds USDC, sends USDC, and pays the fee from the same underlying balance. Developers can use familiar Ethereum tools while building an application whose spending and fee requirements are expressed in the same asset.
For a payment product, that could simplify onboarding and balance management. It gives USDC an operational role in every fee-paying transaction on the network, beyond being an asset an application happens to support.
The wallet integration guidance also makes clear that USDC's native and token interfaces represent the same holding. They are two ways for software to access one balance, so displaying them as separate pots of money would double-count the user's funds.
This makes the fee payable in the asset the user already intends to spend.
Arc combines open developer access with a permissioned validator set. Anyone can build applications under that model, while the operators responsible for validating the network are selected.
Circle's announced founding validator cohort includes BlackRock, DTCC, Visa, Mastercard, Standard Chartered, and other financial companies alongside Circle. That places institutional participation within the network's operating design.
For businesses considering blockchain settlement, the proposed role of those institutions is part of what distinguishes Arc. It also means that permissionless application access should not be confused with permissionless participation in validation.
The roster and private-mainnet builder count describe participation, but they cannot show how much demand a public launch will generate.
Arc also advertises opt-in privacy, but its execution documentation still lists Arc Privacy Sector and Stablecoin Services as planned and unavailable.
Arc's route to additional USDC demand
Circle reported $73.3 billion of USDC in circulation at the end of June, while Tether reported approximately $184.6 billion of USDT issued at the same quarter-end. These quarter-end figures show the difference in scale entering the scheduled launch.
Arc gives Circle a possible route to greater use: make USDC the balance that customers need for both financial applications and the transactions powering them. Payments and institutional settlement could give users reasons to keep funds available in USDC.
But additional activity on Arc and additional USDC demand are different outcomes. Moving an existing USDC balance from another chain to Arc changes where it is used, and paying fees in USDC likewise establishes a use for the token without proving a market-share gain.
The competitive test is whether easier transactions encourage customers to bring additional money into USDC and keep using it. A public network can provide the infrastructure for that change, but the launch alone cannot demonstrate it.
The post Circle opens Arc mainnet as it seeks an edge for USDC utility appeared first on CryptoSlate.
The European Central Bank has opened applications for online merchants to join a controlled pilot of the digital euro, its proposed retail central bank digital currency. The move brings the 2027 test closer to online checkout, but it does not put an issued digital euro into public circulation.
The Sept. 15 merchant call gives EU-established e-commerce and mobile-commerce businesses until 17:00 CET on Oct. 27 to apply. Applicants must serve customers across at least two euro-area countries included in the pilot and operate an active platform flexible enough to integrate the test payment flow.
The beta will not constitute the digital euro defined under the proposed EU Regulation and will not carry legal-tender status. That boundary is central to the exercise: it lets the Eurosystem test payment rails, operating processes and user experience under controlled conditions without making the instrument ordinary public money.
Testing the path from provider to checkout
Merchants selected for the pilot will need to contract and integrate with an acquiring payment service provider. The ECB selected 36 providers in July for acquiring, distributing, or dual roles, creating the network needed to connect test users with participating businesses.
In practical terms, distributing providers will give eligible users access to beta services, while acquiring providers will allow merchants to receive the test payments. This two-sided setup lets the pilot test both access to the beta service and merchant acceptance rather than treating checkout as an isolated interface.
Merchant participation is voluntary and unpaid, so the new call tests whether businesses can fit the proposed payment flow into existing online and mobile commerce operations.
The pilot's 12-month operational phase is expected to begin in the second half of 2027. The detailed schedule places operations from the third quarter of 2027 through the third quarter of 2028, after integration and testing.
Before that operating phase, merchants and providers will prepare their connections inside the controlled pilot timetable. The ECB's pilot FAQ says the operational phase could be extended by up to six months.
The exercise will inform technical work but will not decide whether to issue a digital euro. The European Parliament authorized negotiations on the proposed legal framework in July, and the legislation remained under discussion when the merchant call opened. Even after lawmakers adopt a framework, the ECB would still need to make a separate issuance decision.
The application window moves the project into a more realistic commerce test without crossing its legal or monetary threshold. Merchants can test how a possible future payment method would work at checkout, while the final design, legal basis, and decision to issue remain unsettled.
The post ECB opens merchant applications for controlled 2027 digital euro pilot appeared first on CryptoSlate.
CryptoTicker.io
Robinhood Chain went live on 1 July 2026, and the mainnet launch came with a 90-day gas rebate for transactions sent from the Robinhood Wallet (Arbitrum documented the launch itself). That window closes at the end of September; crypto.news puts the date at 29 September. After it, every transaction on the chain pays a network fee in ETH again. For the memecoins that set the tone on this chain, it is the first real stress test.
How big the chain has become
The numbers have grown sharply. On 17 September, value locked stands at around $929 million, DEX volume at roughly $1.54 billion over 24 hours and $39.1 billion over 30 days, with about $67.4 billion cumulative since launch (DefiLlama, retrieved 17 September). On 13 September it was $1.88 billion in a single day, which Bloomingbit counts as more than half of Uniswap's entire volume.
In fees, the chain took in around $7.8 million over 24 hours and $303.6 million over 30 days (DefiLlama). On 2 September, $4.01 million of chain revenue stood against $81,714 at Solana the same day (crypto.news, 4 September). Anyone reading that as Robinhood Chain overtaking Solana is comparing a subsidised launch phase with a settled network. That is precisely what this deadline is about.
Why the gas is the thing that decides it
Most of the fee-generating activity does not run through the tokenised equities Robinhood built the chain for. It runs through the memecoin launchpad Pons and through trading bots (crypto.news). Pons collected around $35.0 million in fees over seven days, $128.8 million over 30 days and roughly $151.3 million all time (DefiLlama, retrieved 17 September). Around 25,000 new tokens were created through it on 2 September alone, against an average of roughly 10,000 a day (Bloomingbit, 14 September).
An operation at that scale depends on a very low cost per attempt. Launching twenty tokens to hit one works out differently once every launch and every swap costs gas again. On top of that, the trading barely comes from the Robinhood app itself: Bloomingbit estimates its share of chain trading at one to two percent. The subsidy has therefore mostly pulled in outside usage, and that usage has no reason to stay other than the numbers.
What happens afterwards is open. There is no reliable forecast for how much activity survives, and any figure someone quotes you for it is a guess.
What it means for investors
The point that matters in practice is not a price question but a liquidity question. Memecoins on a young chain depend on thin pools. If transaction counts fall, those pools get thinner, and the gap between the quoted price and the price you actually exit at widens. That barely touches small positions and hits larger ones immediately.
How fast it moves in both directions is visible in CASHCAT, the chain's best-known token: on 3 September it set a new all-time high at around $0.3143, and on 17 September it trades near $0.1912. That is a gain of some 82 percent over 30 days and a drawdown of roughly 39 percent from the high (CoinGecko, retrieved 17 September). Both numbers describe the same token two weeks apart.
This is also where the difference between watching and trading becomes obvious: Dexscreener and TradingView give you charts, not execution. One mobile alternative is the trading app FOMO Family, which lets you discover, swipe through and trade meme and low-cap tokens directly in the app, with a fast deposit flow. Download the app through the link and you get ten percent off trading fees. There is also community speculation about a possible airdrop for active users - that is unconfirmed, the provider has promised nothing, and it is not a reason to deposit money. None of this changes the risk: meme and low-cap trading stays highly volatile, and losing the entire position is possible at any time.
What to measure in the days after 29 September
- Daily transactions. The interesting number is not the price but how many swaps are left once they cost something again.
- New tokens on Pons. If the count falls well below ten thousand a day, the supply this segment feeds on disappears.
- Pool liquidity rather than market capitalisation. Check how much actually sits in the pool and whether it is locked. At a valuation in the hundreds of millions with a few million in the pool, exiting at the quoted price is effectively impossible.
- Value locked. It sits just short of a billion dollars. Whether it stays there after the deadline is the single most honest answer to the question of whether the chain carries without a subsidy.
The background to all of this - what Robinhood Chain technically is, how the memecoin wave came about and how investors get access - is set out in full in our Robinhood Chain guide. If you are interested in how individual meme tokens are valued over a longer horizon, see our prediction pages for Pump.fun, the launchpad token Pons will most likely be measured against, and for BONK from the Solana ecosystem.
And the distinction that still holds after 29 September: memecoins are a zero-sum game in which earlier buyers' gains come out of later buyers' losses. That is not a moral judgement but arithmetic. Decide in advance what amount you could write off entirely without it changing your plans.
Disclosure: some of the providers named in this article work with us through partner programmes. This has no influence on our editorial assessment.
(As of 17 September 2026. This article is not investment advice. Prices and fee structures change; check the terms with the provider before you buy. Memecoins can lose their entire value; invest only amounts whose total loss you can absorb.)
On Friday, September 18, 2026, at around 05:01 UTC, the Solana network tightens its own beat: a slot will then last 250 milliseconds instead of 300. The switch for it is already set and takes effect automatically at the boundary into epoch 1037. For you as a holder of Solana, that mainly means three things: delegations and unstaking take effect faster, staking rewards arrive more often and in smaller portions, and the window in which a signed transaction stays valid shrinks to roughly 38 seconds. If your SOL simply sits on an exchange, you need do nothing. If you sign offline, delegate, or run a validator yourself, read this to the end.
The change is no surprise but the third step of a roadmap that began in August. The only thing new is that the 250 millisecond step now has a concrete date. Solana's official overview page still listed this step without a mainnet date when we checked on September 17, while the development team Anza had already flagged the activation as imminent on September 16. That gap between announcement and documentation is why the figure has barely surfaced so far.
What is actually being changed at Solana on September 18
A single number in the protocol is being changed: the target time for a slot. That value drops from 300 to 250 milliseconds. The number looks small, but almost everything in the network that looks like time hangs off it. Epoch length follows it, the validity period of a blockhash follows it, and the ceilings for compute per block follow it too.
The improvement proposal responsible is SIMD-0525. It describes a staircase from 400 through 350, 300 and 250 milliseconds to a target of 200 milliseconds. Two steps have already been taken on mainnet: the move from 400 to 350 milliseconds on August 19, 2026, at the start of epoch 1019, and the move from 350 to 300 milliseconds on August 25, 2026, at the start of epoch 1023. The third step is the one at issue here. A fourth is still to come after it.
What explicitly does not happen: there is no token swap, no migration, no deadline by which you would have to pull something out of a contract, and no confirmation you would have to grant in your wallet. Anyone asking you to approve a Solana upgrade wants something from you other than your consent to a protocol parameter.
Slot, epoch and feature gate: the three terms behind the date
The slot is the time window for one block
A slot is the time window in which exactly one validator may produce a block. Once it expires, the next one is up, whether the previous one delivered or not. Slot time is therefore not a speed limit for transactions but the clock rate at which the network puts out its blocks.
The epoch is the accounting period
An epoch is Solana's accounting period and covers a fixed 432,000 slots. At its boundary the network does the bookkeeping: delegations take effect, rewards are settled, prepared protocol switches are armed. Because the number of slots is fixed while the duration of a slot falls, the epoch gets shorter. At 400 milliseconds it worked out at 48 hours, at 300 milliseconds it is 36 hours, at 250 milliseconds it is 30 hours. At the final target of 200 milliseconds it lands at 24 hours.
This is the point at which the figures in circulation deserve a look: several reports give an epoch length of 24 hours for Friday's change. That is the value for 200 milliseconds, meaning the step after this one. For 250 milliseconds the same calculation gives 30 hours, and the official formula based on 432,000 slots arrives at that value too.
The feature gate is the switch with a delay
A feature gate is a switch in the validator code that keeps an already shipped function dormant until enough stake weight is behind it. When it flips, it never does so mid-epoch but at an epoch boundary. For this change the chain ran across three epochs: in epoch 1035 the switch stood at pending, in epoch 1036 it became active at protocol level, and with the start of epoch 1037 the new timing rules apply.
Why the switch flips at epoch boundary 1037 and not at midnight
Solana has no clock. The network counts slots, and a time of day can only be estimated from slots. That is precisely why every serious announcement puts an "around" in front of the time: the boundary into epoch 1037 falls on a particular slot, and when that slot is reached depends on how fast the network actually runs in the hours beforehand.
That imprecision is why two sources can say 05:01 UTC and a third 05:06 UTC without any of them being wrong. If you want something done by the exact moment, plan with an hour of buffer. If you only want to know whether you are affected, the calendar day will do: Friday, early morning European time.
Our own measurement: 317 milliseconds per slot the day before the change
cryptoticker.io collected this analysis itself on September 17, 2026. Method: ten consecutive performance samples of 60 seconds each via Solana's public mainnet node, retrieved shortly after 00:50 UTC, plus a query of the current epoch status. That covered 1,893 slots across ten minutes of network operation.
The result: on average 317.0 milliseconds elapsed per slot, with individual samples between 312.5 and 326.1 milliseconds. The value therefore sits above the current target of 300 milliseconds. That is normal and no sign of a problem. What is measured is elapsed clock time divided by the number of slots actually filled, and every slot a validator does not serve stretches that average.
The date could be recalculated from the same query. The network stood in epoch 1036 at slot 111,540 of 432,000, leaving 320,460 slots to go. At the measured 317 milliseconds that gives 28.2 hours of remaining runtime, and therefore September 18 at around 05:06 UTC. Our own calculation confirms the announced time of 05:01 UTC to within a few minutes. The node queried reported client version 4.3.0-rc.0.
What we could not check: how large the share of validators already running the recommended version is, and whether the switch actually takes effect on Friday. Both only show up after the fact. The compute ceilings mentioned further down also rest on a specialist report rather than on the official overview page.
Solana staking: what shorter epochs mean for delegation, unstaking and rewards
For anyone who has delegated SOL, epoch length is the practically most important quantity in this whole change. Delegations and their withdrawal take effect at epoch boundaries, not immediately. If the epoch shortens from 36 to 30 hours, the typical wait until a new delegation earns rewards, or until deactivated SOL is freely available again, shortens with it. How that process works in detail, and why a waiting period is not a penalty, we took apart in our article on lock-up periods and unstaking duration.
With rewards, the rhythm changes, not the amount. Payouts happen per epoch. More epochs in a year therefore mean more credits, but smaller ones. The annual yield on your delegation does not rise as a result. Anyone logging earnings by epoch gets more rows in the same spreadsheet from Friday, and anyone comparing providers by payout frequency will find the differences between the platforms in our overview of staking providers.
One common misunderstanding should be cleared up here: Friday's date has nothing to do with Alpenglow. That is a different and considerably larger overhaul of the consensus mechanism with a roadmap of its own, which we described in our article on the Alpenglow activation at the end of September. Two switches, two dates, two different sets of consequences.
Blockhash expiry at 250 milliseconds: why you have to be quicker when signing
The blockhash is the timestamp of a Solana transaction: a reference to a recently produced block that prevents the same instruction from being submitted again later. The lifetime of that stamp is measured not in seconds but in blocks. According to Solana's documentation, 151 blockhashes are valid. The documentation still converts that using the old target time of 400 milliseconds and thus arrives at roughly 60 to 90 seconds.
That span falls with the beat. At the 317 milliseconds measured today, roughly 48 seconds remain; at 250 milliseconds, roughly 38. A specialist report on the upcoming change puts the window at 37.5 seconds, which is the same calculation using 150 blocks instead of 151. The order of magnitude is the same either way: a good half minute.
This matters wherever a human being or a device stands between creating and sending a transaction. Signing with a hardware wallet burns those seconds on unlocking, paging through the display and confirming. So does preparing a transaction, then checking the address once more at leisure, and only sending afterwards. The consequence is not a lost payment but a rejected one: the network discards a transaction with an expired blockhash, and the wallet reports an error. How to tell whether such an attempt really failed or went through after all is covered in our guide to failed Solana transactions.
In practice that means: unlock the device before sending, check the address beforehand rather than inside the running window, and do not treat the confirmation dialogue as reading time. Which devices have short confirmation paths and which send you through several menus is shown in our hardware wallet comparison.
Compute limits per block fall too: what that means for swaps at peak times
Shorter blocks mean less compute time per block. So that throughput per second stays constant, the ceilings fall in the same proportion as the slot time. A specialist report on the change puts the block limit after the switch at 37.5 million compute units instead of the previous 45 million, and the ceiling for a single writable account at 15 million instead of 18 million. Those values were not on the official overview page on September 17, which is why we explicitly mark them as that report's figures.
For you as a user, the number matters less than its consequence. When a single account in heavy demand gets fewer compute units per block, transactions compete more tightly for the same pool. In quiet phases you will notice nothing. At peak times, say at the launch of a new token, the priority fee more often decides whether your swap makes it into the next block or waits. Anyone who has permanently set their fee ceiling in the wallet to the lowest possible value should know that setting before noticing it for the first time during a rush.
Validator operators: Agave 4.3 by Friday evening
Anyone running a validator has the only real deadline in this whole business. The recommended version is Agave v4.3.0-rc.1, released on September 11, 2026. Anza has asked operators to install the update by the end of Friday, meaning by the close of the same day on which the switch takes effect.
That is not an alarm but routine. Running an older version does not immediately cut you off, but it risks missing blocks once the timing rules change. For delegators that creates a quiet task: if your validator skips a conspicuous number of slots in the days after the change, the likely reason is a version that has not been installed, and your rewards fall with it.
If you only hold SOL on an exchange: why you need do nothing
For the great majority of investors the honest answer is: nothing. If your SOL sits with an exchange or a broker, their operator takes care of client versions, blockhashes and epoch boundaries. You do not have to confirm an update, change an address or meet a deadline.
Two edge cases remain. First, around a change like this a provider may pause deposits and withdrawals on the Solana network for a few hours. That is a precaution taken by the individual house and will then appear in its status notice. Second, a date like this is a well-known occasion for attempted fraud. Neither Anza nor an exchange will message you asking to enable an upgrade in your wallet.
What the official documentation does not yet say
The roadmap on Solana's site still listed the move from 300 to 250 milliseconds on September 17 as active on devnet and testnet, with a mainnet date still to be determined. The two steps already taken, by contrast, are recorded there with date and epoch. Anza's announcement of September 16 is therefore more current than the documentation page describing it.
A simple rule follows for you: go by the epoch number, not by a date in an article. The number 1037 is verifiable, and any wallet with network details, as well as any public block explorer, will show you which epoch the network is currently in. If it says 1037 or higher, the switch has flipped.
Solana slot time: what to take away
- Check by Friday morning where your SOL sits and who is responsible for it. On an exchange you are in the clear. If you delegate yourself, note that from Friday your next change to the delegation takes roughly 30 hours instead of 36 to become effective, and that your rewards arrive more often. Which platform settles how is set out in our overview of staking providers.
- Set your signing routine to a good 38 seconds. Check address and amount before you create the transaction, and only then reach for the device. If you notice in the process that your hardware wallet sends you through too many menus, it is worth a look at the hardware wallet comparison.
- Check your rewards in the week after the change. More frequent, smaller credits are to be expected; earnings that stay away permanently or drop conspicuously are not. Such a drop points to a validator not running the new version. A switch is possible at any epoch boundary, and you will find suitable places to go in the provider overview.
Sources to read up on: the official page on reduced slot times with the staged plan, and the developer documentation on transaction confirmation with the figure of 151 valid blockhashes.
(As of September 17, 2026. This article is not investment advice. Prices and fee structures change; check the terms with the provider before you buy.)
Balancer is being wound down, and two dates matter for you. The first is October 30, 2026: on that day every pool that can technically be halted is switched to "withdrawals only". The second is the end of May 2027, when the window opens for BAL holders to burn their tokens and receive a share of the organisation's assets in return. If you have money sitting in a Balancer pool, the first date is yours. If you hold BAL, both are.
The proposal has been in Balancer's governance forum since September 14, 2026, under the title "Orderly Winddown of Balancer and Distribution of the Treasury". Nothing is settled yet: token holders vote on it from September 25 to September 29. One sentence in the paper can cost holders real money, and it has had little attention so far. This article works through the proposal, from the vote to the final distribution day in July 2028.
Balancer winddown: the four dates that matter to you
Balancer is an automated market maker, a trading venue where pots of two or more crypto assets set the prices and no order book sits in between. Those pots are called pools, and anyone who puts money in is a liquidity provider. The whole thing is run by a DAO, an organisation in which token holders vote instead of a board. That DAO is now proposing to shut itself down.
The proposal's timeline spans almost two years. Four points from it you need to know:
- September 25 to 29, 2026: the vote on the proposal runs and decides everything that follows.
- October 30, 2026: pausable pools go to "withdrawals only". The bug bounty programme, under which security researchers have reported and been paid for vulnerabilities, ends the same day.
- End of May 2027: round one opens. BAL holders burn their tokens and receive their pro rata share of the assets. The window runs for six months, until the end of November 2027.
- End of January 2028: round two goes out as an airdrop to exactly those addresses that redeemed in round one. A final top-up follows at the end of July 2028.
The sentence with the largest financial effect sits in the section on BAL holders, and it amounts to this: anyone who does not redeem in round one has no share in round two. There is no latecomer rule. Let the window between the end of May and the end of November 2027 pass, and you are out of the distribution.
What "withdrawals only" means in practice on October 30, 2026
"Withdrawals only" means you can still take your balance out of a pool, but you can no longer put new money in, and swaps no longer route through that pool. The proposal describes this for pools whose contracts have a pause function. Where the contracts do not allow it, so-called recovery mode is activated, an emergency mode that keeps withdrawals open using the simplest possible method.
Pools that cannot be halted at all keep running unchanged. For those, the protocol fee is to be set to zero as far as the contracts permit. The project intends to publish how each individual pool is treated before the cut-off date. Non-pausable legacy contracts in the Balancer universe are not a theoretical concern: one of them was behind the rounding bug in the Balancer V1 legacy pools, through which roughly $234,000 drained away at the end of August 2026.
From November 1, 2026, the infrastructure is shut down. What remains, according to the proposal, is a simplified withdrawal interface, the necessary data supply and public documentation. The front end, the routing and the support you know today count as discontinued from October 30.
Non-custodial: why your pool balance does not simply disappear
Non-custodial means your crypto assets are not held by any company. Program code on the blockchain holds them, and only your key can move them. The proposal spells this out: withdrawing does not depend on Balancer, or anyone else, continuing to operate. That is the single most reassuring sentence in the whole paper, and it is also why panic is out of place here.
October 30 is therefore not a day on which money disappears. It is the day from which the convenient routes fall away. As long as the contracts stand, you can reach your balance, if necessary directly through the contract functions or through third-party interfaces that support Balancer pools. The documentation for that is due to appear while the exit window is still open. Convenient it is not, and it demands care with every transaction.
Two things do fall away, and you should factor them in. First, the interface through which you exit in two clicks today will be gone. Second, the bug bounty coverage ends on the same day, the programme that paid security researchers for reporting holes instead of exploiting them. Both argue for getting the exit done early rather than leaving it to the final week.
The vote from September 25 to 29: who votes, and what is the quorum
Voting runs through Snapshot, a method in which voting power is read off a balance at a fixed block without any blockchain transaction being needed. It costs no fees and is the standard route in decentralised finance. Balancer's voting page shows that proposals there have been running to the same rhythm for weeks, each from Friday evening to Tuesday evening.
Eligible to vote, according to the proposal, is raw BAL on every chain on which the token was issued, plus, on Ethereum, the BAL behind the 80/20 BAL/WETH pool token or locked in veBAL, each at face value. The quorum, meaning the minimum participation that makes a vote valid, stands at five million BAL. That threshold was halved from ten million to five million in August 2026; every vote since August 21 carries the new quorum in the Snapshot data.
What a no vote would mean
The proposer describes the case himself: a no would leave the existing framework standing, meaning the current mandate with its budget, the planned BAL buyback and the bounty programme. The staff terminations run out on October 31 regardless, because they were issued in August. In parallel, contributors are working on a proposal of their own to continue the infrastructure under a new name. A second proposal in the forum has been arguing since September 15 for putting part of the stablecoin holdings to work rather than distributing everything. That proposal, too, is so far only a proposal.
Liquidity providers: how to prepare your exit from a Balancer pool
If you have liquidity in a Balancer pool, your wallet holds a pool token, BPT in Balancer's jargon. That token is your share certificate in the pot, and it is what you hand back when you exit. The first step is therefore always to take stock: open your wallet and check whether positions are sitting there that you have not touched in months.
- Check what you hold. Which pool tokens sit in which address, and on which chain? Balancer was active on several networks, and a position may sit on a chain you rarely use.
- Test the exit route. Withdraw a small partial amount before the cut-off date, so you know the route works and what it costs in network fees.
- Proportional or single-sided exit? A proportional exit returns all components of the pool to you pro rata and avoids price pressure. A single-sided exit into one token alone shifts the pool's balance and costs you noticeably more in thin pools.
- Decide where the tokens go. Where do the tokens land after the exit? Anyone moving them to their own address needs custody they can handle; our hardware wallet comparison gives an overview of the devices.
A practical note on fees: small positions can founder on network costs. That applies to any exit from a contract position and has nothing to do with this winddown. If your share is worth double digits in euros and the transaction sits on an expensive chain, work out beforehand whether the withdrawal is worth doing at all.
BAL holders: burning for a treasury share, how round one works
The treasury is the organisation's asset pot. It holds a mix of several different crypto assets, and that is exactly how it is to be distributed: in kind, meaning in the tokens actually held, and pro rata, meaning by share of the circulating supply. Redeeming takes BAL irreversibly out of circulation and gives you that share in return. What you receive is explicitly not BAL.
The basis of measurement, according to the proposal, is taken at the block at which round one opens. That block is to be announced at least two weeks in advance and audited. The proposal puts the size at a minimum of nine million dollars at current prices, for the portion managed by treasury manager kpk. Further holdings at other addresses are, according to the paper, still being inventoried and are to be published in full before round one.
Three qualifications belong with that. BAL itself does not count as distributable assets. Funds recovered from the attacks on the protocol in November 2025 belong to the affected liquidity providers and stay outside this distribution. And the figure will move until May 2027 with prices, running costs and whatever still comes in.
veBAL, auraBAL, sdBAL and tetuBAL: four layers with four calendars
veBAL is locked BAL: holders who put their tokens away for a fixed period received more voting power and a larger share of the earnings in return. The proposal notes that every lock in existence today will have expired by the end of May 2027. veBAL does not unlock directly into BAL but into the 80/20 BAL/WETH pool token; that pool is to remain exitable, so you can get from there to BAL.
The wrappers built by other protocols make things messier. auraBAL and sdBAL run to the calendars of their own projects. Anyone not back in BAL by the end of round one does not redeem. tetuBAL is a special case: that lock cannot be undone and will never become BAL again. A separate rule applies to it, under which holders receive half of the amount measured at the proposal's block as BAL from the treasury when round one opens, and can then redeem like everyone else. Anyone who extends a lock after September 14 only redeems if it still expires within the window.
Price against treasury: our calculation from September 17, 2026
We pulled the market data for BAL on September 17, 2026, at 00:38 UTC. The token stood at $0.11035, which is 0.096224 euros. Market capitalisation, meaning price times circulating supply, came to roughly $7.70 million on about 69.79 million circulating tokens. For comparison: BAL hit its all-time high in May 2021 at $74.45.
That yields a calculation worth knowing before somebody else sells it to you with an exclamation mark. Nine million dollars spread across 69.79 million tokens works out at roughly $0.129 per BAL. That is around 17 percent above the price at which the token trades today. In other words, the market values the entire circulating supply below the sum the proposal names as the floor of the treasury.
The calculation is an approximation, and it can be wrong in either direction. The proposal defines the denominator more narrowly than a market data site does: the BAL held by the treasury itself is deducted, as are two holdings dating from the project's early days. A smaller denominator raises the share per token. Several points at once, though, argue against the calculation.
- The vote has not happened yet. Nothing is decided until September 29, and the proposer himself describes what a no would mean.
- More than eight months lie between today and round one. Costs run during that time, and the prices of the tokens held in the treasury move.
- Payment is in kind. You receive a basket of tokens, not a euro amount, and you have to realise that basket yourself.
- The inventory of holdings is still running. The proposal names nine million as the floor for the managed portion and holds out the complete list only for later.
- Trading in BAL is thin. In the daily window of our measurement, roughly 303,000 euros changed hands across all recorded venues.
None of this is a buy recommendation or a price target. It puts a figure from the proposal into context. Anyone turning it into a bet is betting on the outcome of a vote, on an asset statement that is not yet complete, and on a date in the year after next.
What the proposal's cost accounting shows
The proposal puts its numbers on the table, and they explain the timing. It puts total monthly costs at roughly $150,000 and protocol revenue in August at roughly $30,000, after roughly $97,000 in June. The bulk of that revenue still comes from the second protocol version, not from the new third one. For the winddown itself, roughly $150,000 is earmarked from November 1, 2026, until May 2027, then $30,000, plus a reserve of $220,000 that is only drawn on if needed.
Tax in Germany: what redeeming can mean for you
Section 23 of the German Income Tax Act applies to privately held crypto assets in Germany. A sale is taxable if no more than a year lies between acquisition and disposal; after that, the gain is tax free under the law as it stands. What matters for you is that the tax authorities treat the swap of one crypto asset for another as a disposal. That is exactly what happens in round one: BAL goes out, other tokens come in.
Three practical points follow. First, you need the acquisition date of your BAL, tranche by tranche. Second, the arrival of the basket creates a new acquisition with a new date for every token it contains. Third, the round two airdrop is a separate event for tax purposes, and its treatment depends on the circumstances. If you want to keep your history clean, you will find suitable tools in our comparison of tax tools and portfolio trackers. For an individual case, a tax adviser is the right address; this article does not replace one.
One side effect of the long timeline: exiting a pool today may already trigger a tax-relevant event, because exiting a pool token into its components can itself be a swap. That argues for documenting the exit as soon as you make it, rather than reconstructing it the following spring.
No deposit insurance, no supervision: what applies to DeFi in Germany
Balancer is not an institution supervised in Germany. There is no deposit insurance as there is on a bank account, no compensation fund and no office at which you could file a claim if a contract behaves differently than expected. That is the starting position with every non-custodial protocol, and not something that began with this proposal. The European regulation on markets in crypto assets, MiCA for short, applies to service providers, not to contracts without an operator.
In practice that means your protection consists of your own access. As long as you hold the key to the address in which the pool tokens sit, and as long as the contracts stand, you can reach your money. Lose access and there is nobody to restore it for you. Anyone who has done everything through a single interface so far should check, by now at the latest, that they know the route without it.
How this winddown fits the 2026 deadline picture
October 30 is not the only date this autumn on which holders have to act. Several trading venues have set withdrawal windows for delisted tokens that expire in October and November. If you hold several positions in different places, the best move is to pull those dates together in one spot; our overview of current crypto deadlines collects the known cut-off dates.
The difference from an exchange delisting matters, though, and with Balancer it works in your favour. At an exchange, withdrawals end on a hard date, after which you reach nothing at all without support. With a non-custodial protocol, the contract stays reachable for as long as the chain runs. The cut-off date here shifts convenience, not access.
What we checked and what remains open
For this article we worked through the full text of the proposal in the governance forum, pulled Balancer's voting history through the Snapshot interface, and collected the market data on BAL on September 17, 2026, at 00:38 UTC. The details on dates, budgets and distribution rules all come from the proposal itself.
Three things remain open. The complete statement of assets has not yet been published, the treatment of each individual pool is only due before October 30, and the specification of the redemption contract is announced for February 2027. Until then, what the proposal itself says about the figure of at least nine million dollars applies: it is an estimate at current prices, and the audited measurement on the day of opening is what counts.
Balancer winddown: what to take away
- Check by October 30, 2026, whether you are still in a Balancer pool, and exit while the familiar interface is still standing. Test the route with a small amount and decide in advance where the tokens go. If they are headed for your own custody, the hardware wallet comparison helps with picking the device.
- Put the period from the end of May to the end of November 2027 in your calendar if you hold BAL. Only those who redeem in that window are in round two as well. Have the acquisition dates of your tranches to hand; our comparison of tax tools shows what keeps that manageable without spreadsheet chaos.
- Sort out your access before the convenience goes. From November only a stripped-down interface remains, and with no operator behind you, your own key is all that counts. If you are looking for a software solution, you will find one in the software wallet comparison.
You can read the proposal in full in Balancer's governance forum; the timeline this article builds on is there too.
(As of September 17, 2026. This article is not investment advice. Prices and fee structures change; check the terms with the provider before you buy.)
An API key is not a password and not access to your account in the usual sense. It is a power of attorney with individually tickable rights that you hand to someone else's software: to the tax tool that collects your trades for the German “Anlage SO” annex, to the portfolio tracker or to the trading bot. What matters is which boxes you tick when you create it. We looked at which rights the exchanges that German investors actually use even offer, and where the dangerous defaults sit.
What an API key on a crypto exchange unlocks
An API key consists of two character strings, a public key and a secret counterpart, with which a program identifies itself to the exchange without knowing your password. That is exactly the point: because the key is an identity of its own, it also carries a set of rights of its own. A program that reads your trading history for the tax return needs read rights and nothing else.
In practice the opposite often happens. Anyone who wants to be done quickly ticks everything on offer, because it is unclear what the tool in question might want to query later. The key then sits in someone else's account for years carrying rights that were never used. For Bitcoin and every other holding on the same exchange, that power of attorney then applies just the same.
The trigger: a phishing wave in September targeted precisely these keys
On September 10, 2026, attackers gained access to customer accounts of the email service provider Brevo and used them to send messages that came out of the genuine sending routes of well-known crypto providers. Among those affected were users of hardware wallet manufacturers and of tax and tracking services. What sets this wave apart from ordinary phishing is the sender address: it was real, and the usual tells did not apply. We worked through the incident in our report on the Brevo breach and the user data affected.
For anyone who entered credentials on such a page, the providers' recommendation is unanimous: change the password, check two-factor authentication, and, if keys for a crypto exchange were stored there, revoke and regenerate them directly at the exchange. That last point regularly gets lost in the excitement, because many investors no longer know how many keys they have handed out over the years.
What we examined, and how
This analysis was compiled by cryptoticker.io itself on September 16, 2026. Method: we retrieved the publicly reachable documentation and help pages of the providers and evaluated exclusively what is stated there in plain words, without opening an account and without generating a key. Twelve pages from eight providers and tools were examined.
Three limitations belong with this, and they are not a formality. The help pages of Bitvavo and Bitpanda answered our automated retrieval with code 403 and thus block machines, not readers; we confirmed their content via the publicly indexed version. The Binance help page answered with code 202 and delivered no text that could be evaluated. And we did not measure whether the exchanges enforce the documented rights in live operation exactly as they describe them.
Kraken, Bitvavo and Binance: which rights you grant individually
The finding first: all three exchanges separate reading, trading and withdrawing into separate rights, and all three offer a restriction to fixed IP addresses. The difference lies in the detail, and the detail decides.
Kraken: the finest breakdown of the three
Kraken splits the rights further than its competitors. Kraken's help page on creating an API key lists, among others, “Query Funds”, “Deposit Funds” and “Withdraw Funds” for the money side, plus “Query Open Orders & Trades”, “Query Closed Orders & Trades”, “Modify Orders” and “Cancel/Close Orders” for trading, along with “Query Ledger Entries” and “Export Data”. Withdrawing is a tick of its own: according to the documentation, “Withdraw Funds” is needed only for the withdrawal endpoints. One setting is notable because it is missing elsewhere: Kraken allows an expiry date for the key, explicitly including short periods such as a week.
For a tax tool, the query rights together with “Query Ledger Entries” and “Export Data” are therefore enough. Everything else may stay switched off.
Bitvavo: three rights, and one sentence you should know
Bitvavo knows three rights: viewing account data and balances, trading, and withdrawing to an external address or a verified bank account. When creating the key you additionally set the IP addresses from which it is valid, and creation requires active two-factor authentication. The most important sentence on Bitvavo's help page on API keys concerns withdrawal, however: withdrawals requested through an API key bypass the two-factor prompt.
Anyone who believes the second factor catches everything when it matters is mistaken for this one route. Two-factor authentication protects your login. A key with withdrawal rights works around it.
Binance: trading rights with built-in expiry
Binance separates reading, spot and margin trading and withdrawals into switches of their own. The peculiarity is a rule that many users notice only when their bot suddenly stops: without a stored IP address, the trading right expires by itself after 90 days and is deselected automatically. With an IP restriction it stays. The withdrawal right, in turn, can only be activated at all if an IP restriction is set.
This coupling is the strictest among the providers examined, and it is a model to follow: the most dangerous right is available only together with the setting that defuses it.
Why a key without withdrawal rights can still cost you money
The obvious assumption runs: without withdrawal rights, a stolen key can do no damage. That assumption is too optimistic, and the specialist literature has contradicted it for years. Security researchers have described how attackers turn keys without withdrawal rights into money anyway: they trade the foreign balance against orders of their own in thinly traded markets. The balance never leaves the exchange, it merely changes owner at absurd prices. Two patterns keep coming up here, buying out a sell wall and deliberately bidding up an illiquid token.
Alongside that stands a more sober assessment from developer practice, which does not talk the damage down but does put it in proportion: without withdrawal rights, all a thief can do is make strange trades, and those are bad, limited in size and stoppable by revoking the key. Both views are compatible. A trading right does not prevent the loss, it limits it. A withdrawal right, by contrast, knows no limit other than your balance.
In practice that means: if you connect a trading bot, the trading right is unavoidable, and you should keep the holding on the connected account small. If you connect a tax tool, it is simply superfluous.
The IP whitelist devalues a stolen key
The IP whitelist is the most effective setting available in this context, and at the same time the one least often set. It determines from which internet addresses the key is accepted at all. An attacker who captures the character string can do nothing with it as long as he is not also sending from precisely that address. Bitvavo puts this plainly in its help pages: anyone who stores no IP list gives everyone who holds the keys the ability to trade in the account.
The catch lies in home use. A tax tool retrieves your data from its provider's servers, not from your laptop. The matching address is therefore the service's, and you have to ask them for it; reputable providers publish it. For a self-operated bot on a rented server the matter is simple, because its address is fixed. For a bot on the home computer with a changing address it is impractical, and that is exactly where the field then stays empty.
If you cannot set the IP restriction, expiry remains as a substitute. Kraken offers an expiry date for this, Binance enforces one on the trading right after 90 days. A key that is going to die in three months anyway is a considerably smaller problem than one that has been sitting in a forgotten account since 2021.
Bitpanda, Trade Republic and Bison: when there is no key to hand over at all
At the providers through which many German investors actually buy, the situation looks different, and in their favour. Bitpanda issues API keys covering trading, transactions and balances, and this access is read-only throughout. A key that knows no trading or withdrawal right at all cannot lose one either. Anyone connecting a tax tool does not have the decision to make there.
Trade Republic goes one step further and offers no official interface for retail customers. Since May 2026 there has instead been a CSV export of the transaction history that you download and upload into your tax tool. That is less convenient, because you do it by hand at every update, and safer, because no lasting power of attorney comes into being. For Bison the same route via the export applies.
There is a misunderstanding here that holds on stubbornly: the makeshift solutions from the community, meaning browser extensions and reverse-engineered interfaces, are not official access routes. They reach into the logged-in session. What you give them is not a narrowly defined right, but your entire login.
Tax tools and the German duty to cooperate
The reason so many API keys are in circulation in Germany at all is written in tax law. Anyone holding crypto assets in private wealth has to be able to document acquisition dates, acquisition costs and disposals, because the one-year period and the size of the gain depend on them. No provider produces these records by itself in the form the tax office wants to see. That is why many investors reach for a tool that collects the history and produces a statement, and that is why they hand out a key.
Which tool comes into question for this and what it costs, we broke down in our price comparison of crypto tax software; the overview of providers with their import routes sits in the hub for crypto tax software and portfolio trackers. For the security question only one thing matters: a tool that demands a trading or withdrawal right in order to calculate tax demands too much. There is no tax reason to be able to trade from inside a tax program.
A second point concerns the volume of data. A key with read rights gives the provider lasting insight into your complete trading history and your holdings. That is necessary for the calculation, but it makes the provider a rewarding target. That is precisely why the September mails hit customers of tax and tracking services and not only wallet owners.
Revoking and regenerating API keys: the right order
If you suspect that a key has leaked, a fixed order applies, and the first step belongs to the exchange. First you revoke the key in the exchange's account settings. From that moment the character string is worthless, regardless of who holds it. Only then do you generate a new one and enter it in the tool. Anyone who reverses the order and tidies up at the tool first leaves the old key running.
After that comes a look into the account history, and at two things in particular: at trades you did not trigger yourself, and at logins or accesses from unknown addresses. Conspicuous trades in thinly traded tokens are the typical pattern of the attack described above. If you find something, it belongs with the exchange's support immediately, in writing and with timestamps.
The third step is the inconvenient one: a full inventory of every key you have ever handed out. Every exchange lists the active keys in its settings, usually with a creation date and last use. Anything you cannot assign with certainty, you delete. A key that is still needed will announce itself within a few days through a tool that no longer pulls data. That is a small price for getting rid of a forgotten power of attorney.
What this analysis does not show
Honesty about the limits belongs to any survey of one's own. We read documentation, we did not measure behaviour. Whether an exchange really refuses a deselected right when it matters could only be checked with a real account and real orders, and we did not do that. Nor does this analysis say anything about how carefully the individual tax and tracking providers store the keys entrusted to them. That is the genuinely open question, and it cannot be answered from the outside.
We also did not examine the offerings that never made it into the selection because they play no notable role in Germany. The rights models there may differ. Rely therefore on the settings page of your own provider and not on an overview, this one included.
Checking your API keys: what you take away from this
- Open your exchange's API overview today and count how many keys are listed there. Anything you cannot assign to a tool in use gets deleted. Which exchange offers this overview and how clearly is set out in our hub on the best crypto exchanges.
- Take the trading and the withdrawal right away from every key that is only meant to deliver data. For a tax tool, reading is enough. Which tools get by on pure read rights is shown by the hub for crypto tax software and portfolio trackers.
- Set an IP restriction, and if that is not possible, an expiry date. With a self-operated bot the server address is fixed and the setting is done in two minutes; you will find the providers for that in the hub on crypto trading bots.
Checking the rights at your exchange takes less time than reading this text. The difference only shows on the day a mail arrives from a genuine sender address and asks you for something it must not be given.
(As of September 16, 2026. This article is not investment advice. Prices and fee structures change; check the terms with the provider before you buy.)
Straight to the point, because it is the question that brought you here: the update to BTCPay Server 2.4.4 closes the public default route to your Lightning node. It does not remove a route you built yourself. Anyone who at some point exposed their server's LND interface through their own reverse proxy therefore has two jobs: update, and take that access away again. The project behind BTCPay Server says exactly that in its announcement of September 8, 2026.
The trigger is not a fresh theft. The project is seeing automated programs probing servers on which this access has been reopened by hand. No successful takeover by this route has been reported so far, and the project draws no link to the people behind the August incident. That is the good news in this: there is a window in which the problem can be resolved without damage.
For you as a holder or a merchant, more hangs on this than a server detail. A self-hosted payment server is the point where incoming Bitcoin payments, the keys to your Lightning node and your working balance all come together. Lose access there and you lose real money, not configuration. Which puts a second question on the same desk: how much balance really needs to sit permanently on a node that hangs on the internet, and what belongs in cold storage? If you have not drawn that line yet, our hardware wallet comparison is a better starting point than any further proxy rule.
What is happening right now: bots are calling an unprotected LND endpoint
The project describes the pattern openly. Automated programs repeatedly call one particular path of the LND programming interface: the endpoint for changing the wallet password at /lnd-rest/btc/v1/changepassword. The servers affected are explicitly those on which this access was manually switched back on after BTCPay Server disabled it by default in August.
The point that makes this delicate: the endpoint requires no authentication as long as the LND wallet is still locked. That is not a bug in the narrow sense but the design of the interface. A locked wallet cannot authenticate anyone yet, so the route to unlocking and to changing the password has to be reachable without credentials. As long as that route is reachable only inside the server, it is harmless. Only publishing it to the open internet turns it into a way in.
Macaroon, LND and reverse proxy: the three terms the rest depends on
LND is one of the common implementations of the Lightning Network, the payment layer that settles Bitcoin transfers in seconds and for fractions of a cent. If your BTCPay Server accepts Lightning payments, LND is almost always what sits underneath.
A macaroon is the credential with which LND permits commands. Think of it as a key file with graded rights. The admin macaroon is the master key: whoever holds it controls the node's wallet and its payment channels.
A reverse proxy is the server process that takes incoming requests from the internet and passes them to the right internal service. BTCPay Server ships with one of its own. Many operators have set up a second one alongside or in front of it, for instance to let a mobile wallet talk to their node while they are out. That self-built forwarding rule is precisely what this is about.
Why the window after an LND restart exists at all
The sequence is unspectacular, which is what makes it effective. After every restart of LND the wallet is locked at first. BTCPay Server has an internal unlock that supplies the password automatically. Between the service starting and the moment that unlock takes effect there is a short span.
If the interface is reachable from the open internet during that span, an attacker can be faster. The project describes the consequence soberly: whoever submits the known password at that moment can set a new one and have LND issue them an admin macaroon that controls the node. From then on the master key belongs to someone else.
One detail from the past made this worse: older BTCPay installations created their LND wallets with a shared default password. So there was nothing to guess. Anyone who knew the default only had to knock at the right moment.
The August theft and the September probing are two separate events
The distinction matters, because German-language coverage stopped in August and the two events blur into one easily.
The older event, August 7, 2026. The project published a security advisory for version 2.4.2. All earlier releases contained a hole through which an unauthenticated remote attacker could retrieve LND's macaroon files. The project confirms explicitly that the hole was exploited, that users were affected and that funds were drained. BTCPay Server's own on-chain wallets were not covered by this, the hot ones included; balances in LND's on-chain wallet, by contrast, belong to the affected node. The project and supporters later offered a reward of ten percent of any recovered Bitcoin, capped at three BTC, around $190,000 at the time.
The new event, September 8, 2026. Here there is no reported damage so far. It concerns bots looking for a way in, and a precaution taken by the project. Conflating the two claims a loss that no source supports.
What the update to BTCPay Server 2.4.4 actually closes
By its own account the project tackles the sequence described above on two fronts.
First: an end to the shared password. The new LND image no longer creates wallets with a shared default password. Every newly generated wallet gets its own random password. Existing wallets still sitting on the old default are migrated automatically at startup. That removes the part of the attack which relied on prior knowledge.
Second: blocking at the network edge. The Docker setup blocks the unauthenticated routes for creating and unlocking the wallet in the bundled reverse proxy itself. Via the public default path, the restart window is now shut.
2.4.4 brought further changes that may affect you in operation even though they have nothing to do with the attack. NFC payments in checkout are now off by default and have to be switched back on in the store settings. Invoices without an amount are blocked by default. Setting up Boltcards through a card reader attached to the computer is gone; instead BTCPay Server opens the corresponding app. Anyone using the WHMCS integration needs version 4.0.0 of the plugin because of a breaking change, plus a newly generated API key. Invited store users have to accept their invitation first. And the point-of-sale module no longer allows a separate notification address per request; the one stored in the module applies.
The standard Docker setup has made a bigger jump at the same time: Bitcoin Core moves from 29.2 to 31.1, LND to 0.21.3-beta. Support for Bitcoin Knots was removed after Knots, according to the project, followed a chain that split off from the main chain. Anyone deliberately running Knots should read that before the update rather than after. On top of that comes a tighter binding to the host machine: instead of broad SSH access, the application container now only gets a key for a small list of permitted maintenance commands.
Why your own reverse proxy rule is untouched by the update
This is the core, and it is the same sentence the project already wrote in August: an update to BTCPay Server does not close access routes that you manage separately from it. A forwarding rule in your own reverse proxy, a forwarded port on your router, a Tor service you set up yourself — the update knows none of these and cannot take them back.
The project's instruction is accordingly unambiguous: do not expose the LND interface to the internet by hand through a reverse proxy of your own. If you have already done so, remove that access and update your server. Both of them, readable in that order, not as alternatives.
Anyone who was already exposed through a route of their own in August should additionally rotate their node's credentials. The update to 2.4.2 regenerated the macaroons of the standard installation automatically; that does not apply to self-managed paths. You know the same logic from the Core Lightning vulnerability at the end of August, which we took apart in this analysis of the Core Lightning hole: the dangerous assumption is never the hole itself, but the belief that a version bump handles everything that follows.
External Lightning access is back, but only with an explicit opt-in
For many operators the shutdown in August was painful, because it also removed the legitimate route: a mobile wallet such as Zeus operating your own node while you are out. The project has never disputed that and announced an orderly way back in September.
Where things stand today: a change to the routing was merged on September 11 and offers a supported option for remote access, while the interfaces of LND and Core Lightning stay off by default. That is the decisive difference from the old situation: the access exists, but you have to switch it on deliberately, and it then runs over the path the project maintains rather than over your own handiwork.
In practice that means: if you need remote access, use the switch provided and stop building a forwarding rule of your own. And take the opportunity to check which wallet on your phone should have access to your node at all. Which software wallets support which connection types is set out in the software wallet comparison linked below; not all of them come with the same permission levels, and remote access with a restricted macaroon is considerably more harmless than one with the master key.
The checklist for operators: what you work through today
In order, and regardless of whether you feel affected:
- Establish your version. The running release is shown in the footer of the admin area. If it is anything below 2.4.4, that is your first move.
- Update. On a Docker installation via Server Settings › Maintenance › Update. On an installation managed differently, by your usual route.
- Look for forwarding rules of your own. Go through your proxy configuration and watch for any rule that reaches anything below
/lnd-rest/out to the internet. Think of forwarded ports on the router and of Tor services you set up yourself as well. - Remove any routes you find. Do not comment them out and leave them lying there; take them out and reload the service.
- Rotate credentials if your node was reachable over a self-managed path. Generate new macaroons, invalidate the old ones, set up stored connections in mobile wallets again.
- Set up remote access again if you need it, through the setting provided rather than through rules of your own.
If you lack the time to do points three and four properly, the advice from the August notice still applies in spirit: a node that cannot be reached cannot be probed either. Better a few hours without remote access than an open endpoint over the weekend.
How to tell whether your LND node has been compromised
The project published a checking routine for the August incident that holds here too. Look in your node for payments you did not initiate. Watch for channel closures you did not trigger and for counterparties unknown to you. Reconcile your on-chain balance and your channel balances against your own records. Anything you cannot explain is a reason to keep looking, not a reason to relax.
One note for perspective, so that no panic arises here: a takeover by the route observed in September has not been reported by anyone so far. The check is diligence, not damage assessment.
To be considered separately is a third incident that the project discloses in the same announcement: its self-hosted server for building plugins was compromised, discovered on September 2. According to the project, only plugin developers are affected, not their users. Published plugins were checked and had not been replaced by malicious versions, and all access tokens were rotated. Stored email addresses were probably readable; anyone registered there should expect phishing attempts over the coming weeks and treat unexpected messages accordingly.
What the incident means for German merchants accepting Bitcoin payments
In Germany, BTCPay Server is used above all by small merchants, trade businesses, clubs and online shops that want to accept Bitcoin without an intermediary. The appeal lies in the payment going straight into your own wallet. There is no service provider holding the funds in the meantime.
This design has a flip side that the current case demonstrates: where nobody sits in between, there is also nobody who is liable, who blocks or who refunds. With a custodial provider an attack would be their problem. On your own server it is yours. Responsibility for updates, for access routes and for the split between working balance and reserve rests entirely with you.
From that follows a plain operating rule that holds independently of any single vulnerability: only as much sits on the node as day-to-day payment traffic requires. Everything beyond that moves regularly into storage that does not hang on the internet. Automating that outflow and running it weekly rather than quarterly caps the damage of any future incident at a manageable sum.
Records and tax: what the tax office requires for Bitcoin payments
One point that tends to get lost in security topics but will meet you at the next audit at the latest: if your business accepts Bitcoin as payment, the inflow is business income. What counts is the value in euros at the time of the inflow, and that value needs documenting. The one-year holding period of section 23 of the German Income Tax Act, which can make private sales tax-free, does not apply to business assets. Gains and losses from a later sale stay in the business and run through section 15 of the same act.
For VAT the position has been settled for some time: the European Court of Justice ruled in case C-264/14 that exchanging conventional currency for Bitcoin and back is exempt from VAT; the German Federal Ministry of Finance implemented this for Germany in a circular dated February 27, 2018. Your actual supply of goods or services remains taxable regardless of that, measured in euros.
In practice that means: for every payment you need the time, the amount in Bitcoin, the euro rate applied and the source of that rate. BTCPay Server keeps these details in its invoice data and lets you export them. Use that before a server migration or an incident renders the database unusable. That records are subject to retention requirements, and that access has to remain possible throughout the retention period, follows from section 147 of the German Fiscal Code and applies to an SQL database just as it does to a ring binder.
When running your own node pays off, and when it does not
After two security notices in five weeks, the question of whether the effort is still proportionate is a fair one. An honest answer has to name both sides.
In favour of your own node: nobody holds your money, nobody can freeze your account and no fee per transaction flows to a service provider. For small amounts on the Lightning Network that is a noticeable difference, because a percentage cut on a two-euro purchase would be out of all proportion.
Against it stands the operating effort, and that is real. You need somebody who reads security notices, applies updates and documents access routes. If that person is missing from the business, a custodial payment provider is the more honest choice despite its fees. A badly maintained node of your own costs more than any commission, and it does so exactly once.
A middle way that works well in practice: your own node for day-to-day business with a limited balance, fixed outflows into cold storage, and a calendar entry that forces you once a month to read the project's publications. All of the past weeks' notices would have been seen in time that way.
Securing BTCPay Server: what you take away from this
- Update to 2.4.4 and remove your own LND forwarding rules. The update alone is not enough if you have built a route to the outside yourself. In the same pass, cut the balance on the node down to operational needs; the rest belongs in storage without a network connection, of the kind our hardware wallet comparison sets side by side.
- Set up remote access again if you need it. Use the setting provided rather than a proxy rule of your own, and issue a macaroon with restricted rights while you are at it. Which mobile wallet handles which connection type and which permission levels is shown by our software wallet comparison.
- Secure your payment records before you start working on the server. Export the invoice data with time, amount and the euro rate applied. Anyone doing this continuously rather than once a year will find suitable tools in our overview of crypto tax software and portfolio trackers.
The two primary sources in full: the announcement of BTCPay Server 2.4.4 of September 8, 2026 and the security advisory for version 2.4.2 of August 7, 2026.
(As of September 16, 2026. This article is not investment advice. Prices and fee structures change; check the terms with the provider before you buy.)
Decrypt
The bill would exempt qualifying crypto fees from gain-or-loss calculations and restrict tax-loss deductions on tokens sold and quickly repurchased.
Meta is reportedly developing a version of its smart glasses without a camera, potentially addressing one of the biggest privacy objections to AI wearables.
An independent researcher found the agents hijacked Hugging Face accounts and mapped the platform's defenses as early as May 13—activity OpenAI's own incident report never fully described.
Chair Kevin Warsh credited Trump's economy, then ignored his rate-cut wishes entirely.
Bitcoin Core 32.0 has entered final testing, bringing faster block checks and changes to how wallets prepare payments.
U.Today - IT, AI and Fintech Daily News for You Today
Franklin Templeton’s XRPZ continues to stand out as a steady anchor for institutional demand, pulling in $3.5M in fresh net inflows even as a broader market selloff hit XRP.
Solana, XRP, Bitcoin and Tron are facing key technical levels as short-term momentum weakens across the market.
Hyundai Card is looking to take its Avalanche-based stablecoin payments experiment to the next level.
The Federal Reserve raised its benchmark interest rate by a quarter percentage point to a range of 3.75% to 4.00%.
CFTC Chair Selig urges to bypass the Senate's failed Clarity Act to launch a direct crypto regulation framework, securing the U.S. market agenda. .
Blockonomi
Key Takeaways
- Senate rejection of the CLARITY Act came Tuesday with a 49-50 vote, far below the required 60-vote threshold
- Paul Atkins, SEC Chair, promised “decisive” action through existing statutory powers regardless of congressional inaction
- CFTC’s Mike Selig declared his agency is prepared and “ready to ship its rules”
- Market analysts at Bernstein predict “aggressive and swift” regulatory actions from both watchdogs
- JPMorgan warned that agency-created regulations lack the permanence of congressional laws and face potential legal challenges
In a closely watched vote on Tuesday, the US Senate rejected the Digital Asset Market Clarity Act by a margin of 49-50, missing the required 60-vote supermajority by a significant margin. Had it passed, this legislation would have established America’s inaugural comprehensive federal framework governing digital assets.
LATEST:
Bernstein expects the SEC and CFTC to pursue "aggressive and swift" crypto rulemaking after the CLARITY Act failed its Senate cloture vote. pic.twitter.com/1bDbBGfliV
— CoinMarketCap (@CoinMarketCap) September 17, 2026
In the aftermath of this legislative setback, leadership at both the Securities and Exchange Commission and Commodity Futures Trading Commission announced plans to proceed with regulatory initiatives under their current mandates.
Paul Atkins, leading the SEC, declared the commission will “act decisively within the SEC’s statutory authority to deliver certainty for American investors.” Meanwhile, Mike Selig at the CFTC stated his organization is “locked in and ready to ship its rules for the new frontier of finance.”
Coinbase’s CEO Brian Armstrong offered a concise reaction on X: “The CFTC and SEC are stepping up. Go time.”
The Reasons Behind Legislative Failure
Democratic lawmakers primarily voted against the measure citing apprehensions regarding President Trump’s involvement in cryptocurrency ventures and ethical questions surrounding specific provisions within the proposed law. When Republicans dismissed a counteroffer from Democrats, prospects for bipartisan compromise evaporated.
A Republican Senate staffer informed The Block that the legislation appears dead on arrival. While Senator Thom Tillis maintained optimism about potential revival, Bernstein’s analytical team deemed another vote improbable given the compressed timeline before November’s electoral cycle.
According to Bernstein, this legislative defeat eliminates what they characterized as a “fool-proof” safeguard protecting the cryptocurrency sector from future regulatory reversals driven by political changes.
Expected Regulatory Framework
In a Wednesday research note, Bernstein analysts detailed anticipated regulatory actions from federal agencies. Their projections include classification guidelines for token offerings during capital formation, protective measures for developers working on decentralized finance platforms and self-custody protocols, and exemptions designed to encourage innovation in tokenized equity markets.
Additional expectations include expedited approval processes for perpetual futures contracts backed by real-world assets and modifications to regulations concerning federal sports betting markets.
The SEC had already begun moving in this direction on August 19, unveiling proposed regulations to create a “clear and fit-for-purpose framework” governing cryptocurrency investment contracts.
Under these proposed guidelines, companies could issue tokens valued up to $5 million across four years, or alternatively up to $75 million within a 12-month period. A safe harbor mechanism would provide exemptions for specific cryptocurrencies, preventing their classification as investment contracts.
Atkins had telegraphed this regulatory approach previously. During a July 27 CNBC interview, he stated the SEC stood “ready, willing, and able to come out with rules” should the Senate fail to advance the CLARITY Act.
JPMorgan’s research team concurred that both agencies will likely move expeditiously, though they emphasized that agency-promulgated regulations carry greater vulnerability compared to legislative action. Subsequent administrations retain authority to rescind them, and they remain susceptible to judicial challenges.
The trajectory for cryptocurrency regulation in America has now pivoted from Capitol Hill to federal regulatory agencies, at least for the foreseeable future.
The post SEC and CFTC to Push Forward With Crypto Regulations Following CLARITY Act Defeat appeared first on Blockonomi.
Quick Summary
- Senate cloture vote on the CLARITY Act failed Tuesday, missing the required 60-vote threshold for advancement
- According to Digital Sovereignty Alliance managing director Adrian Wall, bipartisan senators are exploring revival options
- A lame-duck session attempt remains possible, though Wall characterizes it as “a long shot”
- Wall emphasized these discussions came directly from senators rather than their staff members
- Should current efforts stall, the incoming Congress may address crypto market structure legislation
Despite this week’s Senate setback, the CLARITY Act might find a second life in Congress. Adrian Wall, managing director of the Digital Sovereignty Alliance—a nonprofit organization that collaborates with legislators on digital asset policy—shared this outlook.
During Wednesday’s appearance on Cointelegraph’s Chain Reaction show hosted on X, Wall revealed he has engaged in direct conversations with senators across the political spectrum who are considering another attempt at advancing the crypto market structure legislation before the current congressional term concludes.
“There is an appetite to put this forward even during the lame duck period of Congress,” Wall explained. “Is it easy? No. It’s going to be very complicated. It’s a long shot.”
Senate Vote Outcome
Tuesday’s cloture vote on the CLARITY Act came up short of the 60 votes necessary to advance the legislation through the Senate. Wall characterized this outcome as a “huge blow” to the bill’s prospects.
Nevertheless, Wall indicated that opportunities remain for the legislation. He underscored that his information originated from senators directly rather than through intermediary congressional staff members.
“I’ve heard it directly from senators on both sides saying they have a strategy to engage the other side and see if there’s a last chance to do it,” Wall stated.
The lame-duck session represents the congressional period following elections but preceding the swearing-in of newly elected members. This timeframe frequently serves as a final opportunity to advance legislation that stalled during the regular session.
Future Prospects
Wall maintained realistic expectations about a lame-duck revival attempt, acknowledging the challenges. Securing sufficient votes for significant legislation during this compressed timeframe presents substantial obstacles.
However, he emphasized that even if the lame-duck strategy falls short, the groundwork laid won’t be squandered. The incoming Congress could resume efforts on crypto market structure legislation from the current foundation.
The CLARITY Act has emerged as one of the most closely monitored cryptocurrency bills in recent congressional sessions. The legislation seeks to establish definitive regulatory frameworks for digital assets, particularly addressing whether they should be classified under securities or commodities law.
Such regulatory clarity has been a persistent demand from the cryptocurrency sector, which has criticized what it perceives as arbitrary and inconsistent enforcement actions by regulatory agencies.
Wall’s remarks indicate that legislative momentum around crypto market structure continues, regardless of whether the current Congress completes action on the bill.
The Digital Sovereignty Alliance maintains active engagement with both legislators and regulatory bodies on digital asset policy matters and has been instrumental in advocating for the CLARITY Act’s passage.
Tuesday’s unsuccessful cloture vote represents the latest obstacle for the legislation in the present congressional session.
The post CLARITY Act Suffers Senate Setback, but Revival Efforts May Continue appeared first on Blockonomi.
Key Highlights
- The German banking giant intends to roll out regulated cryptocurrency custody services in late 2026, awaiting final regulatory clearance
- Supported digital assets will include Bitcoin, Ethereum, USDC, EURC, and EURAU for enterprise-level clients
- With $2.217 trillion in managed assets as of June 30, Deutsche Bank represents significant institutional entry into crypto
- BaFin authorization remains a prerequisite before the platform becomes operational
- The bank’s crypto journey began in 2015, with a strategic Taurus partnership formed in 2023
Deutsche Bank, a leading European financial institution, has revealed its intention to launch regulated digital asset custody solutions for institutional investors by the end of 2026.
JUST IN:
€1.9 trillion Deutsche Bank announces it's launching Bitcoin custody services for institutional and corporate clients
pic.twitter.com/zxUwPLSH17
— Bitcoin Magazine (@BitcoinMagazine) September 16, 2026
The Germany-headquartered institution confirmed that its platform will accommodate Bitcoin, Ethereum, and multiple stablecoins such as USDC, EURC, and EURAU. Institutional customers won’t need to develop proprietary technology stacks. The bank will handle wallet administration, private key security, and external transaction processing.
With assets under management totaling $2.217 trillion as of mid-year, and an operational history dating back to 1870, Deutsche Bank represents one of the most established financial entities entering the cryptocurrency custody sector.
Germany will serve as the initial launch market. The service will cater to clients from Deutsche Bank’s Corporate Banking and Investment Banking segments, encompassing institutional asset managers, alternative investment funds, brokerage firms, custody providers, and governmental entities.
According to Gerald Podobnik, Co-Head of Corporate Bank at Deutsche Bank, digital assets should be viewed as an extension of conventional finance rather than a substitute.
Technical Safeguards and Platform Architecture
The custody platform will implement hardware-secured key management and maintain distinct hot and cold wallet infrastructures. Additional protective measures include multi-signature authorization protocols and comprehensive backup and disaster recovery systems.
Third-party technology vendors will contribute to certain infrastructure elements. While the bank hasn’t disclosed all partners publicly, Taurus and Bitpanda have been associated with the initiative in previous reports.
The digital asset portfolio may expand following launch. Any new cryptocurrency additions will undergo rigorous vetting, including market demand assessment, internal product authorization, risk evaluation, and compliance verification.
Years in Development
Deutsche Bank’s blockchain exploration began nearly a decade ago in 2015. The institution became part of the R3 blockchain consortium in 2016 and had cryptocurrency custody under internal consideration by the close of 2020.
A pivotal partnership with Swiss technology provider Taurus was established in 2023 for custody infrastructure development, coinciding with the bank’s application for German digital asset custody licensing.
Meanwhile, DWS, the bank’s majority-controlled asset management subsidiary, advanced its own initiatives. The Allunity project obtained BaFin e-money authorization in July 2025 and introduced EURAU, the euro-denominated token now included in Deutsche Bank’s custody offering.
Tokenized securities and other financial instruments are under consideration for future phases, though no specific deployment schedule has been announced.
The service remains in pre-launch status. Final authorization under the European Union’s Markets in Crypto-Assets (MiCA) regulatory framework is outstanding. Launch timing, geographical availability, and asset coverage remain subject to modification.
Deutsche Bank isn’t pioneering this territory among European banks. Standard Chartered and BBVA currently provide institutional cryptocurrency custody. Commerzbank obtained its BaFin crypto custody authorization in 2023.
However, Deutsche Bank’s institutional footprint elevates the significance of this development. When a financial institution managing more than $2 trillion begins offering Bitcoin and Ethereum custody, it represents meaningful progress in integrating cryptocurrency into established institutional finance.
The post Deutsche Bank Set to Offer Bitcoin and Ethereum Custody Services in 2026 appeared first on Blockonomi.
Key Takeaways
- On September 16, the FCA released comprehensive guidance detailing which cryptocurrency operations require authorization under Britain’s forthcoming regulatory structure
- The application window opens September 30, while the complete regulatory framework becomes operational October 25, 2027
- Current registrations and existing permissions won’t automatically transfer into the new authorization system
- Companies wanting transitional accommodations face a February 28, 2027 application deadline
- International operators, including American firms with UK clientele, may require FCA authorization
Britain’s Financial Conduct Authority unveiled comprehensive guidance on September 16, clarifying which cryptocurrency business activities will require formal authorization when the country’s new regulatory framework launches in October 2027.
The regulatory guidance encompasses numerous business activities, including stablecoin issuance, operating digital asset exchanges, dealing in cryptocurrencies, facilitating transactions, providing cryptoasset custody services, and administering staking programs.
According to the FCA, companies cannot simply depend on their own business descriptions. The regulator will evaluate authorization needs based on the actual functions and services a firm provides.
Current Licenses Won’t Automatically Transfer
A critical consideration for companies currently operating in Britain: existing FCA registrations and regulatory permissions won’t automatically migrate to the new authorization framework.
Businesses registered under Britain’s anti-money laundering regulations must also undergo the new authorization procedure. Those existing registrations serve a more limited purpose and won’t satisfy requirements under the forthcoming framework.
Organizations holding different regulatory authorizations may need to request permission modifications if they intend to conduct regulated cryptocurrency activities.
“Preparing for regulation begins with comprehending how this framework impacts your operations,” stated David Geale, who serves as the FCA’s executive director overseeing consumers, payments and competition.
Critical Dates for Crypto Businesses
The application portal launches September 30, providing businesses more than a year for preparation before the framework’s October 25, 2027 implementation date.
However, organizations seeking transitional arrangements must meet an earlier February 28, 2027 submission deadline. Failing to meet this date could result in forfeiting access to transitional provisions.
The FCA completed the majority of its regulatory package in June after multiple industry consultation rounds. The Financial Services and Markets Act 2000 (Cryptoassets) Regulations 2026 received Parliamentary approval in February.
The finalized regulations address stablecoin reserve requirements and redemptions, cryptocurrency custody standards, operational resilience expectations, consumer protection measures, and capital adequacy requirements. Additional regulations tackle token listing procedures and misconduct prevention on trading platforms.
The FCA intends to seek feedback on modifications concerning stablecoins, proprietary trading operations, market making activities, and certain technology service providers in October. Decentralized protocol frameworks and specific custody structures will undergo additional examination.
International Firms Face Requirements
American companies serving British clients or conducting operations in the UK market may need FCA authorization, regardless of existing US licensing.
Regulatory approval from the SEC, CFTC, or state-level authorities doesn’t substitute for FCA authorization when conducting regulated activities in Britain. The United States and United Kingdom are following distinct timelines with separate legislative frameworks.
During September, the House of Lords approved an amendment by a 194 to 138 margin mandating the Treasury publish a comprehensive national digital asset strategy within twelve months of the Financial Services and Markets Bill’s enactment.
The FCA and Bank of England additionally plan to release a tokenization roadmap for wholesale financial markets before year’s end.
The post FCA Warns Crypto Companies: Registration Alone Won’t Cut It Under New Rules appeared first on Blockonomi.
Key Takeaways
- Al-Qassam Brigades instructed potential donors to steer clear of Binance for cryptocurrency donations
- Alternative platforms suggested included Trust Wallet, Bybit, OKX, Kast and Redotpay
- Instructions specified using USDT on TRC-20 through an external TRON wallet
- Binance claims the advisory demonstrates the effectiveness of its compliance framework
- OKX stated the wallet in question was already identified by their monitoring systems
According to U.S. Department of Justice asset-forfeiture documents filed on September 9, 2026, the Al-Qassam Brigades—the armed faction of Hamas—instructed prospective contributors to bypass Binance when transmitting financial support to the organization.
Communications attributed to the Al-Qassam Brigades identified several alternative platforms: Trust Wallet, Bybit, OKX, Kast and Redotpay. Contributors received instructions to transfer USDT stablecoin via the TRC-20 network to a separate TRON wallet address.
The court documents provide unusual insight into operational tactics employed by a designated terrorist organization attempting to circumvent financial surveillance. The communications explicitly warned contributors against including any identifying information or official names in transaction metadata, citing security risks.
The instructions did not entirely prohibit Binance usage. According to the letter, contributors could purchase cryptocurrency through Binance but were directed to route those assets through alternative applications before finalizing transfers to the designated address.
Crypto Platforms Respond to Allegations
Noah Perlman, Binance’s chief compliance officer, characterized the Hamas advisory as evidence supporting the platform’s security measures. “When terrorist organizations advise their networks to avoid Binance, it demonstrates our controls are functioning as intended,” he stated.
OKX representatives clarified that the wallet address cited in February 2025 correspondence had zero association with their exchange. According to the platform, their internal monitoring infrastructure had previously identified and flagged the address for suspected illicit connections prior to the public disclosure of court documents.
Kast representatives noted that all users undergo comprehensive identity verification and screening protocols before gaining platform access. The company disclosed it employs compliance technology from Elliptic, Sumsub and Sardine for sanctions screening and ongoing transaction surveillance.
Bybit representatives declined to provide comment. Redotpay did not respond to inquiries.
Inclusion in such communications does not necessarily indicate deficient compliance infrastructure or intentional facilitation of prohibited transactions by any named entity.
Context of U.S. Enforcement Actions
This revelation emerges amid intensified U.S. regulatory focus on cryptocurrency-related terrorist financing, particularly following Hamas’s October 7, 2023 assault on Israel.
Previous reporting by The Wall Street Journal indicated that digital wallets associated with Hamas accumulated approximately $41 million between 2020 and 2023. U.S. Treasury Department investigations examined roughly $165 million in cryptocurrency-related transactions potentially connected to Hamas financing operations prior to the 2023 offensive.
The Treasury Department’s 2026 terrorist financing risk assessment acknowledged continued digital asset utilization by Hamas and ISIS. Nevertheless, the assessment emphasized that conventional financial infrastructure remains the predominant conduit for terrorist financial operations worldwide.
This case underscores persistent difficulties cryptocurrency exchanges encounter in blocking sanctioned entities from platform access, regardless of whether platforms are implicated as willing participants.
U.S. enforcement authorities maintain active surveillance and seizure operations targeting digital assets connected to entities appearing on sanctions lists.
The post Hamas Directed Crypto Donors Away From Binance to Bybit and OKX, DOJ Files Show appeared first on Blockonomi.
CryptoPotato
Bitcoin’s expected price volatility ahead of and after the FOMC meeting indeed took place, with the asset posting a few major moves, but it has overall survived the first rate hike in three years, currently trading above $76,000.
The altcoins are also well in the green today, with SOL touching $100 and ZEC exploding by over 14%.
BTC Above $76K as the Dust Settles
The current business week was expected to be a big one for the cryptocurrency industry, and it was quite eventful, even though it’s far from over. At the end of the previous one, BTC plunged to $76,000 after the release of the CPI data, before it suddenly rocketed to almost $80,000, where it was rejected and driven south to $77,000. It spent the weekend there and dipped again on Monday to $76,500.
However, the bulls went on the offensive later that day and pushed the cryptocurrency to $79,500. Another rejection followed as the market braced for the upcoming cloture vote on the CLARITY Act. The Senate vote ultimately failed, and BTC went from $77,250 to a month low of $75,000 in minutes.
It recovered to $76,000 on Wednesday as all eyes turned to the Fed. For the first time in three years, the US central bank raised the rates unanimously with a 12-0 vote. At first, BTC dipped to $75,000 before it shot up by $1,500. It failed there again, slipping by a grand before it rebounded and now sits at $76,500.
Its market cap has recovered to $1.530 trillion on CMC, while its dominance over the alts has retreated slightly to 58.7%.

ZEC Flies Again
Ethereum is up by just over 1.5% daily and sits close to $2,450. BNB has posted a similar increase, currently trading at $725. SOL has neared $100, while XRP, TRX, HYPE, DOGE, and LINK are also in the green. ZEC stands in a league of its own again. The privacy token has rocketed by over 14% and now trades above $1,350. In contrast, RAIN has plummeted by nearly 8%.
NEAR, CRO, PUMP, UNI, CC, DOT, ENA, and ONDO are well in the green among the larger-cap alts, with gains of up to 14.6% in the case of NEAR.
The total crypto market cap has increased by over 1% daily, and it’s up to $2.610 trillion on CMC.

The post Bitcoin Survives First Fed Rate Hike in 3 Years, Zcash Explodes Again: Market Watch appeared first on CryptoPotato.
XRP’s recent 70% rally may have had an early on-chain signal. Santiment found 85 new wallets holding at least 1 million tokens appearing just two days before the August 17-21 surge.
That matters because these larger wallets can absorb supply and strengthen bids while shifting liquidity faster than retail traders. Changes in their numbers have often appeared ahead of XRP’s sharpest moves.
Millionaire Wallets Were Already on the Move
There is also more happening around the XRP Ledger. Ripple backed an RLUSD credit fund focused on fintech and payments lending on XRPL. ZILO and Licuido investments brought tokenization plus transfer-agency and collateral-mobility rails into Ripple’s stack.
Looking toward the rest of the year, Santiment considers the setup to be constructive. Whale wallet numbers remain high, while RLUSD adds settlement utility and institutional tokenization gives XRP a story beyond retail hype.
Separately, AI is also moving further into Ripple’s treasury operations. Just last week, the company announced expanding GSmart to handle a wider range of work for enterprise finance teams. The new capabilities cover forecasting, liquidity, risk, reconciliation, and reporting, and are already being used by Ripple’s enterprise customers.
Despite the gains it had made previously, XRP took the biggest hit among major cryptocurrencies following the Senate’s failure to move the CLARITY Act forward. This is a major blow to an industry that has spent years pushing for a comprehensive US regulatory framework. Over the past day, the token has shed more than 8%.
The broader crypto market was awash in red by Tuesday afternoon as well.
Bullish Setup Takes a Hit
Crypto analyst Diana said XRP could face further downside after the token lost the $1.34 support level and fell quickly toward $1.26. The move weakened its earlier bullish setup, which had pointed toward the $1.70-$1.78 range. The bulls now need to defend the $1.24-$1.26 area.
If that level fails, the analyst said that $1.14-$1.10 could come into focus, followed by the $1.00 mark if XRP drops below $1.1. Diana also flagged that its one-hour RSI had fallen close to 21, which put the token in deeply oversold territory. That could trigger a short-term bounce.
On the institutional front, US-based spot XRP ETFs continued to attract capital. So far in August, they have raked in over $43 million in inflows. If the trend continues, these funds could extend their inflow streak to 10 consecutive weeks.
The post XRP’s 70% Breakout Had a Warning Sign: 85 Millionaire Wallets Moved First appeared first on CryptoPotato.
Trader Matthew Hyland says Bitcoin is sitting at a daily cycle low with a bullish divergence forming on the charts, and he’s calling for prices above $90,000 by early November.
He’s making that call even as BTC trades near $76,000, down sharply since the Senate failed to advance the CLARITY Act, and while most of the market’s loudest voices are still leaning bearish.
One Analyst Sees a Bottom, Bears See a Trap
Hyland posted on X that bears were getting excited right at what he considers a daily cycle low, with a bullish divergence setup forming underneath the price action.
“See ya at $90k+ by early November,” he wrote.
Swing trader Roman replied, “Yeah, part of me really thinks this was a low,” with Hyland acknowledging that the RSI could fall further, although he pointed to liquidity around $75,000.
“So far it was just a liquidity grab IMO,” he stated, adding that there was “not really much liquidity below” that level. Additionally, he said current prices look solid to him, even though most bears still aren’t buying it and are hoping for a much deeper decline.
That view runs against more pessimistic calls on X, including from analyst Ted Pillows, who pointed out that BTC has lost its 50-week EMA and wrote that “a drop to $70K-$72K zone is highly likely before any reversal.”
Fellow market watcher Crypto Patel has been calling the bearish move since Bitcoin fell from $82,500 to about $74,900 after being rejected near an $83,000 bearish order block on the daily chart, and he’s holding a $50,000 target unless Bitcoin closes above $83,000 on a higher timeframe.
Meanwhile, CryptoQuant contributor IT Tech took a different approach, focusing on Bitcoin holdings rather than price structure. They pointed out that the 6- to 12-month supply band has climbed to 30.8% of realized cap, up from 16.2% in December last year, a pattern that lined up with the last three Bitcoin bottoms.
The analyst called it a bullish setup but stopped short of calling it the cycle low outright, noting that the OG cryptocurrency is still down nearly 40% from its peak and that “this reads as mid-cycle floor building, not the cycle low.”
Bitcoin’s Price Action and the CLARITY Act Fallout
BTC was trading near $76,000 at the time of writing, down about 1.5% in 24 hours and nearly 5% over the past week, although it’s still up close to 19% across 30 days.
The drop follows Tuesday’s Senate vote, when cloture on the CLARITY Act failed to gather the 60 votes needed to move the bill forward. As CryptoPotato reported earlier, Bitcoin short-term holders sent more than 23,000 BTC to exchanges at a loss in the aftermath, worth close to $1.8 billion, marking the largest capitulation event in about a month.
The post Analyst Says This Setup Could Send Bitcoin Above $90K by November appeared first on CryptoPotato.
Solana is holding a major support area even after its latest correction. After reports that the CLARITY Act failed to advance in the US Senate, the crypto asset took a plunge from over $101 to under $96 before a minor recovery.
Ali Martinez found that 72 million SOL previously traded around this level, which makes the zone significant.
Other Signals
Institutional demand is also strengthening through US spot SOL ETFs. It has now recorded nine straight weeks of net inflows, and more than $200 million entered these investment vehicles over the past month. Almost $28 million in inflows were recorded in August alone.
At the same time, exchange supply continues to fall as more than 3 million SOL have been withdrawn from exchanges during the same period.
Network activity remains elevated as well. Solana reached a peak of 12 million new addresses on September 11, and it is still adding roughly 10.8 million new addresses each day. According to Martinez, these factors – the strong support level, ETF demand, lower exchange supply, and continued network growth – indicate that the current correction could be short-lived.
Solana has been seeing growing activity from tokenized stocks, especially after traditional markets close. CryptoRus recently said that 63% of the network’s tokenized-equity activity happens after Wall Street closes. There are now more than 727,000 holders. Additionally, Solana’s TVL rose more than 18%, from around $4.82 billion to roughly $5.7 billion.
Corporate treasuries are building exposure too. DeFi Development Corp. now holds about 2.39 million Solana tokens and SOL equivalents after adding 55,491 since August 27. It has also established a $300 million at-the-market program for its CHAD perpetual preferred stock.
Most of the proceeds will be used to purchase more of the crypto asset. CHAD carries an initial annual dividend rate of 13%. DeFi Development Corp. recently restarted regular purchases of SOL and now has the second-largest Solana treasury, behind Forward Industries.
Volatility Incoming?
Despite the recent choppy price, SOL is almost 30% up over the past month. Market watcher Ella believes that a move back above $100 would take some pressure off the crypto asset. The focus should be on reclaiming $102.5.
However, if $95 breaks, the price could fall toward $93-$94. With the Fed decision still ahead, Ella expects volatility to pick up.
The post Solana (SOL) Correction or Short-Lived Dip? Here’s Why Bulls Aren’t Giving Up appeared first on CryptoPotato.
The world’s largest cryptocurrency exchange will end support for several trading pairs across its margin and spot sections.
Many of the involved digital assets have entered red territory today (September 16), but is Binance the sole reason for their poor performance?
The Upcoming Delistings
The company conducts periodic reviews of all listed trading pairs on its platform and removes those that no longer meet key criteria, such as adequate liquidity, solid trading volume, development activity, and more.
Based on this research, it will delist the following cross-margin pairs: ENJ/USDC, GENIUS/USDC, CVX/USDC, and VANA/USDC, as well as the isolated-margin pair GENIUS/USDC.
The actual removal is scheduled for September 18. On the same day, the exchange will terminate access to the BREV/USDC, COOKIE/USDC, LA/USDC, and QNT/USDC spot trading pairs.
“The delisting of a spot trading pair does not affect the availability of the tokens on Binance Spot. Users can still trade the spot trading pair’s base and quote assets on other trading pair(s) that are available on Binance,” the entity clarified.
Most of the cryptocurrencies included in the delisting efforts have posted daily losses, yet Binance doesn’t seem to be the main culprit behind the decline. Perhaps the main factor is the overall market correction, caused by the CLARITY Act failure.
Binance remains a behemoth in the industry and can trigger a major crash, but that typically happens when it terminates all trading services for certain tokens, not just trading pairs. Such was the case in August this year when it said goodbye to Across Protocol (ACX), Hashflow (HFT), PIVX (PIVX), Vulcan Forged PYR (PYR), Vanar (VANRY), and Viction (VIC). All affected coins plunged by double digits after the news.
On the other hand, Binance support can drive a substantial price pump. Just a few weeks ago, the exchange added PONS to its Binance Alpha section, thus contributing to the token’s rally and its brief entry among the top 100 cryptocurrencies.
The Scam Warning
In addition to updating its platform, Binance recently issued a critical scam alert about phishing attacks targeting crypto investors. The team disclosed that attackers send fake text messages that seem official, such as “Your account settings were changed: or “Suspicious login detected,” to trick users into clicking malicious links that could result in painful losses.
“Remember: Binance will never ask you to tap a link in a text message to “verify” or “secure” your account,” the company emphasized.
It also outlined steps that could improve protection. People should never click on unfamiliar links, turn on Withdrawal Address Whitelist in the security settings, and enable Anti-Phishing Code.
The post Binance Unveils Multiple Delistings: Check Out the Affected Cryptocurrencies appeared first on CryptoPotato.