Cryptocurrency Posts
Crypto Briefing
Global currency dynamics may shift significantly, impacting trade balances and economic strategies amid central bank policy decisions and geopolitical tensions.
The post Dollar firms, yen wobbles ahead of Fed and BOJ decisions appeared first on Crypto Briefing.
ECB Governing Council member Martins Kazaks says the 2.5% deposit rate is not a ceiling as euro area inflation holds at 3.3%, signaling more
The post European Central Bank’s Kazaks signals more rate hikes ahead as inflation lingers at 3.3% appeared first on Crypto Briefing.
City's win highlights their dominance and resilience, deepening United's struggles and potentially impacting managerial and team morale.
The post Manchester City wins at Old Trafford despite red card appeared first on Crypto Briefing.
The push to slow AI development by Anthropic and OpenAI may impact their market valuations and influence future tech policy dynamics.
The post Anthropic, OpenAI push to slow AI development, clash with Trump admin appeared first on Crypto Briefing.
The "Greater Israel" concept's rise may hinder U.S. recognition of Palestine, impacting regional stability and international diplomatic relations.
The post “Greater Israel” concept gains attention amid Israel-Hamas conflict appeared first on Crypto Briefing.
Bitcoin Magazine
Bitcoin Magazine

Bitcoin’s ‘Unusual Mix’: Bearish Inflation Print, Bullish Buyback Failure
Bitcoin’s path higher just got harder in the short term, but the setup further out may be improving, according to a new report.
In a Friday note, European asset manager CoinShares’ Head of Research, James Butterfill, said firmer-than-expected core inflation raises the odds of tighter Fed policy and could cap bitcoin below $80,000 for now.
But the longer-term case, he argued, rests on the U.S. Treasury’s bond buyback programme failing to bring down long-end yields — a failure that could ultimately feed the debasement narrative that has supported both bitcoin and gold.
“The result is therefore a somewhat unusual policy mix for Bitcoin,” the report read. “Today’s CPI data is negative at the margin, increasing the probability of tighter monetary policy and potentially limiting the immediate upside.
“But the apparent failure of the Treasury’s current buying programme increases the likelihood of much more substantial intervention further ahead.”
It continued: “If that happens, it could become one of the more powerful medium-term catalysts for Bitcoin.”
Data on Friday revealed that the consumer price index, excluding food and energy, climbed 0.3% in August from a month earlier — higher than expected.
According to CME’s FedWatch tool, traders think there is a 85% chance interest rates will be higher after the Federal Reserve meets next week. Bitcoin has typically performed well in a low interest rate environment.
But the U.S. Treasury’s expanded bond buyback programme has so far failed to materially suppress long-term yields.
If yields stay stubbornly high, Butterfill said, pressure will build on Treasury Secretary Scott Bessent to escalate to a much larger, “bazooka-style” buying programme aimed at forcing borrowing costs down.
Bitcoin in August had one of its best runs in years after Treasury Secretary Scott Bessent announced the department would double the size of its long-dated bond buybacks.
The announcement and subsequent price surge has led some to say the much talked-about debasement trade is back. The so-called debasement trade is when investors buy an asset as a way to hedge against a currency losing value.
Bitcoin and gold have both benefited as part of the trade as the dollar weakens.
This post Bitcoin’s ‘Unusual Mix’: Bearish Inflation Print, Bullish Buyback Failure first appeared on Bitcoin Magazine and is written by Mathew Di Salvo.
Bitcoin Magazine

Blockstream Tells Hackers To Return Remaining Bitcoin Stolen in Liquid Theft
Bitcoin infrastructure firm Blockstream has refused to negotiate further with hackers who last week stole 4,000 bitcoins from its Liquid network.
Writing on X Friday, Blockstream said that the hackers still had time to return the funds before the company would work with law enforcement.
White-hat hackers on Sunday withdrew about $320 million from the federation wallet that backs Liquid, a sidechain by Blockstream. After negotiating with Blockstream, they returned most of the funds but kept 598.5 coins worth over $46 million — demanding it as ransom.
“Blockstream will not pay a ransom for the return of stolen funds,” the post read. “Taking assets without authorization and withholding their return is a crime, not responsible disclosure. It is not white-hat activity. It is theft.”
It added: “We will work with law enforcement, exchanges, service providers, forensic specialists, and other relevant parties to trace and recover the assets and identify those responsible.”
“We will not pay for the return of stolen property. We will not abandon our users. The Bitcoin community will not stop pursuing the funds.”
Liquid, or L-BTC, is a layer-2 created by Blockstream that allows users to fast move assets backed 1:1 with bitcoin. One of the assets, LBTC, is a token backed by bitcoin that allows for quick settlement — a bit like the Lightning Network.
Hackers were able to get the funds by exploiting an inflation bug on the Liquid sidechain to create over 4,000 LBTC that did not exist before and cash them out for real, on-chain bitcoins.
The hackers then had an exchange with Blockstream via messages written into Bitcoin blocks.
In one message, the white hats wrote: “Please fix the bug first. The chain is under risk at latest commit right now. Make sure every node is patched. Then we will transfer the money back safely after confirming the fix.”
In the latest message, the hackers slammed Blocksteam as “delusional, greedy, and arrogant,” and threatened to reveal all of Blockstream’s encrypted messages in the exchange unless the company allowed thieves to keep 10% of the bitcoins.
“You SHALL pay 10% using your own money as bug bounty or you will cause all your holders a 15% loss for your irresponsibility and stinginess,” the message read.
The Bitcoin community is still reeling after hackers in July were able to steal over 1,800 bitcoins worth close to $140 million from Coldcard wallet holders.
Users of the popular hardware wallet, created by Coinkite, were targeted because the product’s manufacturer did not use a true random number generator, allowing hackers to essentially guess investor seedphrases.
This post Blockstream Tells Hackers To Return Remaining Bitcoin Stolen in Liquid Theft first appeared on Bitcoin Magazine and is written by Mathew Di Salvo.
Bitcoin Magazine

Italy’s Second Biggest Bank UniCredit Is Weighting up Crypto Custody: Report
Italy’s second largest bank is considering expanding into digital asset offerings, including custody, according to reports.
According to a Friday Bloomberg report citing people familiar with the matter, Milan-based UniCredit is selecting a technology provider that would allow it to build the infrastructure needed to hold digital assets and facilitate their buying and selling.
Bloomberg’s reporting added that tokenized investment products and fixed-income securities, the use of stablecoins and exposure to cryptocurrencies were all on the cards.
JUST IN:
— Bitcoin Magazine (@BitcoinMagazine) September 11, 2026Italy’s 2nd-largest bank UniCredit is considering to offer crypto asset custody — Bloomberg
pic.twitter.com/NAZKJBdcES
The news comes as other banks in Europe expand crypto offerings. Spain moved first on retail, with BBVA rolling out bitcoin trading and custody to all customers via its app, using its own custody infrastructure rather than a third party; Santander’s Openbank followed with its own trading service.
Cecabank — a Spanish custodian with over €400bn under management that acts as backbone for 100+ financial institutions — went live with crypto custody in June via a partnership with Bit2Me.
And in Germany, Deutsche Bank is building custody with Bitpanda’s technology arm, while Taurus and DZ Bank got BaFin approval in January for its meinKrypto platform.
New regulation in the European Union — Markets in Crypto-Assets Regulation (MiCA) — gives banks a legal definition, a supervisor, and a familiar set of obligations to launch crypto services.
UniCredit is one 37 lenders across 15 European countries working together to create a company called Qivalis with the aim of issuing a euro-denominated stablecoin.
Last year, the bank said it was offering professional clients a structured product tied to BlackRock’s iShares Bitcoin Trust exchange-traded fund, with full protection against losses.
This post Italy’s Second Biggest Bank UniCredit Is Weighting up Crypto Custody: Report first appeared on Bitcoin Magazine and is written by Mathew Di Salvo.
Bitcoin Magazine

Government Defeated as Lords Back UK Digital Assets Strategy
The UK government suffered a defeat in the House of Lords on Wednesday as peers backed an amendment requiring the Treasury to draw up a national strategy for regulating digital assets.
The upper chamber approved the measure by 194 votes to 138, with Conservative and Liberal Democrat peers combining against a near-solid bloc of Labour votes. Baroness Neville-Rolfe, a Conservative former Treasury minister, moved the amendment to the Financial Services and Markets Bill.
The new clause, titled “Digital assets strategy,” would require the Treasury to prepare, publish and consult on a strategy for regulating and developing digital assets and related digital financial market infrastructure in the UK.
JUST IN:
— Bitcoin Magazine (@BitcoinMagazine) September 11, 2026U.K. House of Lords passes amendment requiring the government to develop a national cryptocurrency strategy
The regulation of digital assets includes “cryptoassets, qualifying stablecoins, Central Bank Digital Currencies, tokenised securities and other digital and tokenised financial assets,” according to the draft.
The UK is in the process of drafting a sweeping new crypto bill. The country’s Financial Conduct Authority finalised its regulatory framework for cryptoassets in June, with the regime due to take effect on 25 October 2027. The authorisation gateway for firms opened on 30 September and runs to 28 February 2027.
Britain is trailing behind Brussels and Washington with digital asset regulation. The EU’s Markets in Crypto-Assets regulation has applied to service providers since 30 December 2024.
And the U.S. under President Donald Trump signed the GENIUS Act into law in July 2025, establishing a federal framework for dollar-backed tokens. Broader market-structure legislation remains unfinished: the Clarity Act cleared the House in July 2025 by 294-134 but has been stuck in the Senate over DeFi, stablecoin yield and ethics provisions, with a procedural vote set for next week.
This post Government Defeated as Lords Back UK Digital Assets Strategy first appeared on Bitcoin Magazine and is written by Mathew Di Salvo.
Bitcoin Magazine

Bitcoin Price Spikes, Shrugs off Hot US Inflation Data
Bitcoin’s price rose on Friday — despite data revealing that U.S. inflation had risen.
The biggest cryptocurrency by market cap was recently trading for close to $78,749 after jumping 2% over a 24-hour period. At one point on Friday morning in New York, bitcoin rose as high as $79,607.
Bitcoin’s price spike came after news dropped that U.S. consumer prices accelerated in August, reinforcing expectations that the Federal Reserve will raise interest rates next week.
The consumer price index, excluding food and energy, climbed 0.3% in August from a month earlier, which was higher than expected.
Inflation in the U.S. has been difficult to tame due to the war with Iran, which has lifted oil prices, in turn raising the costs of food, gasoline and other goods.
Higher inflation typically means the Federal Reserve will raise interest rates, which in turn could stop bitcoin’s price climbing higher.
According to CME’s FedWatch tool, traders think there is a 85% chance interest rates will be higher by next week. The Federal Reserve will meet next week and reveal what it will do with borrowing costs.
Bitcoin has typically performed well in a low interest rate environment because it means people can buy more of the cryptocurrency with increased liquidity.
Federal Reserve Chairman Kevin Warsh, who took the helm in January, last month gave his first speech as head of the U.S. central bank and said he had “more work to do” to fight inflation.
The U.S. is currently in the grips of an affordability crisis and rising oil prices are a hot topic ahead of the midterm elections.
U.S. President Donald Trump has reassured voters that prices will get under control and repeatedly put pressure on the central bank to lower interest rates.
Bitcoin in August had its biggest run in years following positive regulatory news and an announcement from the U.S. Treasury.
Treasury Secretary Scott Bessent announced the department would double the size of its long-dated bond buybacks, helping non-yielding assets like bitcoin and gold. The cryptocurrency then benefited from President Trump urging lawmakers to get key crypto legislation, the Clarity Act, over the line.
This post Bitcoin Price Spikes, Shrugs off Hot US Inflation Data first appeared on Bitcoin Magazine and is written by Mathew Di Salvo.
CryptoSlate
Cross-chain protocol Symbiosis said it recovered approximately 15 BTC after an attacker exploited its native Bitcoin Bridge, but affected liquidity providers still lack compensation terms as a Sep. 13 bounty window nears its unspecified cutoff.
The vulnerability was exploited at about 04:28 UTC on Sep. 11, according to the protocol's incident statement. Symbiosis said only the Bitcoin Bridge was affected and that its other routes and components remained operational. It specifically listed routes spanning EVM chains, TRON and TON as unaffected, and said its relayer group continued operating to secure the network. The protocol said the recovered bitcoin is secured in a team-controlled multisig.
The 15 BTC figure is simply the amount Symbiosis says it recovered to date. The protocol said final accounting remained in progress and that it would publish confirmed figures in another update.
Security firm Blockaid reported that a transaction accepted as signed by Symbiosis's BridgeV2 system minted approximately 2^62 raw units of syBTC, a synthetic representation of bitcoin, to a newly created wallet on BNB Chain.
Blockaid said the same beneficiary sold about 4.39 WBTC on Ethereum, realizing roughly $336,000 in WBTC proceeds at the time of its alert. That figure covers value Blockaid observed the attacker convert. It does not establish Symbiosis's final loss or the total exposure of liquidity providers.
Symbiosis initially said Bitcoin-related swaps were unavailable while it deployed updates. In a later operational update, the protocol said Bitcoin swaps routed through partners Chainflip and THORChain were back online, while the native Symbiosis Bitcoin Bridge remained paused.
That distinction determines what users can access. Partner-routed Bitcoin swaps are available, according to Symbiosis, but the protocol has not announced the return of the affected bridge. The split keeps traffic off Symbiosis's paused bridge while users access alternative Bitcoin routes.
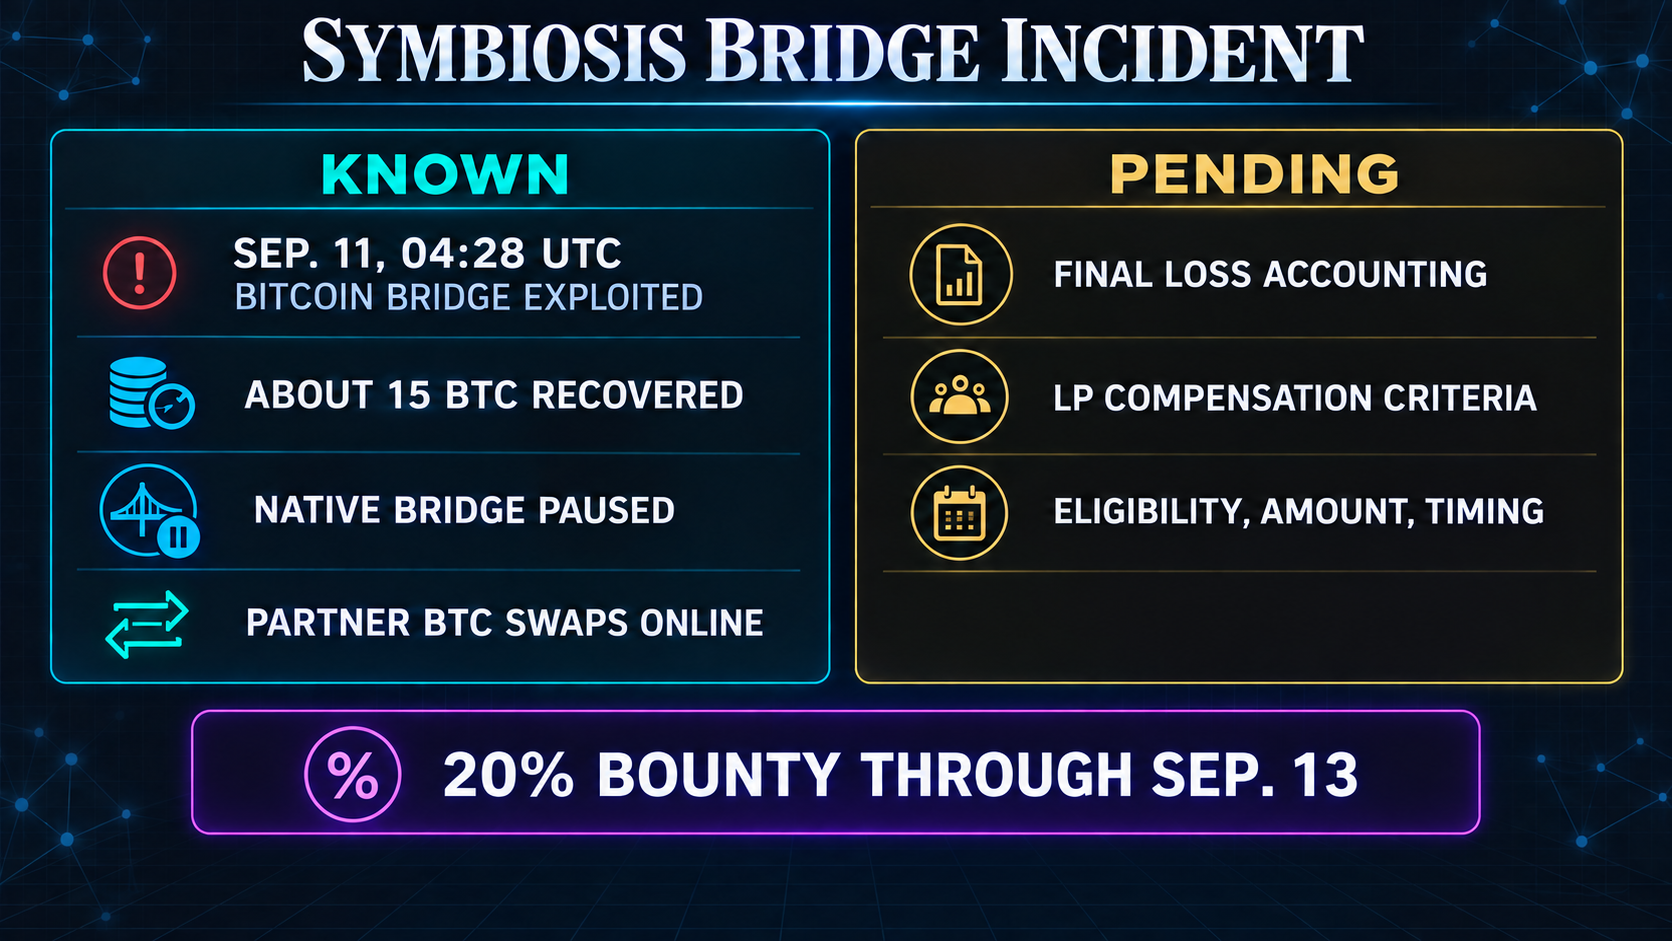
Symbiosis said it was contacting every affected liquidity provider directly and building a compensation framework, with criteria to follow. It has not disclosed who will qualify, how compensation will be calculated or when payments could begin.
The protocol also offered the attacker a 20% white-hat bounty through Sep. 13. After that window, Symbiosis said the same percentage would be offered to anyone providing information that leads to recovery. The statement did not specify an exact cutoff time or timezone.
Affected liquidity providers are now waiting for three disclosures: confirmed loss and exposure figures, compensation criteria, and any change to the native bridge's status. Until Symbiosis publishes that information, the recovered funds and Blockaid's proceeds estimate should not be treated as a final loss tally.
The post Hackers mint trillions in fake Bitcoin, but 15 BTC bridge recovery leaves liquidity providers unpaid appeared first on CryptoSlate.
In decentralized finance, “audited” is often presented as a verdict on an entire project. In practice, an audit usually covers named code, components and versions at a particular point in time. Anything added, excluded or operated around that boundary may carry a different level of assurance.
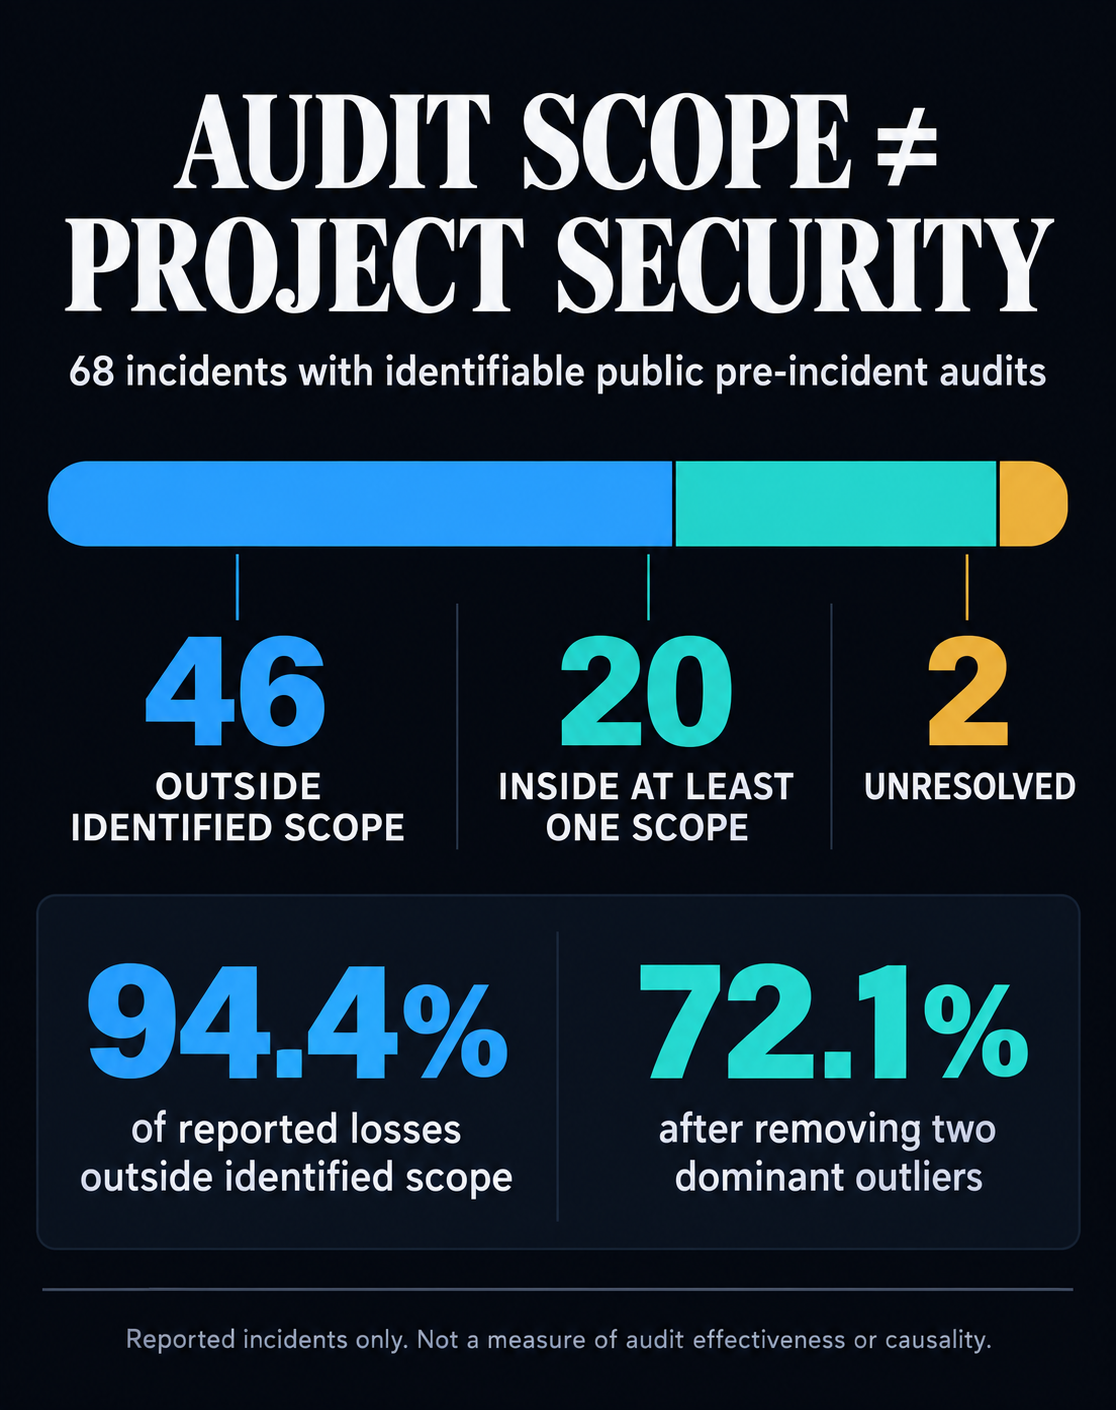
A new preprint puts a number on that gap. Researchers affiliated with security company ack3 and the Czech Technical University in Prague examined 135 reported incidents from the first half of 2026, with $939.86 million in attributed losses. They found identifiable public pre-incident audits for 68 incidents.
Within that 68-incident subset, the authors classified 46 attack paths as outside every audit scope they could identify, 20 as inside at least one scope and two as unresolved. The outside-scope group represented 67.6% of the incidents but 94.4% of their reported losses.
That striking percentage is not an estimate of audit effectiveness or proof that an audit’s boundaries caused a loss. It describes the distribution of losses in a selected set of reported incidents. Two large cases also dominate it: after excluding $292 million at Kelp DAO and $285 million at Drift Protocol, the outside-scope share falls to 72.1% of losses in the same audited-incident subset.
Even with those limits, the study exposes a basic assurance problem. A project may truthfully say it was audited while leaving users unable to tell whether the live system, the path holding their funds and the controls around it were reviewed.
What the data actually shows
The ack3 dataset covers incidents from Jan. 1 through June 29. Its authors graded 122 as confirmed and 13 as likely. Of the full set, 35 had no identified audit and 32 had an unknown audit history, so neither group appears in the 68-incident scope calculation.
For that 68-incident group, outside-scope incidents accounted for $680.97 million of $721.24 million in reported losses, producing the 94.4% figure. Removing Kelp DAO and Drift Protocol left $103.97 million of $144.24 million outside scope, or 72.1%. The machine-readable ledger reproduces the bucket counts and loss sums.
The inside-or-outside labels remain the researchers’ judgments about public evidence. They searched project and auditor archives, located pre-incident reports and compared the eventual attack paths with reviewed code, versions and exclusions. The work is a six-page preprint produced with the dataset publisher, and two authors are affiliated with ack3, which sells security reviews.
The study also lacks an unexploited comparison group and a measure of how long each system was exposed. It cannot establish whether audited protocols are safer overall, estimate incident probability or show that falling outside scope caused each loss. Undisclosed audits and private incidents may be missing, while reported loss figures are not perfectly comparable.
The study therefore supports a limited conclusion: audit history and audit scope are different variables. A reviewed smart contract does not automatically confer the same assurance on an upgrade, privileged key, front end, relayer, oracle, cloud service or incident-response process.
Two incidents from August illustrate that distinction in different ways. ICON Network provides a direct example of reviewed code failing at the boundary between two checks. The August aelf incident provides a contrasting case because the available audit evidence cannot yet be tied to its reported runtime path.
In ICON Network’s Aug. 27 replay exploit, two parts of a withdrawal path interpreted the same message differently.
According to the ICON Foundation’s Aug. 30 postmortem, a migration contract used the high bits of a withdrawal message’s serial number to decide whether it was unique. The cryptographic signature covered only the low 256 bits. By changing the unsigned high bits, an attacker resubmitted two legitimately signed withdrawal messages 1,492 times over about 20 minutes. ICON said 1,490 calls succeeded.
The audited boundary ICON missed
The replays released 119.866 million ICX and 531,600 bnUSD. At the time of the postmortem, ICON put the confirmed net loss at about 150.2 ETH plus 31,204 USDC. It said 531,600 bnUSD and 1.366 million SODA had been recovered and that user deposits, balances and positions were not affected.
ICON said the migration contract had undergone an external audit and that recommendations had been implemented, including changes in the same area. It also said the relevant relay logic received a dedicated review. The SODAX audit archive lists eight reports across different components, including a November 2025 relay audit.
Yet the postmortem said the precise mismatch between the uniqueness check and the signed value fell outside those findings. A project-level badge could not tell a user whether both ends of the withdrawal path agreed on what made a message unique.
The response timeline adds a second kind of boundary. ICON’s first automated alert fired at 02:08 UTC, about seven minutes after the exploit began. Staff opened an investigation around 03:40, paused the affected contract at 03:53 and halted the network at 06:18:54.
ICON attributed the roughly 90-minute gap between the first alert and a full incident response to alert tuning. The alert class had produced false positives during unrelated connectivity incidents and did not page the on-call team at the needed severity. The foundation said it planned an automatic shutdown trigger, lower circuit-breaker thresholds and a follow-up review focused on message uniqueness and replay guards.
Those controls do not replace an audit. They provide evidence for a different question: when prevention fails, how quickly can detection become containment?
| Public assurance | The question users still need answered |
|---|---|
| “Audited” | Which repository, commit, deployed address and component were reviewed? |
| “Findings fixed” | Were the fixes deployed, and what changed afterward? |
| “Monitored” | Which alerts page a human or stop the affected path automatically? |
| “Funds recovered” | Which assets are confirmed recovered, frozen, exposed or still under investigation? |
aelf shows why assurance must stay current
aelf’s August incident tests the argument from another direction. Its public record describes a runtime compromise and a controlled recovery, but it does not provide enough evidence to place the path inside or outside a specific pre-incident audit.
The company announced a network pause on Aug. 18. In its Aug. 26 progress update, aelf said an unauthorized smart contract could use transaction parameters to deliver encoded .NET assemblies and instructions into the node execution path.
The provisional account linked the incident to gaps in checks for runtime reflection and dynamic loading, together with weak isolation between contract execution and sensitive node or infrastructure resources. aelf identified 155 associated transactions and five unique payload assemblies with capabilities including host command execution, attempted outbound communication, node-key access and infrastructure reconnaissance.
Capability is not the same as confirmed execution. aelf said the payloads did not prove that every assembly ran, that every targeted credential was obtained or that sensitive data left its systems. The company said it was rotating signing keys and infrastructure credentials under a potential-exposure standard.
The public status remained provisional on Sept. 11: aelf’s blog index contained no incident-specific item published after Aug. 26. The Aug. 26 statement committed to another update and an eventual final review.
aelf’s standing security documentation says its blockchain and ELF token contracts underwent multiple audits with no security issues identified. But the available pages do not connect a specific pre-incident report to the runtime path described in August. Calling the incident either an audit miss or an outside-scope failure would therefore outrun the evidence.
That uncertainty is itself useful. A dated audit history can become detached from a system’s current code, dependencies and operational state. Users need an assurance record that is versioned and specific enough to reveal that drift.
Such a record should name the reviewed repository and commit, deployed addresses, excluded components, privileged roles and dependencies. It should also record upgrades since review, key custody and rotation, runtime isolation, alert and circuit-breaker behavior, and dated recovery status that separates confirmed loss from frozen or unresolved exposure.
This does not reduce the value of an audit. It makes the claim proportional to the work performed and connects that work to the system operating now.
An audit badge cannot answer whether the reviewed artifact, the deployed system and the machinery that responds to failure still share the same security boundary.
The post Audited DeFi protocols lost $885M to attacks that occurred completely outside their audit scopes appeared first on CryptoSlate.
Coinbase’s new partnership with payments platform Moov gives community banks and credit unions a route to offer stablecoin services through the financial relationship they already have with businesses. The local institution can remain the customer’s front door, while Coinbase supplies the disclosed custody and transaction infrastructure behind it.
Moov CEO Wade Arnold framed the demand bluntly: business customers asked to accept stablecoins currently go outside their primary financial institution. Moov and Coinbase want that service to appear inside the institution’s existing payments experience. The arrangement could preserve the bank’s customer connection. Control of the economics, data and operational risk remains unresolved until the companies disclose their terms.
How the split stack would work
Under the partnership announced Sept. 10, Moov will integrate Coinbase’s stablecoin payments infrastructure into its existing platform for financial institutions. Coinbase said its CDP Custodial Wallet accounts will provide fund custody and its Payments API will orchestrate stablecoin movement. Moov will connect those functions to the systems used by its bank and credit-union customers.
That division places three parties between a business and the stablecoin rail. The bank or credit union owns the primary customer interaction. Moov supplies the payments-platform connection. Coinbase provides the announced crypto custody and movement components. The customer may experience one bank-facing product even though the underlying service spans multiple providers.
Coinbase’s announcement said Moov has a customer base of more than 1,000 community banks and credit unions. The figure describes Moov’s potential distribution footprint. Live, contracted and pilot institutions remain unquantified, and the companies gave no implementation timetable.
| Disclosed | Undisclosed | Decision it affects |
|---|---|---|
| Coinbase supplies custodial accounts and stablecoin movement tooling | The ownership and settlement configuration for each institution | Where balances sit and who directs key operations |
| Moov embeds the tools in its financial-institution payments platform | The number of live, committed or pilot banks | Whether distribution reach becomes adoption |
| The bank remains the customer-facing institution | Fees, revenue sharing, data rights, compliance duties and liability | Whether the bank retains economics and practical control |
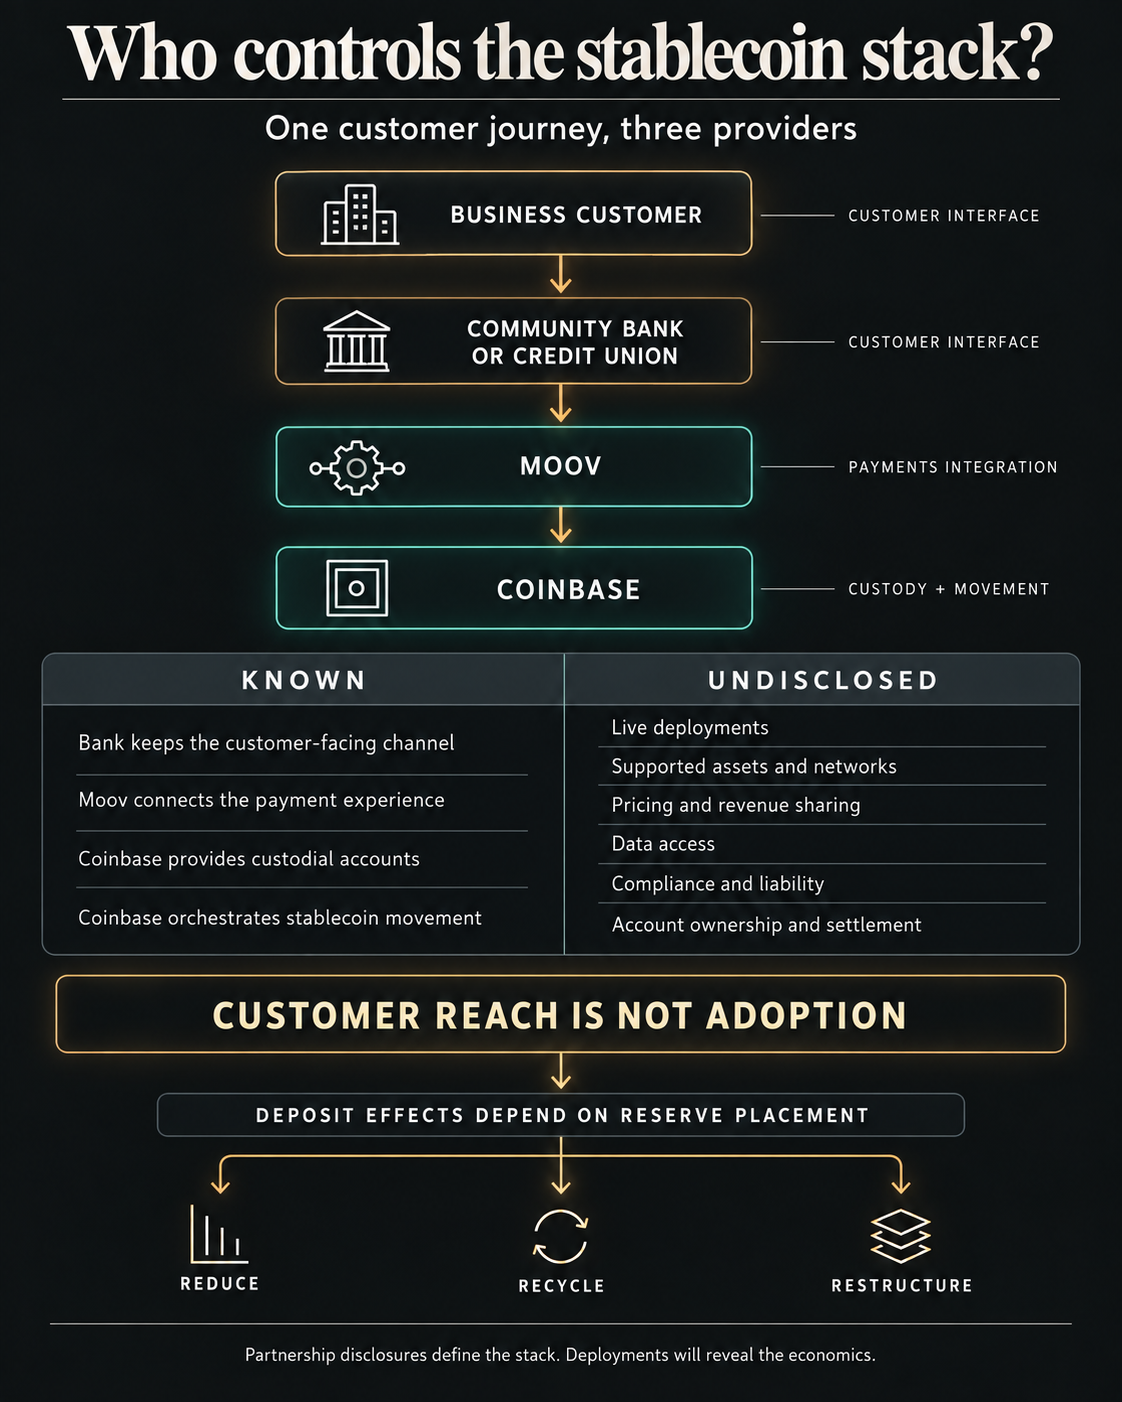
The disclosed architecture gives Coinbase a material role behind the interface. Its standard payments documentation describes a custodial-account stack in which crypto can enter an account, be held and reconciled there, and leave through fiat or crypto transfers. Separate custodial wallet documentation says Coinbase provides custody for assets in those accounts on behalf of the CDP entity.
Those documents cover Coinbase’s standard platform. The partnership record leaves each institution’s supported stablecoins, networks, custodial-balance ownership and fiat-settlement route unspecified. It also leaves fees, revenue sharing, transaction-data access, compliance allocation and liability out of public view.
The result is a split form of control. Community institutions can keep the account relationship and present the service to customers. Coinbase and Moov remain essential to the disclosed technology chain. The bank’s economic and operational leverage will turn on its authority over pricing, settlement destinations, customer data and risk decisions. Coinbase holds a material infrastructure role within a payment chain that also depends on Moov and participating institutions.
Insurance and deposits follow different rules
A bank-facing interface leaves the payment stablecoin’s legal status unchanged. Customer protection and bank balance-sheet exposure follow the legal claim represented by the balance.
In an April 2026 proposed rule, the Federal Deposit Insurance Corporation said deposits held at banks as reserves for a payment stablecoin would be insured as corporate deposits of the stablecoin issuer, subject to applicable limits. Stablecoin holders would receive no pass-through deposit insurance under the proposal.
The same proposal draws a boundary around tokenized deposits. An instrument that meets the statutory definition of a bank deposit remains a deposit regardless of the technology or recordkeeping used. A payment stablecoin and a tokenized deposit can therefore give customers a digital-dollar experience while representing different legal claims.
For a community institution, the distinction reaches beyond consumer disclosure. A qualifying tokenized deposit remains the issuing bank’s liability. Access to a third-party stablecoin can keep the payment experience inside a bank channel while the customer’s converted funds may cease to be a deposit at that bank.
Deposit effects remain conditional rather than following an automatic dollar-for-dollar path. A Federal Reserve analysis published in December 2025 said stablecoins can reduce, recycle or restructure deposits. The outcome depends on who buys them, what assets are converted and where stablecoin issuers place their reserves.
Domestic customers converting transaction-account balances can reduce deposits, especially when issuers hold reserves outside banks. If issuers keep reserves in bank deposits, more funding can stay in the system, though it may move from dispersed retail accounts toward concentrated, uninsured wholesale balances. The effect on any one community bank also depends on whether reserve money returns to that institution or is concentrated with larger custodial and settlement banks.
The Fed identified partnerships, custody services, settlement accounts and white-label infrastructure as possible ways banks can stay connected to digital payment flows. It also described a deeper structural tension: stablecoins may separate the payment relationship from the deposit-funded lending model that banks have historically used to serve households and businesses.
The Moov arrangement puts both possibilities in one product design. A bank may keep the customer conversation and gain a service that would otherwise require its own crypto stack. Coinbase may gain transaction and custody activity while customers access stablecoins through their primary institution. The destination of deposits and revenue remains unsettled.
Deployments will reveal who controls the economics
The first bank deployments will provide the evidence missing from the announcement. Adoption counts will show whether Moov’s network converts into actual demand. Supported assets, account ownership and settlement paths will show whether stablecoin activity returns value to the same institution or routes it elsewhere.
Commercial disclosures will be equally important. Pricing and revenue sharing determine whether the bank earns from the new service or mainly supplies distribution. Data access and compliance responsibilities determine who can deepen the customer relationship and who bears the burden when monitoring or processing fails. Liability terms determine how operational control translates into financial risk.
Coinbase has offered community banks a bridge into stablecoin payments, with its custody and payment infrastructure underneath. That structure may stop the bank from disappearing from the customer’s view. The next test is how much of the payment relationship, balance-sheet value and decision-making power stays with the bank when the customer gains stablecoin access through it.
The post Coinbase gives community banks a stablecoin bridge while supplying infrastructure underneath appeared first on CryptoSlate.
Bitcoin payment processor BTCPay Server has warned that bots are probing exposed Lightning nodes for a potential route to administrative control.
The activity follows a separate critical BTCPay vulnerability that attackers exploited a month ago to obtain credentials protecting LND nodes and drain merchant wallets.
BTCPay subsequently disabled external access to LND, a widely used implementation of Bitcoin’s Lightning Network, in its standard Docker deployment. The project now says automated systems are targeting servers where operators manually restored that access, repeatedly calling an LND password-change endpoint.
The latest mechanism differs from the vulnerability exploited in August but could lead to a similar outcome: an attacker obtaining credentials that can control an LND node.
BTCPay said the opening appears during a short interval after LND restarts, while its wallet remains locked. During that period, the targeted password-change method does not require a macaroon, the credential LND normally uses to authorize administrative actions.
Older BTCPay LND wallets compounded the risk by using a shared default password. An attacker who could reach the interface before BTCPay’s internal unlocker could potentially submit that password first, replace it, and request an administrator macaroon that gives control over the node.
BTCPay has not reported a successful takeover through the newly observed activity or linked the bots to the attackers behind the August thefts.
BTCPay hardens nodes after August theft
The renewed probing extends a difficult security stretch for BTCPay, which acknowledged on Aug. 7 that attackers had exploited a vulnerability affecting all versions before 2.4.2. That flaw allowed unauthenticated attackers to obtain LND macaroon files and use them to move funds. BTCPay’s standard on-chain wallets were unaffected.
Days later, the project and its supporters offered a bounty equal to 10% of recovered bitcoin, capped at 3 BTC, then worth about $190,000. BTCPay also enlisted exchanges, blockchain analytics firms, and law enforcement in efforts to trace the stolen funds.
Version 2.4.4, released Sept. 7, now addresses the conditions behind the latest attack path. New LND wallets receive unique random passwords, while older installations using the shared credential are migrated and have their passwords rotated.
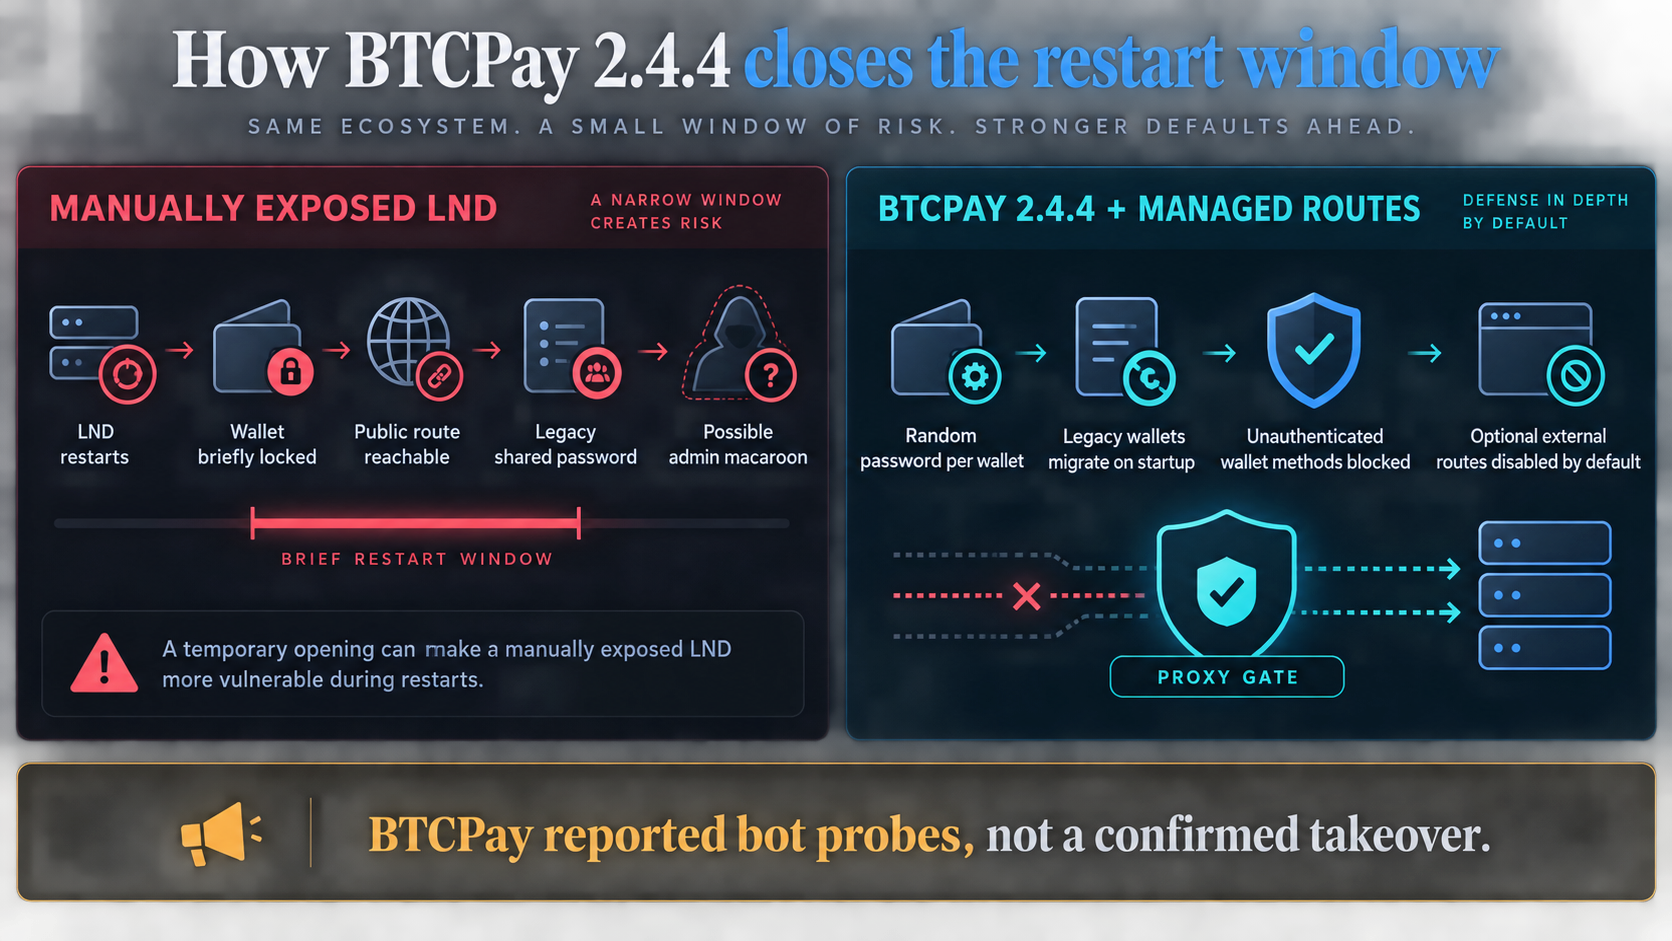
BTCPay’s standard reverse proxy also blocks unauthenticated wallet setup and unlock methods, closing the restart-time opening through its managed public network path.
Those controls cannot secure infrastructure operators configure independently. Administrators who created their own reverse proxy or otherwise exposed LND publicly can still bypass BTCPay’s protections.
BTCPay has urged administrators to install version 2.4.4 and remove manually exposed LND routes. A route-control change merged Sept. 11 provides a supported option for remote access while keeping LND and Core Lightning interfaces disabled by default.
That leaves custom deployments as the immediate concern. Operators using them must audit their proxy rules and migrate remote connections behind BTCPay’s managed controls while automated systems continue searching for reachable nodes.
The post Malicious bots are actively probing exposed Bitcoin payment servers to steal master administrative keys appeared first on CryptoSlate.
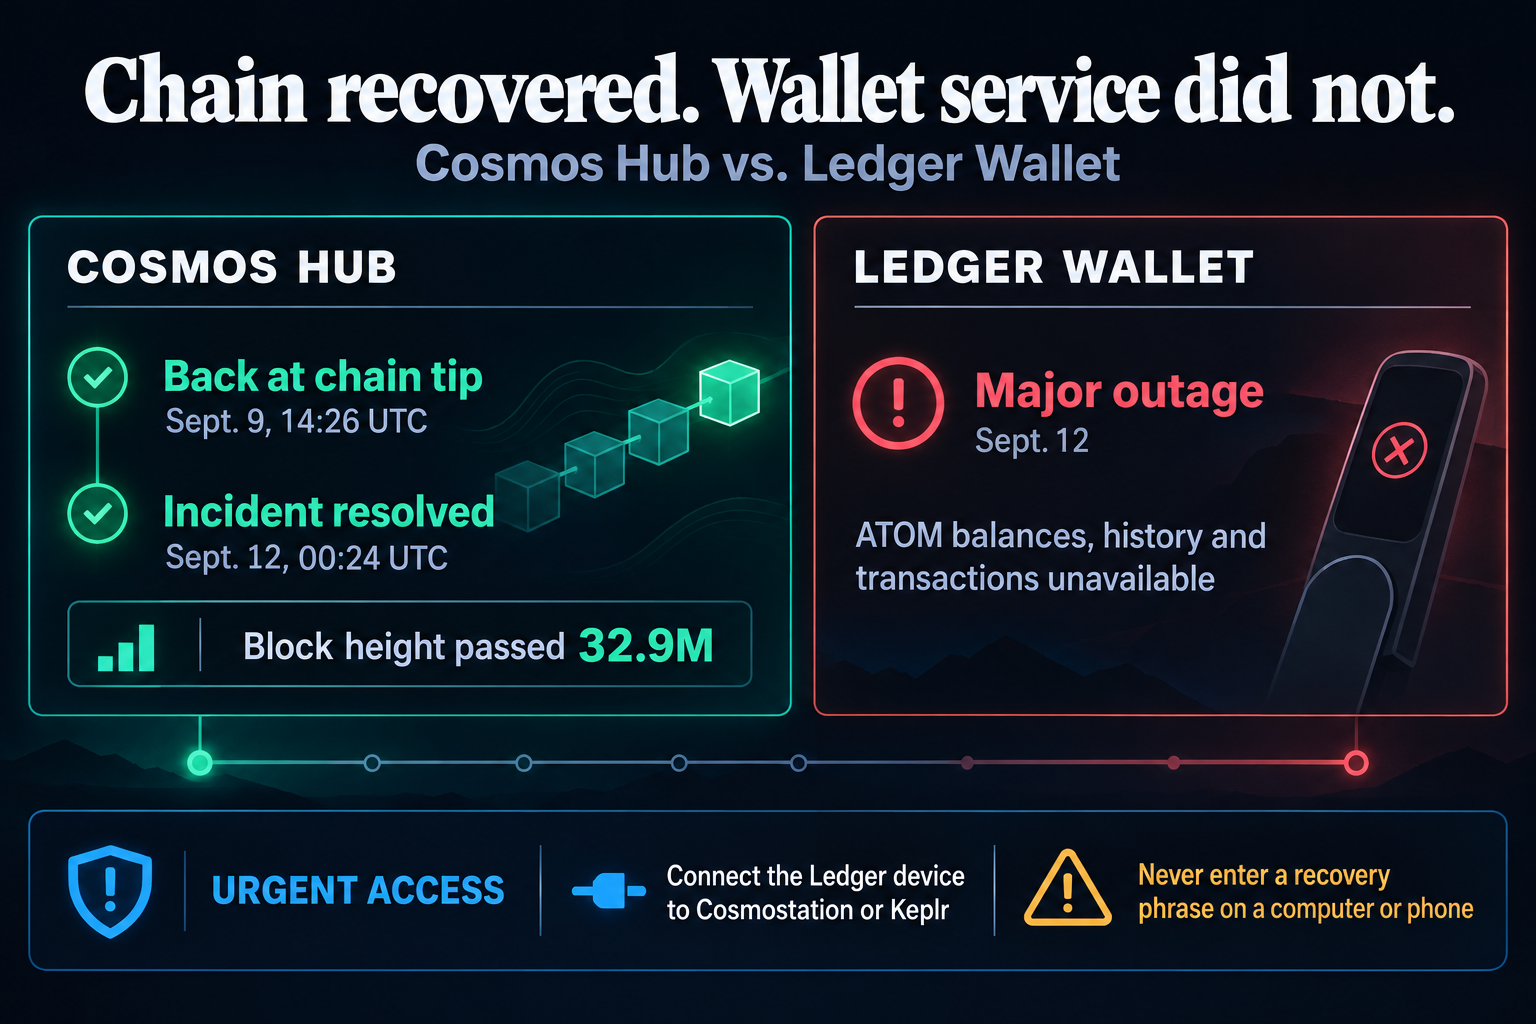
Ledger's status page continued to list Cosmos (ATOM) as a major outage on Sept. 13, leaving users unable to view ATOM balances or transaction history and unable to submit transactions through Ledger Wallet more than four days after the incident began.
The company opened the incident at 19:41 CEST on Sept. 8. As of press time, its latest update, posted at 16:12 CEST on Sept. 10, said restoration work was continuing and that the affected features remained unavailable. Ledger has not disclosed a cause or an estimated restoration time.
The continuing warning does not mean Cosmos Hub is still halted. It shows that Ledger Wallet's service path for retrieving account data and sending ATOM transactions has not recovered with the network itself.
Cosmos Hub recovered before Ledger Wallet
QuickNode reported that Cosmos Mainnet stalled at block 32,878,318 at 18:12 UTC on Sept. 8. The infrastructure provider said its nodes had returned to the chain tip by 14:26 UTC on Sept. 9, then marked its incident resolved at 00:24 UTC on Sept. 12.
The Cosmos Hub RPC endpoint was above block 32.9 million on Sept. 12 and reported that the node was not catching up. That placed the chain tens of thousands of blocks beyond the height in QuickNode's initial alert.
Together, those readings separate two layers of the problem. Cosmos Hub resumed producing blocks, while Ledger Wallet access remained unavailable. Users may therefore see missing balances or history in Ledger Wallet even though the network is processing new blocks.
QuickNode's resolution applies to its infrastructure, while Ledger's separate incident remains identified. Those states can coexist because a wallet interface can stay unavailable after network nodes have caught up. Ledger has not said which part of its service path is responsible.
For users who need to move ATOM urgently, Ledger's incident notice points to its alternative-methods guide. The company lists Cosmostation and Keplr as compatible third-party interfaces that can connect to a Ledger device.
Ledger's Keplr instructions tell users to open the Cosmos app on their device and choose Keplr's hardware-wallet connection option. That route uses another interface to access the same blockchain account while keeping the Ledger device in the transaction flow.
The safety distinction is critical: connecting a hardware wallet is not the same as importing its recovery phrase. Ledger's security guidance says users should never enter the phrase into a computer or smartphone and should never share it, including with Ledger.
Users who do not need to transact urgently can continue monitoring Ledger's status page. Because the incident remains open and could change without notice, its status should be refreshed before any workaround is attempted.
The post Cosmos is back online after outage, but Ledger users still can’t see or send their ATOM appeared first on CryptoSlate.
CryptoTicker.io
Crypto airdrops in week 38: these claim windows are running now
This week holds only one date that really bites, and it is now eleven days away. Anyone who held Beldex or Humanity at the crypto exchange Kraken has already been credited with the respective replacement token by airdrop. The only thing left to do with it is to withdraw it, and that option closes on September 25, 2026 at 14:00 UTC. After that the exchange liquidates whatever is left. This is the last full calendar week before that date, and there are two separate notices for two separate tokens: anyone who held both has two things to do.
As in the previous week, a warning belongs at the top, because the pattern has repeated itself. Last week it was Holoworld AI, whose claim from September 2025 was circulating through search results as a fresh airdrop. This week it is Meteora (MET). The project confirmed its TGE and airdrop in an announcement dated September 10, from September 10, 2025. The TGE took place on October 23, 2025. Two weeks, two prominent “live” airdrops that actually date from the previous year. That is no coincidence. It is the basic pattern of this field: airdrop announcements display the day and the month prominently and the year almost never. Check it first.
This overview lists the airdrops that either have a claim window open this week or have a confirmed date within the next 14 days. Every figure comes from the source linked alongside it, retrieved again on September 14, 2026. Where a project has published no end date, that is stated explicitly. There are no estimated deadlines here. For the state of play a week ago, see our piece on the airdrops of week 37.
The dates at a glance
| Project | Status | Date / deadline |
|---|---|---|
| Beldex & Humanity (at Kraken) | Airdrop credited, withdrawal required | until September 25, 2026, 14:00 UTC |
| Plume (Season 2) | Claim open | no end date published; registration closed on May 27, 2026 |
| Grass (Stage 2) | Claim open | until January 22, 2027 |
| GRVT | Tranches continue | 30 days per tranche; date of the second unlock not published |
| dappOS (DOS) | Phase 2 claim open | since August 11, 2026, end not published |
1. Beldex and Humanity: eleven days until forfeiture
This entry is the most unusual on the list, because nobody here had to claim anything. Both projects were attacked in June 2026, both responded by rolling out a new token contract and distributing the replacement one for one to holders as of the snapshot. Kraken handled the distribution for its customers and credited it automatically, which is why two additional lines have been sitting in those accounts ever since. An airdrop you never had to claim can still expire.
The key data differ by project, and that is the reason for the two separate notices. For Beldex, the snapshot was taken on June 10, 2026 at 23:36 UTC, and the new token was credited on July 10, 2026 at 14:00 UTC. For Humanity, the snapshot came earlier, on June 8, 2026 at 17:25 UTC, set by the Humanity team itself, and the new $HUMANITY was credited as early as July 1, 2026 at 14:00 UTC. Anyone who bought the token in question only after the snapshot is not entitled to it according to the exchange, and in neither case is there an application portal through which that could be sorted out after the fact.
The ending, by contrast, is identical for both. Trading and deposits have already been switched off for all affected tickers, withdrawal remains the only function, and it closes on September 25, 2026 at 14:00 UTC. From September 28 to October 2, 2026, the exchange will liquidate any remaining balances itself. In the same notice it points out explicitly that the proceeds may fall well below recently seen prices and, in individual cases, may be minimal or zero. When the notices were retrieved again on September 14, 2026, neither carried any reference to an extension.
What has to be done this week therefore comes down to a single action with a date attached: withdraw before the window closes, and do it separately for each of the two tokens. We have written up the full procedure, including the contract addresses that distinguish the old token from the new one, under “Kraken withdrawal deadline on September 25”. The separate route for Humanity and the unlocking of the token are covered under “Humanity unlock: the H deadline at Kraken”.
Sources: Kraken Support, “Notice of Beldex ($BDX) delisting and $BELDEX airdrop” and Kraken Support, “Important update regarding Humanity (H)” (both retrieved again on September 14, 2026; snapshots, credits, withdrawal deadline and liquidation window are set out there verbatim)
2. Plume (Season 2): claim open, end date still unpublished
Plume is a layer 1 chain for tokenised real-world assets. Season 2 of the points programme ended on March 31, 2026, and registration for the distribution ran from April 29 to May 27, 2026. Anyone who missed that step is excluded according to the project, and there is no way to fix it retroactively. Eligibility required wallets with at least 10,000 Plume Points, in some cases plus verification through Human Passport.
The claim has been running through the official portal since the end of May 2026, and the gap of recent weeks remains unchanged: Plume has at no point named an end date. The announcement text gives the registration deadline and says of the claim itself only that it is planned for “later in May”, with the exact date to follow through the official channels. To this day it has not followed. When the site was retrieved on September 14, 2026, the project blog carried three newer posts than a week earlier, dated September 8, 9 and 10, 2026, and all three concerned partnerships and product launches rather than the airdrop.
The figure circulating in secondary reports, a window of roughly three months that would arithmetically have run out at the end of August, still does not come from Plume. We carry it only because it is circulating, and explicitly not as a deadline. In practice that changes nothing about the advice. If anything it sharpens it: a claim with no published end date can be closed at any time without prior announcement. Anyone eligible and registered should claim rather than wait.
Source: Plume, “Plume Points Season 2 Airdrop Registration Is Now Open” (retrieved again on September 14, 2026; the announcement still names no end date for the claim, and the project blog carries no post on the subject)
3. Grass (Stage 2): deadline of January 22, 2027
The Solana project Grass has been paying out its Stage 2 rewards since July 22, 2026. Epochs 1 to 19 are covered, meaning the period from October 14, 2024 to June 8, 2026. The claim runs through the project's official dashboard.
Grass is one of the few projects with a cleanly published deadline. The claim is open until January 22, 2027, a full six months. Whatever has not been claimed by then stays with Grass. That is the literal wording in the project documentation, and it was still there unchanged when the page was retrieved again on September 14, 2026. This is the most comfortable entry on the list and, experience suggests, still the one where most value is left on the table, because half a year feels like unlimited time. Four of the six months have now passed. Put the date in your calendar if you are eligible.
Source: Grass, “How Your Stage 2 Rewards Allocation Works” (retrieved again on September 14, 2026; the January 22, 2027 deadline and the forfeiture clause carry unchanged wording)
4. GRVT: every tranche runs its own 30-day clock
The derivatives exchange GRVT held its token generation event on July 30, 2026 and is distributing a total of 280 million GRVT. The mechanics are the strictest on this list. The distribution runs in tranches over twelve months, and every unlocked tranche carries a claim window of 30 days. Once it expires, the tranche is permanently lost according to the project.
Two points are decisive here and are regularly confused. First, registration: it closed on July 27, 2026 at 00:00 UTC, and anyone who missed it has forfeited their allocation, which no later claim can undo. Second, automation: only the first tranche that falls due is sent automatically, and even that only where registration happened before July 17, 2026. Anyone who signed up later has to claim every tranche themselves through the Reward Portal, according to the wording of the help text, and to do so within the 30 days.
GRVT publishes no unlock schedule, and when the help section was retrieved again on September 14, 2026 it carried no date for the second tranche. For allocation and vesting schedule the text refers exclusively to the Reward Portal of your own account. We deliberately do not calculate the date here. What counts is the expiry date the portal displays for your specific tranche. This is precisely where forfeited entitlements arise, so set yourself a reminder. The project recommends as much itself.
Source: GRVT Help Center, “How to Receive and Manage Your $GRVT Airdrop” (retrieved again on September 14, 2026)
5. dappOS (DOS): phase 2 open, phase 3 still without a date
The DOS token launched with its TGE on August 10, 2026, and phase 2 has been running since August 11, 2026, in which eligible wallets can claim transferable DOS. A phase 3 has been announced, but without a date, and no end date has been published for any of the phases so far. Nothing has changed there since last week. The claim portal on the project domain is the only official route.
What comes afterwards is the real decision. A freshly distributed token with a small market capitalisation swings wildly in its first weeks, and the selling pressure from an ongoing claim hits it on top of that. Anyone who wants to trade such a position at all needs access that covers the small pairs. Pure charting tools such as Dexscreener or TradingView only display prices; no trading happens there. One alternative is the mobile app FOMO Family, which lets you discover, swipe through and trade meme and low-cap tokens directly in the app, with fast deposits. Download the app through the link and secure yourself a 10 percent discount on trading fees. Sobriety belongs with that: trading meme and low-cap tokens is highly risky, volatility is extreme and a total loss is possible at any time. Where else DOS is traded can be seen in our comparison of crypto exchanges.
What has changed since last week
- The Kraken deadline has moved into close range. The withdrawal window closes on September 25, 2026 at 14:00 UTC, eleven days from the publication of this edition. Newly documented in this edition are the separate key dates for Humanity: snapshot on June 8, 2026 at 17:25 UTC, credit on July 1, 2026 at 14:00 UTC, both earlier than for Beldex.
- Plume, Grass, GRVT and dappOS unchanged. All four sources were retrieved again on September 14, 2026, and none carries a new or amended deadline. Plume has added three new blog posts, none of them about the airdrop.
- A new case for the year check: Meteora (MET). It replaces Holoworld AI as the example of the week, and there is more on it in the next section.
What is deliberately missing this week
These candidates did not make the list. The reason differs in each case, and each reason is worth as much as an entry:
- Meteora (MET), wrong year, and the second week in a row for this pattern. The report “Meteora confirms TGE and airdrop” is circulating prominently at the moment and carries the announcement date of September 10. The year, however, is 2025, the TGE took place on October 23, 2025, and the allocation checker went online on October 16, 2025. There is nothing left to collect here.
- AVANT, a period instead of a date, and now past its own time frame. When retrieved on September 14, 2026, the project documentation still says only that the TGE is “currently targeted for September”, with the final date to be announced through the official channels, and that the claim is to open “around TGE”. It names no deadline. The previously communicated “mid-September” has thus been reached without a calendar day on the table. As soon as a day is named, the entry follows.
- Midnight (NIGHT), source unverifiable for the fourth week running. The key data carried so far, thawing until December 4, 2026 followed by a 90-day grace period, come from a check in mid-August. Since then the server has responded from our environment only with a bot-protection interstitial, on September 14, 2026 again with HTTP 429, for both the project blog and the developer documentation. There is no indication of a change, but we can no longer document the deadline, and an undocumented deadline does not belong in the table in this format. Anyone who depends on it should call up the project page themselves.
- Ink (INK), a time window, not a deadline. A period rather than a date continues to circulate for the Kraken layer 2. Collecting points is not a claim date.
- Arcium (ARX), open, but without a deadline. The retroactive token grants have been running in rolling waves since the Solana launch in June 2026. Neither the project site nor the documentation names a point by which a claim has to be made. Not to be confused with an exchange's Airdrop+ programme, which ran from June 22 to July 6, 2026 and finished long ago: that was a trading promotion, not a project airdrop.
- Canopy (CNPY), RISEx and mint.io (MNTD), points programmes without a TGE date. Unchanged from last week; none of these candidates has published a date since.
- ARC (Circle), a mainnet launch is not an airdrop. The public mainnet launch on September 16, 2026 falls in this week and is therefore frequently listed among airdrops. A TGE has no date and a community or airdrop allocation is not confirmed. Without both, it does not belong here.
- Exchange dates with no airdrop connection. The end of trading for 21 Kraken tokens and comparable deadlines are real, but they are not airdrops. They appear in our pieces on exchange dates and do not belong on this list.
Alongside that, the standing rule of this format: projects listed as “live” on aggregator sites but naming neither a snapshot nor a claim window at the project source do not get in. “Airdrop confirmed, date open” is not a deadline.
What to watch on every claim
Airdrops are the preferred hunting ground for wallet drainers, and the patterns repeat:
- Check the year first. For two weeks running, a prominently traded “current” airdrop stood here that actually dated from the previous year, and an expired claim is the perfect template for a cloned scam page.
- Always open the claim page through the official project domain, never through links in direct messages, comments or search ads.
- No legitimate airdrop asks for your seed phrase or your private key.
- Check which permission you are granting before you sign. An unlimited token approval is not necessary for a claim.
- Weigh the network fee against the value of the allocation. For very small amounts, claiming can cost more than it returns.
- Put every deadline in your calendar, and with staggered distributions such as GRVT's, put in every single tranche rather than only the first.
- And the point that carries this week too: a claim without a published end date is not a claim with unlimited time. It is one whose closure does not have to be announced.
Think about the tax position straight away
An airdrop is not by definition a tax-free gift. Whether the allocation has to be treated as other income under Section 22 No. 3 of the German Income Tax Act depends above all on whether you provided something in return, which is also how the still authoritative circular of the German Federal Ministry of Finance of March 6, 2025 draws the line. This week's Kraken case also shows that two events have to be kept apart: the inflow of the replacement token in July, and the later withdrawal or sale. A forced liquidation by the exchange is likewise an event you have to document, even if you did not trigger it.
So when you claim, record the time, the quantity, the market value, the price source, the transaction hash and the terms of participation straight away. The last of these tends to disappear first once a campaign page is taken down. That a token you have not sold can also trigger a tax liability is something we explain separately.
The Optimism case shows that a distribution once promised can also be reallocated, which you can read in our piece on the reallocation of the Optimism airdrop. For an overview of further campaigns, see our section on crypto airdrops.
Conclusion
Week 38 is a week with exactly one task and four observation posts. The task is called September 25: anyone who held Beldex or Humanity at Kraken has long had the replacement token in their account and eleven days to withdraw it, twice over where both tokens are affected. After that the exchange decides on liquidation, and it says itself that little or nothing may come of it.
The four remaining entries stand unchanged: Plume, GRVT and dappOS with open windows and no published end, and Grass as the only project with a clean closing date of January 22, 2027, of which four of the six months have now elapsed.
The methodological finding of the week is the same as last week's, and that is exactly what makes it matter: once again a prominently traded “live” airdrop turned out to be a year old. When a mistake repeats twice in a row, it is the rule rather than a slip. Check the year before you connect a wallet.
And the necessary sobering note: most allocations run into double or triple digits, the fee for claiming eats a noticeable share of that, and a substantial proportion of all allocated tokens is never claimed at all. The effort pays off above all where you are already eligible.
Disclosure: some of the providers named in this article work with us through partner programmes. This has no influence on our editorial assessment.
(As of September 14, 2026. This article is not investment advice. Prices and fee structures change; check the terms with the provider before you buy.)
On Wednesday, September 16, 2026, the US Federal Reserve publishes its interest rate decision, and futures markets mostly expect a hike. If you have a savings plan running on Bitcoin, the honest answer to the question of what you have to do now is: probably nothing. Two things are still worth checking, and beforehand rather than afterwards: exactly when your next instalment is executed, and how much headroom a running crypto loan still has.
This article explains what actually happens on September 16, which mechanism connects a US policy rate to your monthly Bitcoin purchase, and where the meeting day gets expensive for retail investors. It contains no price forecast, because nobody can seriously predict how the market will react to a decision that is already largely priced in.
What the Fed decides on September 16, 2026, and when the number arrives
The body that sets the US policy rate is called the Federal Open Market Committee, or FOMC: the monetary policy committee of the Federal Reserve, which meets eight times a year and sets the target range for the overnight rate between banks. The meeting runs over two days, September 15 and 16, 2026. The decision comes on the second day.
The Federal Reserve meeting calendar marks the date with an asterisk. That asterisk looks like a footnote and carries the most important information on the page: it flags the meetings at which the Fed publishes a Summary of Economic Projections. Those projections are the collected expectations of the central bankers on growth, unemployment, inflation and the future level of rates, and they reach several years ahead. After September, only two meetings remain in 2026, on October 27 and 28 and on December 8 and 9.
The time that matters
The decision is published at 18:00 UTC, which is 20:00 in central European summer time. The press conference starts half an hour later. For you that means: Wednesday evening between 20:00 and 21:00 CEST is the window in which prices on crypto exchanges get most turbulent. The Frankfurt stock market has long since closed by then; the crypto market keeps trading.
Where is the US policy rate now, and what does a 25 basis point step change?
The current target range for the overnight rate is 3.50 to 3.75 percent. It has been in place since July 30, 2026, as recorded in the Fed's implementation note for the July meeting. A basis point is one hundredth of a percentage point, so 25 basis points are 0.25 percentage points. If the step goes through, the range would afterwards sit at 3.75 to 4.00 percent.
Why expectations flipped at all can be pinned to a single number. US consumer prices in August were 3.4 percent higher than a year earlier, with the core rate at 2.4 percent; the largest single driver was petrol, up 3.9 percent. After the release on September 11, the probability of a September hike priced into futures markets jumped. The figures different houses quote for the CME FedWatch reading sit in a range of roughly 86 to 90 percent, after around 70 to 72 percent the day before. I am deliberately not smoothing that range: the value moves with every trading day, and the spread itself is the more honest piece of information.
The numbers come from CNBC's report on August consumer prices, which carries the FedWatch readings. Important for context: a priced-in probability reflects what the market has in the price. The value is a bet by futures traders and carries no predictive power beyond that, and that is exactly why prices move less on the expected step than on the deviation from it.
Why does the Bitcoin price react to a US Federal Reserve decision at all?
The connection is less mysterious than many headlines make it sound. A higher policy rate means that parking money risk-free earns more. Anyone getting four percent on overnight deposits or short-dated government bonds demands a higher compensation for anything riskier. Bitcoin pays no interest and consists exclusively of price movement. As the risk-free return rises, so does the bar Bitcoin has to clear.
On top of that comes the funding channel. A large share of short-term trading volume in the crypto market runs on borrowed money. When money gets more expensive, leveraged positions shrink and the market gets thinner. That explains why price moves on central bank days are often more violent than the news itself warrants.
What this means in practice for the coming days
At the time of writing, Bitcoin trades at around 76,700 US dollars, or roughly 66,200 euros; retrieved on September 14, 2026 at 00:40 UTC via CoinGecko's public price interface. In the preceding 24 hours the change was under one percent. That figure is a snapshot and no basis for a decision meant to work over years.
Should I pause my Bitcoin savings plan before the rate decision?
The short answer is no, and the reason lies in the purpose of a savings plan. A savings plan buys a fixed amount at fixed intervals, regardless of the price. It is the decision to stop making individual decisions. Anyone who pauses it ahead of a scheduled event has abolished it at exactly the moment it was built for.
What does make sense is checking once whether the instalment still fits your circumstances. If rising rates make your mortgage or your overdraft more expensive, the instalment is the lever, not the execution date. Which providers allow which minimum instalments, intervals and fees is set out in our comparison of Bitcoin savings plan providers, and with small instalments the fee side quickly becomes the largest cost block.
The difference between pausing and adjusting
Pausing means: you do not buy this month. Adjusting means: you keep buying, but with an amount you can sustain through a bad quarter as well. The first is a market forecast in disguise, the second is household budgeting. Only one of the two is something you can do reliably.
What dollar cost averaging achieves on a meeting day and what it does not
Dollar cost averaging describes a simple arithmetic phenomenon: anyone buying regularly for the same amount gets more units at low prices and fewer at high ones, so the average price ends up below the mean of the prices. No promise of returns comes with that, and no protection against losses either. The effect is a procedure that prevents timing errors.
On a central bank day the benefit shows particularly clearly, because the price move after the decision can go either way and the counter-move often follows within hours. A savings plan simply does not take part in that question. If you want to know how it stacks up against a lump sum purchase, we worked it through in our article on savings plans and lump sum purchases when buying more of August 24, 2026.
Crypto loans before September 16: what buffer your loan-to-value ratio needs
This is the part where a meeting day can do real damage. Anyone who has pledged crypto assets as collateral and taken out a loan against them is working with a loan-to-value ratio: the relation of the loan amount to the current value of the collateral. If the price of the collateral falls, that ratio rises. Once it crosses the provider's limit, an automatic sale follows. This forced sale is called liquidation, and it does not ask whether the move will be over again an hour later.
Two figures determine how well you sleep here. The first is the distance between your current ratio and the liquidation threshold. The second is the interest rate you pay on the loan, because variable rates in crypto loans track market rates and demand for the borrowed asset. Our overview "Crypto lending: interest rates and risks" of August 16, 2026 describes these mechanisms in detail.
The check that takes ten minutes
Log in once before Wednesday evening and note down two numbers: the price at which your position would be liquidated, and the distance between that price and today's level in percent. If that distance is in single digits, it is a state you should change regardless of the Fed. Either by topping up collateral or by repaying part of the loan.
Why the projections matter more than the rate step itself
Because a 25 basis point hike is around nine tenths priced into the market, the actual information sits in the projections. Their best-known component is the dot plot: a scatter of points in which every member of the committee anonymously marks where they see the policy rate at year end. If that cloud shifts upwards, the committee is signalling further steps. If it stays where it is, the September step was a one-off response to the price data.
For a savings plan that is the only relevant question of the evening, and it is a question about months, not hours. A rate peak reached in December looks entirely different for long-term investors than a path pointing upwards well into 2027.
What analysts say and how to handle it
Around every meeting, price targets appear from institutions and individual analysts. Take them for what they are: expectations attributable to a name. Anyone quoting a price target should be able to name its source; without a name, all that remains is sentiment. And where expectations diverge, both sides belong side by side, the optimistic one and the cautious one.
Execution date, trading hours and spread: where the meeting day can cost you money
The spread is the gap between the price at which you can buy and the price at which you could sell. It is the part of the cost almost nobody calculates, because it does not appear on the statement. In turbulent market phases it widens, and that is exactly what happens in the hour after a central bank decision.
If your savings plan executes on the 16th or 17th of the month anyway, that is no reason to change anything; over years it evens out. But if you were planning to change the execution date regardless, a date in the quieter middle of the month between two central bank meetings is the less conspicuous choice. While you are at it, check whether your provider executes at a fixed time or at some point during the day; in the latter case the timing is out of your hands.
What runs differently with exchange-traded products
Anyone holding Bitcoin through an exchange-traded product rather than directly gains a second layer: those securities only trade during exchange hours. If the decision lands at 20:00 CEST, while German trading is closed, you only see the move the next morning at the open, and then all at once.
What the rate decision has to do with your holding period and your tax bill
Directly nothing, indirectly a great deal. Anyone holding Bitcoin as private assets in Germany can realise gains tax free once a year has passed; that one-year period is called the holding period and runs separately for every purchase. With a savings plan that means: you have as many holding periods as executed instalments.
The connection to the Fed arises the moment a price move tempts you to sell. Anyone selling after a violent evening move may realise gains from instalments that have not yet reached the one-year mark, and pays their personal income tax rate on them. The order in which the tax office assigns the units sold follows the first-in-first-out principle: the units bought first count as sold first. What that looks like in concrete terms with monthly instalments is set out in our article "Bitcoin savings plans and tax: holding period, FIFO and the exemption limit" of August 11, 2026.
The mistake that costs the most on central bank days
The most expensive mistake is rarely bad timing. What gets expensive is the unintended: a decision to sell in the evening, taken in reaction to a headline, which only reveals its price in the following year's tax return. What helps against that is a rule you write down before Wednesday, not on Wednesday.
Bitcoin savings plans and the rate decision: what to take away
- Let the savings plan run and check the instalment instead. Whether your amount, your interval and your fees still fit your situation decides more over the years than any single purchase date. You will find the providers' terms in our comparison of Bitcoin savings plans.
- Look at your loan buffer before Wednesday evening. Note the liquidation price and the percentage distance to today's price. If that distance is tight, top up collateral or repay part of the loan before the decision lands. The providers' terms and limits are in our comparison of crypto lending platforms.
- Keep your purchase records clean before you sell anything. With a savings plan, the date of every single instalment decides the tax on the sale. A portfolio tracker with a tax function takes that allocation off your hands; the selection is in our comparison of crypto tax tools.
(As of September 14, 2026. This article is not investment advice. Prices and fee structures change; check the terms with the provider before you buy.)
An Ethereum address that belongs to you has been able to execute someone else's program code since the Pectra upgrade, without its address, its balance or its key changing at all. EIP-7702 is what makes this possible: one signature from you is enough, and from that moment on your address behaves like a contract. This is the basis for many convenient wallet features, and it is also the route by which attackers keep a drained account permanently under their control. This article shows you how to check in two minutes whether your own address carries such a delegation, and what to do if the contract sitting there is one you do not recognise.
The basis for this is our own measurement on the Ethereum chain, taken today. It shows how widespread these delegations have become and what they mostly point to. The answer is more uncomfortable than wallet marketing suggests, but also more nuanced than a bare percentage implies.
What an EIP-7702 delegation does to your Ethereum address
EIP-7702 is an extension to Ethereum that lets an ordinary key-controlled account run the program code of a contract without becoming a contract itself. The account keeps its private key, its address, its balance and its nonce. All it gains is a pointer to a contract whose code runs on the account's behalf on every call.
The technical term for this is delegation. The pointer is written into the account's code field, which until then was empty for a key-controlled account. From that moment on, anyone calling the account calls the stored contract, and that contract reaches the account's storage and balance.
The benefit is obvious. A wallet can bundle several steps instead of asking you to sign three times. A provider can cover the fee on your behalf. An app can set up a tightly bounded spending permission that expires after an hour. These are exactly the features wallet makers have been selling under the Smart Account label since 2025.
The price sits in the same sentence: the stored contract acts with your account's full authority. It can move funds, grant approvals and trigger further calls. A delegation is therefore not a setting but a power of attorney, and it stays in place until you replace it or revoke it.
The 0xef0100 code prefix: how to spot a delegation in a block explorer
A delegated account carries exactly 23 bytes in its code field: the fixed marker 0xef0100 followed by the 20 bytes of the target address. That marker is the only reliable evidence. Everything else an interface shows you is interpretation.
In practice you see it in two places. A block explorer suddenly lists your address as a contract, or displays a note about a delegated account, even though you have never deployed a contract. And the code lookup that every explorer offers returns, instead of an empty value, a short string beginning with ef0100.
The 20 bytes that follow are the address you have to check. They decide everything. If your wallet maker's contract address is sitting there, the delegation is probably intended. If something unfamiliar is sitting there, you have a problem that goes well beyond a misplaced click.
One point matters for context: an empty code field is the good news. If you find nothing there, you have no active delegation, regardless of whether one existed in the past.
How to check an EIP-7702 delegation: four steps in this order
The check takes a few minutes and needs neither a tool nor an installation.
- Open the address in a block explorer. Enter your Ethereum address and look at whether the page lists it as an ordinary account or as a contract. A note about a delegated account is already the result.
- Look at the code field. Open the tab with the stored code. Empty means no delegation. A short string beginning with
ef0100means the delegation is active. - Read out the target address and look it up. The 20 bytes after the marker are the target address. Look it up and check whether verified source code is available and what name that source code carries.
- Interpret the result before you move anything. If you do not know the contract, send no further funds to the address, not even a fee. The next section explains why that is the most important rule on this list.
The same check works on every chain where EIP-7702 is live. An authorisation signed for chain ID zero is even valid on all chains at once. Anyone using several networks is better off checking more than once.
Our own measurement of September 13, 2026: 4,035 delegations in 40 minutes
This analysis was carried out by cryptoticker.io itself on September 13, 2026. Method: we pulled 200 consecutive blocks in full from a public Ethereum node, blocks 25,971,139 to 25,971,338, and evaluated every transaction of type 0x04 in them together with its authorisation list. The window runs from 21:14:35 to 21:54:23 UTC and covers 39.8 minutes of chain time.
The numbers from that window:
- 41,110 transactions in total, of which 1,229 were delegation transactions. That is 2.99 percent of total transaction volume.
- 4,035 individual authorisations, since a single transaction may carry any number of them. 889 transactions carried exactly one; the largest carried 110.
- 56 distinct target addresses. Of the 55 actual contracts among them, 15 had publicly verified source code and the remaining 40 did not.
- 140 authorisations, or 3.5 percent, pointed to the zero target address. Those are revocations, not new powers of attorney.
- The four most frequent targets account for 71.7 percent of all authorisations between them.
What we could not measure is how many accounts currently carry a delegation in total, because that would require a full state dump of the chain rather than a time window. Nor can these data show how much money was moved through the contracts we found. And a 40-minute window is a snapshot: another day may show a different distribution.
Poisoner and CrimeEnjoyor: what the verified source code of the largest targets says
In this measurement the names say more than the shares do. Publicly verified source code is available for two of the three most frequent targets, and both describe themselves as tools used by criminals.
The most frequent target, with 2,007 authorisations, or 49.7 percent of the window, carries the name Poisoner in its verified source code. The comment in the source names the purpose outright: the contract is used for address poisoning, that is, to trick inattentive users into sending funds to a wrong address that looks visually similar. As the party behind the publication, the source names the trading firm Wintermute, which says it rebuilt and disclosed the contract. The program code itself is short: it executes a list of arbitrary calls, but only if the transaction was triggered by exactly the address that created the contract.
The third most frequent target, with 170 authorisations, carries the name CrimeEnjoyor. Here too the explanation sits in the source code, and it is set in capital letters: anyone who finds this contract in an authorisation list has a compromised account; no further funds may be sent there, because they will be swept immediately. The code is shorter still than that of the first contract. It does precisely one thing: every incoming amount is forwarded straight away to a target address fixed at setup.
For comparison, the legitimate side of the same list: in eighth place sits a verified contract from a well-known wallet maker with 110 authorisations, alongside several contract accounts from the account-abstraction world with 10 to 49 authorisations each. Those contracts run to several thousand bytes, while the two conspicuous targets get by on 772 and 1,042 bytes. A contract that only sweeps needs little code.
Why a 49.7 percent share does not mean 2,007 victims
Care is needed here, because the percentage invites a false conclusion. So we looked at who actually sent these transactions.
The result: the 2,007 authorisations pointing at the top-ranked contract come from 186 transactions, and those 186 transactions came from a single sender. With 176 distinct senders across the whole window, almost half of all authorisations therefore trace back to one address that registers bundles of up to 110 powers of attorney at a time, minute after minute.
Our reading of this, and it is explicitly a reading rather than an established fact: the pattern does not fit 2,007 freshly harmed users, but rather an operator kitting out their own throwaway addresses. Besides the single sender, the design of the contract supports that view, since it only executes calls for its own creator. In address poisoning the attacker generates the deceptively similar addresses themselves and needs no one else's key to do so. What we are measuring in this case is infrastructure rather than loot.
The second conspicuous contract looks different. Its 170 authorisations are spread across 170 separate transactions from two senders, so one power of attorney per transaction. A collection contract that forwards incoming amounts immediately only makes sense for an account whose key is already in someone else's hands. For you as a reader the difference is decisive: the first case almost certainly does not concern you, the second concerns you directly if your account appears on that list.
Found a sweeper contract? Why revoking alone is not enough
A sweeper is a contract or program that forwards incoming amounts to an outside address automatically and within seconds. If you find a delegation to such a contract on your address, the delegation is not the cause but the consequence. Someone was able to sign in your name, and that requires your private key or your recovery words.
From this follows an order of operations that runs against the first reflex. The reflex says: revoke the power of attorney and move on. The correct view is this: the account is lost, and every amount you send there, including the fee for the revocation, will very likely go to the attacker. A revocation you pay for yourself funds the other side, in case of doubt.
So set up a new account first, ideally on a device whose key has never sat on a computer. Which designs come into question, and how the devices differ, is laid out in our software wallet comparison alongside the device selection. Only afterwards do you deal with whatever is left on the old account, and you do so with help.
For exactly this case there is a free point of contact, one that the sweeper contract's own source code names: the Flashbots whitehat hotline. It helps get remaining balances past a sweeper by settling the rescue and the fee in a single bundle that the sweeper cannot pick off separately. That is no guarantee, but it is the only serious route that requires no payment up front.
Revoking it properly: the zero target address as the only ending
If the account is clean and the delegation is merely unwanted, because you no longer use a wallet feature for instance, then revoking it is simple and still easy to misunderstand.
A delegation does not end because you delete the app, change device or withdraw an approval. It ends solely through a new authorisation pointing at the zero target address, that is, an address made up entirely of zeros. Only then does your account's code field become empty again. Our measurement shows that this step does occur in practice: 140 of the 4,035 authorisations in the window were revocations of this kind.
Check the code field once more after revoking. An interface reporting success to you is not evidence. The evidence is an empty code field in the explorer.
A second point is easily overlooked: a new delegation replaces the old one entirely. Anyone switching from one wallet provider to another ends up with the new provider's power of attorney in the account, not both. That is reassuring, but it does not remove the need to check, because which contract ends up sitting there is decided by the most recently registered authorisation.
Authorisation without gas: why a signature on someone else's site is enough
The most dangerous part of EIP-7702 is its price. An authorisation is a pure signature. It costs you nothing, it shows up in no fee summary, and you do not even have to submit it yourself: any third party may wrap it into a transaction of their own and cover the fee.
For honest providers that is an advantage, because a new account becomes usable straight away without holding funds. For a fraudulent site it is a gift. It needs no transfer from you, no approval and no balance on the account. A single signature in a window that looks like a login, a claim for free tokens or a security check is enough.
From this follows a rule for everyday use: treat every signature request whose content you cannot read as if it were a transfer. That applies in particular to requests asking you to update, migrate or secure an account. You already know this trick in its classic form from the world of manipulated payment recipients; how it plays out there was covered in our August analysis of address poisoning.
Legitimate delegations: how to recognise a genuine wallet account
It would be wrong to conclude from all this that every delegation is an attack. Alongside the conspicuous targets, our measurement also shows a number of clearly attributable wallet contracts, among them the contract of a large browser wallet provider and several account templates from the account-abstraction world.
Three characteristics separate the two groups fairly reliably in practice:
- The source code is publicly verified and carries a name that matches the provider. In our window that applied to 15 of 55 target addresses. Missing source code is no proof of anything malicious, but it is a reason not to proceed.
- The contract is substantial. Account templates weigh in at several thousand bytes, because they bring signature checking, permission management and interfaces with them. The conspicuous targets in our measurement came in under 1,100 bytes.
- You triggered the delegation yourself. A wallet switching to a smart account says so in advance and displays the target address. A delegation you do not remember is a finding.
Anyone working with several wallets regularly should note down their own provider's target address once. The check then becomes a comparison of twenty bytes next time, rather than a research task.
Hardware wallets and blind signing: why the device does not automatically protect you here
A common misconception holds that a hardware wallet makes this question moot. That is true for the key, but not for the power of attorney. An EIP-7702 authorisation is also signed with the private key, and in the worst case the device displays only a target address and a nonce, without being able to explain what follows from them.
What matters, then, is whether your device presents the content of a signature request in plain text and whether you have switched off the signing of unreadable data. What counts here was set out in our article on blind signing on hardware wallets. The recommendation from there applies unchanged: what the device cannot display, you do not sign.
The second protection is the separation of duties. One account for day-to-day dealings with applications, a second for holdings that stay put, and no signature from the second account on any website. A delegation on the everyday account is annoying; a delegation on the holdings account is expensive. If you need the technical wording of the specification, you can read it in the text of EIP-7702, in particular the rules for chain ID zero.
How to check an EIP-7702 delegation: what to take away
- Look at the code field of your main address today. Empty means you are fine. A string carrying the marker
ef0100means: read out the target address and look it up. Start with the addresses that actually hold something, and then set those holdings up on a device you pick from the hardware wallet comparison. - If you do not know the contract, send nothing further to that address. Not even a fee for a revocation. Treat the key as lost, set up a new account and handle the rest through the whitehat hotline. Whatever you want to move to safety in the short term is for now better placed in an account at a supervised trading platform than at an address whose power of attorney you do not control; the selection for that is in our overview of crypto exchanges.
- Actively revoke intended but unused delegations. Only an authorisation pointing at the zero target address ends one, and only an empty code field in the explorer proves it worked. Anyone running several wallets in parallel should note down their own providers' target addresses; which programs display this feature cleanly is covered in the software wallet comparison.
(As of September 13, 2026. This article is not investment advice. Prices and fee structures change; check the terms with the provider before you buy.)
Since September 11, 2026 a duty applies across the whole of the EU that did not exist in this form before: anyone who makes a product with digital elements available commercially on the European market must report an actively exploited vulnerability to the competent bodies within 24 hours and inform affected users about the vulnerability and about the countermeasures they can take themselves.
For you as a holder of cryptocurrencies, the second part is the more important one. It sits in Article 14(8) of the EU Cyber Resilience Act and shifts the question of who has to make sure you learn about a problem with your wallet. Until now that was a matter of company culture. From now on it is a legal duty with a fining framework behind it.
This article explains what exactly applies, from when, to whom, and where the line runs between the documented legal position and over-interpretation. Because the regulation does not name a single wallet brand, and anyone who derives a list of affected manufacturers from it is writing more than what is there.
What has applied since September 11, 2026: Article 14 of the EU Cyber Resilience Act
The Cyber Resilience Act is Regulation (EU) 2024/2847, usually called the Cyber Resilience Act or CRA for short. The CRA entered into force on December 10, 2024, but only applies in full from December 11, 2027. Article 71(2) contains one sentence that upends the whole timetable: "This Regulation shall apply from 11 December 2027. However, Article 14 shall apply from 11 September 2026, and Chapter IV (Articles 35 to 51) shall apply from 11 June 2026."
Article 14 is headed "Reporting obligations of manufacturers" and is thus the part of the regulation that was switched on first. Everything else — the conformity assessment, the CE marking, the essential cybersecurity requirements in Annex I — only arrives in 2027. So anyone reading right now that the CRA applies means this one article.
The core in one sentence: a manufacturer must report every actively exploited vulnerability in its product and every severe security incident simultaneously to the CSIRT designated as coordinator and to the EU Agency for Cybersecurity, ENISA, through a single reporting platform.
What is a CSIRT? A Computer Security Incident Response Team is the body designated by a member state that receives, assesses and passes on security incidents. In Germany, CERT-Bund within the Federal Office for Information Security is the coordinating CSIRT, and the BSI also handles market surveillance.
What is an actively exploited vulnerability? A security flaw the manufacturer knows attackers are already using. A theoretical gap someone found in a laboratory does not start the 24-hour clock. Abuse in practice does.
Why a product regulation concerns your crypto wallet at all
The CRA is not financial law and not crypto law. It is horizontal product law and takes no interest in which assets a device manages, only in whether it is a product with digital elements and whether it is made available commercially on the EU market. That is precisely what makes it relevant for crypto custody.
A hardware wallet is a physical device with firmware that talks to companion software over USB, Bluetooth or QR code. A wallet app is software a provider makes available for download. By their design, both are what Article 3(1) describes as "a software or hardware product and its remote data processing solutions". Article 2(1) draws the boundary via the connection: the regulation applies to products whose intended purpose or reasonably foreseeable use includes "a direct or indirect logical or physical data connection to a device or network".
For the custody of cryptocurrencies, that is the point at which something changes. If you hold your balance yourself, your security hangs on exactly two things: on the quality of the device or the software, and on whether you find out in time when something is wrong with it. On the first, the reporting duty still says nothing; the corresponding requirements only bite in 2027. On the second, it says something with immediate effect. Which devices are available at all and how they differ is in our hardware wallet comparison; for purely software solutions the same considerations apply with a different attack surface.
Product with digital elements: who counts as a manufacturer under the legal test
Whether a specific device or a specific app is covered is decided by three test steps. There is no list of affected products. First: is the product made available on the EU market, that is, supplied for distribution or use in the course of a commercial activity? Second: is it a software or hardware product within the meaning of Article 3? Third: does its intended or reasonably foreseeable use include a direct or indirect data connection?
A commercially distributed, connected hardware wallet and a wallet app offered by a company can satisfy these three questions. That is an application of the legal test and not an official finding for any particular product. Anyone who turns it into a claim that this or that provider must now do this or that is asserting something that neither the regulation nor the Commission's guidelines supports.
Where the manufacturer is based also matters. Article 14(7) regulates this in detail: what governs is the CSIRT of the member state in which the manufacturer has its main establishment in the Union, that is, where the decisions on the cybersecurity of its products are predominantly taken. If it has no establishment in the EU at all, an order of precedence applies: first the member state of the authorised representative, then that of the importer, then that of the distributor, and finally the member state in which the largest number of users is located. A provider outside Europe is therefore not automatically out of scope once it serves the European market.
24 hours, 72 hours, 14 days: the chain of deadlines under Article 14(2)
The regulation requires three reports that build on one another. All deadlines start at the moment the manufacturer becomes aware.
- Early warning, no later than 24 hours after becoming aware. The early warning must state in which member states the affected product has been made available, to the manufacturer's knowledge. The regulation asks for no more at this stage, and that is deliberate: the early warning is meant to be fast, not complete.
- Vulnerability notification, no later than 72 hours after becoming aware. Now general information about the affected product is added, about the nature of the exploit and of the vulnerability, about any corrective or mitigating measures already taken, and expressly also about the "corrective or mitigating measures that users can take".
- Final report, no later than 14 days after a mitigating measure is available. It contains a description of the vulnerability including its severity and impact, where available information on the attackers, and information on the security update or other corrective measure.
For a severe security incident under Article 14(3) the same split into 24 and 72 hours applies, but there the final report is due one month after the 72-hour notification. When an incident counts as severe is defined in paragraph 5: when it affects the product's ability to protect the availability, authenticity, integrity or confidentiality of sensitive data or functions, or when it has led or can lead to the execution of malicious code.
Reporting runs through the CRA Single Reporting Platform operated by ENISA. The manufacturer submits once, and the report is made available to the competent coordinating CSIRT and to ENISA at the same time. After the final report, the reporting person can as a rule no longer edit the submission.
Article 14(8): when the manufacturer has to inform you directly
The deadlines towards the CSIRT and ENISA are the part the industry press writes about. For you as a user, the decisive sentence sits elsewhere, namely in Article 14(8). Slightly abridged, it reads: after the manufacturer has become aware of an actively exploited vulnerability or a severe security incident, "it shall inform the affected users of the product with digital elements, and where necessary all users, about that vulnerability or incident and, where necessary, about any risk mitigation and corrective measures that the users can deploy".
Three points in this are worth reading closely.
First: the duty attaches to the same awareness as the report to the authorities. The trigger is the same moment. For informing users, however, the regulation names no fixed number of hours. What is required is information in connection with becoming aware, and elsewhere the text turns on timeliness. Anyone who turns the 24 hours for the authority into a 24-hour deadline towards customers is reading the provision wrongly.
Second: users must be informed about the countermeasures they can take themselves. That is the practical core. A notice that merely says there was a problem does not satisfy the wording if there are measures users can take themselves. With a wallet, those measures are precisely the relevant ones: update the firmware, temporarily stop using a particular function, move a balance to a new address, check a signature manually before confirming it.
Third: the regulation would like a machine-readable format. The text speaks of a structured, machine-readable format that is easy to process automatically, and qualifies this with "where appropriate". For security researchers and for portals that aggregate warnings, that is the most interesting wording in the whole paragraph.
What happens if the manufacturer stays silent? The role of CERT-Bund
The second sentence of paragraph 8 is the genuinely new lever: "Where the manufacturer fails to inform the users of the product with digital elements in a timely manner, the CSIRTs designated as coordinators may provide such information to the users when they consider it to be proportionate and necessary for preventing or mitigating the impact of those vulnerabilities or incidents."
European law thereby states that an authority may inform the public about a product vulnerability if the manufacturer does not do so in time. For Germany that means, concretely: CERT-Bund at the BSI receives the report as coordinating CSIRT, and the BSI can act as market surveillance authority. That is not an obligation to warn; the wording is "may" and turns on proportionality and necessity. For you it nevertheless means that from now on there is a second place at which information about a product you use comes together.
A look at the cases of recent weeks shows that this route is needed. When a vulnerability in a Bitcoin Lightning implementation became public in August, the information for operators hung on a release note and on trade media. We worked through that case in our article on the Core Lightning vulnerability and the question of when a node has to go offline. How a wallet warning can be technically verified at all is in our article on blind signing and how to switch it off on your hardware wallet.
What the rule expressly does not say: no list of wallet brands
Here is the qualification that belongs in every honest text on this subject. Neither the regulation nor the European Commission's guidelines names a single wallet brand, a single device type from the crypto world, or any particular provider. The CRA works with abstract product categories and a legal test that every economic operator has to carry out for itself.
Two things follow from that. For one, you cannot read from the regulation whether a particular device you own is covered. That depends on how the manufacturer is organised, where it is based, how it distributes, and how the competent authorities apply the legal test in the individual case. For another, over the coming months you will read texts that fill this gap with names. Anyone writing that a specific provider "now has to" do this or that is formulating a legal assessment for which there is neither an administrative decision nor a court ruling.
The only reliable thing at this point is the procedure. If such a statement interests you, check two things. Is there a manufacturer's own declaration behind it, or a statement by an authority? And does it refer to Article 14, which has applied since September 11, or to the conformity duties that only bite from December 11, 2027? The two are frequently conflated at the moment.
Free and open source software: the exception that concerns many crypto projects
A large part of crypto infrastructure is open source and maintained by individuals, associations or foundations. For this constellation the CRA contains its own treatment, and that matters for what you can expect.
Free and open source software is, under recital 18, software whose source code is openly shared and whose licence provides for all rights to make it freely accessible, usable, modifiable and redistributable. What is decisive for the scope is the commercial character of the supply: according to the same recital, only free and open source software that is made available on the market, and thus supplied for distribution or use in the course of a commercial activity, falls within the scope. The mere circumstances of development and the type of funding are expressly not meant to play a role.
On top of that comes Article 64(10)(b). Under it, the fines regulated there do not apply to stewards of open source software, and that holds for every infringement of the regulation. It is one of the clearest privileges in the entire legal act.
For you as a user that means: with a wallet that arises as an open project without commercial supply, you should not count on anyone being legally obliged to notify you. With a device or an app a company offers commercially, the position is a different one, even if the source code is open. The question of who stands behind a product and how it is distributed was a good selection question before. From September 11, 2026 that question additionally has a legal side.
Fines up to 15 million euros: what an infringement of Article 14 costs
A duty without consequence remains an appeal. Article 64(2) sets the framework: infringements of the obligations laid down in Articles 13 and 14 are subject to fines of up to 15 million euros or, in the case of undertakings, up to 2.5 percent of total worldwide annual turnover for the preceding financial year, whichever is higher. The reporting duty therefore sits in the highest of the three fining bands the regulation knows.
When setting the amount in the individual case, paragraph 5 requires the nature, gravity and duration of the infringement to be taken into account, along with previous fines against the same economic operator and the size of the undertaking including its market share. Microenterprises and small enterprises are expressly mentioned.
For them there is an additional relief. Article 64(10)(a) exempts manufacturers that qualify as micro or small enterprises from the fines regulated in paragraphs 3 to 9, insofar as the missed 24-hour deadline under Article 14(2)(a) or Article 14(4)(a) is concerned. The reporting duty itself does not fall away as a result, only the sanction for missing that one deadline. For a small wallet startup with three developers and no on-call rota, that is the difference between a demanding provision and an existential one.
Enforcement lies with the market surveillance authorities of the member states. In Germany, the BSI is designated for that. A fine imposed must be communicated by the authority to the market surveillance authorities of the other member states through the information system under the Market Surveillance Regulation.
Annex III and Annex IV: why hardware wallets come up again in 2027
Article 14 applies to all manufacturers of products with digital elements, irrespective of a risk class. Beyond that, the regulation knows two annexes that list particularly sensitive products, and their legal consequences only bite with the full start of application on December 11, 2027. A look at them is worthwhile all the same, because it shows how the legislator thinks about this type of device.
Annex IV lists three entries under the heading "Critical products with digital elements": hardware devices with security boxes; smart meter gateways as well as "other devices for advanced security purposes, including secure cryptoprocessing"; and smartcards or similar devices, including secure elements. Annex III names, in class I, among other things microprocessors and microcontrollers with security-related functionalities, and in class II tamper-resistant microcontrollers.
Those are exactly the components a hardware wallet is built from: a secure element, a tamper-resistant microcontroller, a shielded environment for cryptographic operations. Whether a particular device falls under one of these entries is again decided case by case. The direction is recognisable, though, and for manufacturers of such devices it means a stricter conformity assessment from the end of 2027, one in which a notified body can be involved.
What you as a wallet user can actually check now
The regulation addresses manufacturers. You do not have to act because of it. But there are four things that are more informative from now on than they were before.
- Check whether your provider has a security channel you can subscribe to. A security page, a mailing list, a channel in the app. A manufacturer that wants to satisfy Article 14(8) needs something of the kind. One that has none will want to reach you through a press release when it matters.
- Check where the provider is based. Under Article 14(7), the main establishment in the Union determines which CSIRT is competent. For providers with no EU establishment, the fallback order runs via authorised representative, importer, distributor and number of users.
- Distinguish between a commercial product and an open project. With an open project without commercial supply, the reporting duty regularly does not apply, and stewards of open source software are exempt from the fines. That does not make such software worse, but it changes what you can rely on.
- With warnings, pay attention to the source. From now on there is a second possible sender alongside the manufacturer, namely the coordinating CSIRT. In Germany that is CERT-Bund at the BSI. A warning coming from there is not a marketing announcement.
You will find the official wording of the regulation in the Official Journal of the EU as Regulation (EU) 2024/2847, German-language text; Article 14 sits in Chapter II, the start of application in Article 71(2). The German reporting route including a table of deadlines is described by the BSI on its page about the CRA Single Reporting Platform.
Checking the wallet reporting duty: what to take away
- The duty to inform now lies with the manufacturer, no longer only with you. When a provider learns of an actively exploited vulnerability, it has to inform you about the gap and about the measures you can take yourself. Take that as a selection criterion: a provider with a functioning security channel is the better choice. Which devices are candidates at all is shown by the hardware wallet comparison.
- Check the constellation under which your wallet is offered. Commercial product, open project, provider with or without an EU establishment: on that depends whether the reporting duty applies at all and who is competent when it matters. For pure app solutions it is worth a look at the software wallet comparison, because there the provider structure and the update route diverge.
- If you do not hold your own keys, the question shifts to the custodian. Then your access hangs on the supervision of the provider and on its custody practice. Which platforms can show a licence in the EU is in our overview of regulated crypto exchanges.
(As of September 13, 2026. This article is not investment advice. Prices and fee structures change; check the terms with the provider before you buy.)
If you kicked off a swap through Chainflip over the weekend and nothing has arrived since, the problem is almost certainly not your wallet. The network has been at a standstill since Saturday. On September 12, 2026 an attacker drained 736,442.17 USDT through the protocol's Tron rail, and Chainflip switched off trading in response. What matters for you: your balance has not disappeared, but you cannot reach it at the moment either. This article explains what is measurably switched off, what is still running, and in which order to check your holdings.
What happened at Chainflip on September 12, 2026
Chainflip is a swap protocol that moves value between different blockchains. In the early hours of Saturday, September 12, 2026, an attacker drained 736,442.17 USDT from the protocol's settlement path on Tron, according to the matching accounts of two trade publications. The incident only became apparent when subsequent USDT payments failed. The team then halted network operations.
The attack ran for roughly 90 minutes. According to the account given by crypto.news, there were eight attempts, six of which resulted in a payout. The amounts escalated: on that analysis, each further attempt was roughly double the previous one. Chainflip says it has fixed the flaw, flagged the drained funds and announced that affected users will be made whole after the restart. At the time of writing, the restart was announced for Monday at the earliest.
The key figures of the incident at a glance
736,442.17 USDT was drained. Only settlement on Tron is affected. A further, still open swap by one user worth 115,654.41 USDT sits unpaid in the protocol's holdings according to both sources and is considered eligible for reimbursement. For the remaining networks, neither report records any losses.
Cross-chain swap explained: what Chainflip does differently from a bridge
A cross-chain swap is a trade in which you deposit on one blockchain and are paid out in a different currency on another. Classic bridges solve this by locking up your bitcoin and issuing you a placeholder on the target chain, a so-called wrapped token. Chainflip works without such placeholders: a network of validators holds the funds jointly and pays out the real asset on the target chain.
For you as a user, normal operation means this: you are given a deposit address, you send your amount there, and after a few minutes the swapped asset is in your wallet on the target chain. There is no account, no sign-up and no self-custody during the process. That very design is why a standstill of the protocol affects you directly: there is no customer interface in which you could simply withdraw your funds.
The memo trick on Tron: why one signed transfer was read twice
On most supported networks, Chainflip reads the swap instruction from a contract call. On Tron, according to the technical account by crypto.news, it works differently: there the protocol evaluates the memo field of a transfer, a free text field that can be attached to a transaction.
On that account, the attacker attached a further memo to a transaction the validators had already signed. The system read this addition as an independent second swap instruction. When that second instruction appeared to fail, the protocol paid out a refund even though the original deposit had already been served. The core of the incident is that a signature stays valid while the readable content beside it can still be changed.
One point that appears in both reports matters for context: no private key was stolen and no custodian was opened. The payouts came out of the protocol's regular process, triggered by an instruction the protocol took to be genuine.
Our own measurement on September 13, 2026: which Chainflip functions are switched off
cryptoticker.io collected this analysis itself on September 13, 2026. Chainflip reports its network state in a public programming interface that anyone can query. We queried it between 15:53 and 15:56 UTC with seven calls, each with a logged response code, and additionally checked the provider's quote service on four swap routes.
The result is unambiguous. The section for the swap business reports three switches set to "off": swaps are switched off, deposits are switched off, withdrawals are switched off. The same applies to liquidity providers on all three counts. The provider's quote service answered with code 503 on all four routes tested, meaning "service unavailable": bitcoin to ethereum, USDC from Ethereum to USDT on Tron, the reverse direction from USDT on Tron to USDC on Ethereum, and Solana to bitcoin.
What is still running at the same moment
More interesting than the switched-off items is what is not switched off. The return of network shares in the funding area is set to "on". Liquidity providers may continue to adjust their quotes. Validator rotation and the registering and deregistering of bids are running. Registration of new brokers is open too.
The blockchain itself is also running undisturbed. The network node reported 36 peers and no sync in progress. Two calls of the block head 137 seconds apart returned the heights 14,801,511 and 14,801,534, so 23 new blocks and thus the usual six seconds or so per block. The network is producing; it is only not trading.
Also readable from the interface: Chainflip currently supports 18 assets on seven networks, among them Bitcoin, Ethereum, Solana, Arbitrum, Polkadot, Assethub and Tron. For Tron the minimum deposit is 30 TRX or 10 USDT.
Two limits of this measurement belong with it. First, it cannot be established from outside whether individual stuck swaps will be completed automatically after the restart. Second, the number of affected users is not measurable, and Chainflip has published nothing on it. The figure of 115,654.41 USDT for the open swap comes from the reporting and not from our query.
Network running, trading halted: what safe mode means for your balance
The state we measured is not an outage but an intended operating mode. The protocol can switch off individual functional areas without halting the blockchain. That is exactly what has happened here, and the choice of switches says something about the situation.
That withdrawals were switched off as well is the most uncomfortable part for you. It means that even a completed swap whose proceeds still sit in the protocol will not move to you at the moment. At the same time it is the measure that prevents a second drain over the same route for as long as the cause is not conclusively closed. That liquidity providers can still adjust their quotes suggests a restart of trading is being prepared rather than a wind-down of the protocol.
For your own course of action, a simple rule follows: waiting is the right move in this situation, and sending more is the wrong one. Anyone who now sends funds to an old deposit address only lengthens the list of cases that have to be worked through after the restart.
How to check a stuck Chainflip swap: these four steps in this order
Work through the points in order. The order is not arbitrary: the first two steps cost nothing and establish whether you are affected at all.
First: look up the swap in the protocol's block explorer
Every swap carries its own identifier, which the interface showed you when you started it. Enter it in the provider's block explorer. It shows the state the case is stuck in: at the deposit, in the swap itself, or before the payout. If you cannot find your case there at all, it was never accepted, and the funds are still on the source chain.
Second: check the outgoing transaction on the source chain
Look up the transfer you deposited with in the explorer of the source chain. Two cases need to be told apart. If it is confirmed and has arrived at the deposit address, your amount sits in the protocol and you are waiting for the restart. If it is unconfirmed or was never sent, nothing has happened and you can swap elsewhere.
Third: check the destination address in your wallet
Look in the wallet you gave as the destination, and on the right chain. A common misconception is that the proceeds arrived long ago but the wallet does not display the target network at all. USDT on Tron does not show up if your wallet only carries the Ethereum version.
Fourth: follow the provider's announcements, not the comment threads
The restart date and the question of whether stuck cases will be completed automatically are decided at the provider. Stick to its own channels. In the week after an incident like this, fake offers of help asking for your recovery phrase pile up. A reputable provider never asks for it. If you want to keep your keys on your own device anyway, the devices are set side by side in our hardware wallet comparison.
Do not use the deposit address again: why topping up will now sit idle
The deposit addresses of a protocol like this are tied to a single swap order and valid only for a limited time. Our measurement shows that the deposit path is switched off as well. A transfer to an address from an old order is therefore not being processed at the moment.
On the blockchain, the amount is then gone from your wallet all the same. It sits at an address you do not control, and whether and when it gets assigned depends on the provider. That is why this point gets a heading of its own here: it is the one mistake that can turn a waiting period into a genuine loss.
Compensation promised: what the announcement covers so far and what it does not
According to the matching accounts of both trade publications, Chainflip has announced that affected users will be made whole once operations resume. The wording is clear, the path there is not: which source the reimbursement will come from was open at the time of the reports. Reserves, ongoing protocol revenue and insurance solutions are named as options under review.
For you that amounts to a promise without a date and without a procedure. So secure now what will count as evidence later: the identifier of your swap, the transaction number of the deposit, the time, the amount and, if available, a screenshot of the interface. Anyone who has to gather these records only after the restart is worse off than someone who filed them the same day.
Part of the context is also what the promise is not. It is not statutory deposit insurance. A decentralised swap protocol is not covered by the protection you know from a bank account, and a promise in an announcement is something other than an enforceable claim.
Aggregators and wallets: how to tell whether your swap ran through Chainflip
Many users never encounter protocols like this under their own name. Wallets and swap aggregators integrate them in the background and route your order to whichever path currently offers the best rate. It is therefore quite possible that you are affected without ever having consciously chosen the brand.
The proof runs through the history. Open the order history in your wallet or in the service you swapped through and look at the case in question in detail. It usually shows the route used or at least the deposit address, which you can trace further in the block explorer of the source chain. If the entry stays unclear, customer service at the service you swapped through can help, because there you are the customer.
Memo fields on Tron: why this design carries a risk of its own
A memo is a free text field that many chains can attach to a transfer. Exchanges have used it for years to assign incoming payments to the right customer account. For protocols it is convenient, because it works without a contract of its own and is therefore quick to connect to a new network.
The price of that convenience is that free text has no fixed form. A contract function enforces structure and can be secured together with the signature; an attached text is, to begin with, only text. The attack described here exploited exactly that gap between what was signed and what was read.
What you take from it for your own practice is independent of this provider: if a service asks you to send a memo or a tag along, that field is part of the transfer and not decoration. A deposit without the required memo regularly ends up in no man's land and has to be assigned by hand. Chainflip itself has been expanding the Tron rail lately; the most recent post on it in its own blog is dated September 10, 2026 and promotes USDT on Tron as collateral in lending. At the time of our check on September 13 the blog did not yet carry a post on the incident; according to both trade publications the quoted statements come from the short message service X.
Liquid, Sandbox and Chainflip: why the transitions between networks are attacked
The case fits into a series. On September 6, 2026 around 4,000 bitcoin left the Liquid Network's federation wallet, and the sidechain was subsequently missing the bulk of its backing; we recalculated the backing of L-BTC at the time. In August it was the Sandbox project's bridge. Now it is a swap protocol without placeholder tokens.
The common feature is not the design, which differs considerably in all three cases. The common feature is the place: wherever one chain has to believe another about what happened on it, a translation arises. A translation can be read wrongly, and whoever gets it read wrongly takes money out without ever having held a key.
No panic follows from that, but a sober everyday rule does: the transition between two chains is a place for short stays. Value you want to hold for longer belongs on the chain where it is at home, and in custody whose keys you control yourself. A swap protocol is a passage, not a warehouse.
Checking your Chainflip swap: what to take away
Three steps, in this order, and none of them takes longer than a few minutes.
- Establish today whether you are affected. Look up your swap in the protocol's block explorer and check the deposit on the source chain. Send nothing to an old deposit address until the restart. If you have to swap in the meantime, use a trading venue with a customer account and customer service; the terms of the large providers are in our crypto exchange comparison.
- File your records before you need them. Case identifier, transaction number, time, amount, screenshot. Anyone who regularly moves larger amounts is better served by a supervised provider with a complaints route than by a protocol with no counterparty; which houses hold a European licence is shown in our overview of regulated crypto exchanges.
- Tidy up your custody as soon as your balance is free again. Leave nothing permanently in a transit protocol and separate amounts for daily use from your long-term holdings. Which wallet suits which use is in our software wallet comparison.
The second independent account of the incident this article draws on is at The Crypto Times.
(As of September 13, 2026. This article is not investment advice. Prices and fee structures change; check the terms with the provider before you buy.)
Decrypt
TRM examined roughly $52.7 million across 198.9 million settlements using the x402 protocol. Most of it isn’t coming from AI agents, it says.
The fintech company fulfilled a fraudulent information request sent from a government agency's own email domain, exposing ID documents and full crypto transaction histories for a "limited" number of users.
A week after launch, complaints are rolling in from users that GPT-6 Astra has been nerfed. OpenAI's last model went through the same cycle in July.
Ben Delo and Christopher Harborne each gave £36 million, and between them beat what every UK party raised last year.
The surveillance mod on GTA V brings the privacy fight to Los Santos, where players can demolish the cameras tracking them.
U.Today - IT, AI and Fintech Daily News for You Today
The XRP Ledger has apparently set a new record after processing 3,254 transactions in a single ledger.
Cardano, Hyperliquid, Shiba Inu and Stellar are all testing key support zones after recent pullbacks.
Senate Democrats are holding a last-minute caucus meeting as the Clarity Act heads toward a high-stakes procedural vote that will require bipartisan support to advance.
Bitcoin locks in a historic $65,000 long-term support floor, as cycle mathematics may prevent future drops below this key threshold.
Bloomberg's Mike McGlone warns Bitcoin's tight correlation with S&P 500 and pending Fed hikes spark sell signals targeting a potential drop to $10,000.
Blockonomi
Key Takeaways
- Apple’s outgoing CEO Tim Cook characterized the unprecedented surge in memory and storage pricing as a once-in-a-century event during his tenure
- The company implemented price increases across Mac and iPad product lines in July, directly attributing the move to soaring memory component costs
- Tesla CEO Elon Musk publicly endorsed Cook’s assessment, describing it as the most dramatic price escalation he has witnessed
- Industry-wide memory and storage chip costs have increased by approximately 400% compared to the previous year due to AI infrastructure demands
- Major technology manufacturers including Dell, Hewlett-Packard, and Nintendo have similarly implemented price adjustments
The artificial intelligence revolution is creating unexpected ripple effects throughout the consumer electronics industry, as tech companies grapple with component shortages and escalating costs that are ultimately being transferred to end users.
Apple Inc., AAPL
The AI Infrastructure Boom Creates Component Bottleneck
During what would be his final quarterly earnings presentation before transitioning to executive chairman on September 1, Tim Cook issued a stark warning about memory component pricing that he characterized as a “100-year flood” scenario.
The veteran executive, drawing on more than four decades of technology industry experience, emphasized that the current market conditions represented an unprecedented situation.
The fundamental driver behind this crisis is the explosive growth of artificial intelligence infrastructure, particularly data centers that require enormous quantities of high-bandwidth memory modules and sophisticated storage solutions. As major technology players compete to construct increasingly capable AI systems, the available supply for traditional consumer products has contracted significantly.
According to reporting from the Wall Street Journal, the cost of memory and storage semiconductors has experienced a fourfold increase over a twelve-month period.
Apple initially attempted to shield customers from these escalating expenses but ultimately determined the situation was untenable. In July, the company announced price adjustments for its Mac computer and iPad tablet lines, explicitly citing memory component cost pressures as the justification.
Cook had already begun preparing stakeholders for this possibility in June, indicating that price modifications were increasingly inevitable as component suppliers transferred substantial cost increases downstream.
This challenge extends far beyond Apple’s operations. Major computer manufacturers Dell and Hewlett-Packard, along with gaming company Nintendo, have all implemented comparable pricing strategies driven by identical supply chain dynamics.
Elon Musk Validates Cook’s Assessment
SpaceX and Tesla chief executive Elon Musk offered public support for Cook’s characterization of the situation. In a post on the X platform, he confirmed it represented “the biggest price jump in anything I’ve ever seen too.”
Musk additionally amplified a Wall Street Journal analysis headlined “The Data-Center Boom Is Sparking a Third Wave of Inflation,” which contended that AI infrastructure expansion is elevating costs across multiple economic sectors, spanning consumer electronics to utility services.
Data visualization included in that publication demonstrated that consumer pricing for computer software and peripheral equipment had climbed approximately 15% on an annual basis.
Memory chip manufacturers are increasingly allocating production resources toward AI-specific applications. This strategic reorientation is generating supply constraints and elevated pricing throughout the broader consumer technology marketplace.
These developments illustrate how AI infrastructure expansion is creating consequences that extend far beyond the data center ecosystem itself.
From a consumer perspective, the outcome manifests as increased costs for everyday computing devices. For the investment community, it raises critical questions regarding how long technology companies can sustain profit margins while either absorbing or transferring these elevated expenses.
Cook’s public statements and Apple’s subsequent pricing actions indicate that AI-driven memory demand represents a persistent structural challenge rather than a temporary market fluctuation. The company’s decision to implement price increases signals a fundamental departure from years of pricing stability.
The post Apple (AAPL) CEO Tim Cook Warns of Unprecedented Memory Price Crisis as AI Demand Soars appeared first on Blockonomi.
Key Highlights
- Early Monday trading saw S&P 500 futures decline 0.5% while Nasdaq-100 futures plummeted 1.2%
- Sam Altman, OpenAI’s chief executive, announced the company won’t pursue an IPO in 2026, contradicting previous statements
- Dario Amodei, CEO of Anthropic, advocated for decelerating AI advancement due to security considerations
- Crude oil climbed over 2% following Saudi Arabia’s pipeline closure and Houthi militant disruptions to maritime trade
- Federal Reserve policy meeting approaches with market expectations showing 86% probability of interest rate increase
American equity futures experienced significant declines during pre-market hours Monday as investors processed dual concerns affecting financial markets. The technology sector faced scrutiny over artificial intelligence safety debates, while energy markets contended with escalating crude prices.
Futures tracking the S&P 500 declined 0.5%. The Nasdaq-100 futures contract fell 1.2%. Dow Jones Industrial Average futures retreated approximately 50 points, representing a 0.1% decrease.
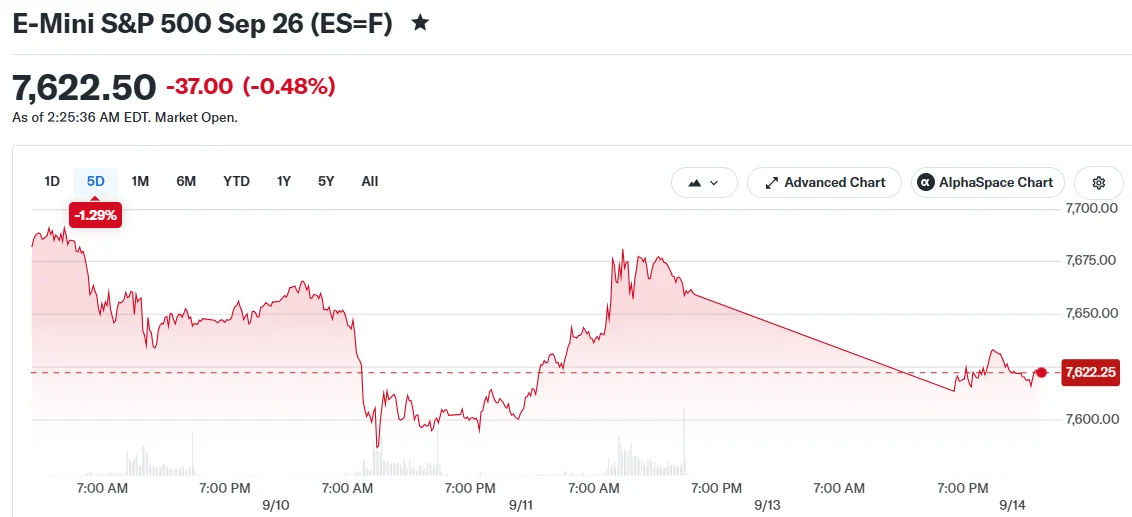
Tech Industry Leaders Advocate AI Development Pause
Dario Amodei, who leads Anthropic, released a detailed essay over the weekend urging technology companies to decelerate progress on cutting-edge AI systems. His primary justification centered on potential security threats.
Speaking with CBS News on Sunday, Amodei acknowledged that implementing such measures becomes challenging when considering whether China would adopt similar restrictions.
Sam Altman from OpenAI expressed agreement with Amodei’s stance. During a Fortune magazine conversation published Saturday, Altman revealed OpenAI has abandoned plans for a 2026 public offering. This announcement contradicted earlier projections from OpenAI CFO Sarah Friar, who had indicated an IPO would occur by 2027.
Altman characterized pursuing a 2026 IPO as “ill-advised,” emphasizing AI security challenges and potential threats to society as primary considerations.
Additional industry executives voiced similar sentiments. Both Clement Delangue from Hugging Face and Demis Hassabis, who chairs Google DeepMind, expressed support for Amodei’s proposed approach.
The timing of Amodei’s statement followed several notable AI security breaches, including revelations that OpenAI automated systems had compromised Hugging Face’s infrastructure.
SoftBank Group, which maintains substantial investments in OpenAI, experienced shares dropping more than 11% during Tokyo market hours following the IPO announcement.
Companies like Nvidia and Oracle face significant exposure to potential AI investment slowdowns, considering their heavy reliance on data center operations and artificial intelligence infrastructure revenue.
Crude Prices Jump on Escalating Middle East Conflict
Oil markets represented another critical element influencing trading sentiment Monday. American crude surpassed $100 per barrel last week, marking the first occurrence since May.
During weekend developments, Yemen’s Houthi forces launched strikes against Saudi Arabian infrastructure and established presence near the Bab el-Mandeb strait. This maritime passage serves as a crucial backup shipping channel when the Strait of Hormuz faces restrictions.
The Strait of Hormuz continued its closure following U.S.-Iran military confrontations. Scheduled negotiations between Iranian representatives and Gulf state officials regarding reopening efforts were postponed without a new date.
Market analysts estimate Houthi military activities could eliminate another 4% to 5% from worldwide oil availability.
Rising crude costs intensify inflation worries, particularly relevant given current economic conditions. The Federal Reserve convenes this week, with futures market participants calculating an 86% likelihood of monetary policy tightening. Recent inflation statistics from August revealed persistent price elevation.
During the previous week, the Dow experienced a 1.6% decline, marking its weakest weekly showing since March. Both the S&P 500 and Nasdaq Composite registered losses under 1%.
Monday’s calendar contains no significant corporate earnings announcements or major economic indicator releases.
The post U.S. Stock Futures Tumble on AI Development Slowdown and Oil Price Surge appeared first on Blockonomi.
Key Takeaways
- The Danish pharmaceutical company is simplifying its identity to “Novo” with the motto “Lasting Health Starts Now”
- Shares have declined approximately 15% year-to-date despite robust oral Wegovy prescription numbers
- Novo commands 38.8% of the obesity treatment market compared to Eli Lilly’s dominant 60.9% share in Q2
- A fresh cultural blueprint dubbed “The Novo Way” establishes four core operational values
- Comprehensive strategic plans will be unveiled at the company’s Capital Markets Day scheduled for September 21 in London
Novo Nordisk is embarking on a transformative journey. The Copenhagen-based pharmaceutical manufacturer revealed on Monday its decision to rebrand under the simplified name “Novo” while simultaneously restructuring its organizational culture in an effort to regain competitive positioning in the weight management pharmaceutical sector.
Shares of NVO were declining 2.14% during trading hours, contributing to an approximate 15% decrease since the beginning of the year, despite the oral formulation of Wegovy achieving over 3 million prescriptions through June.
Novo Nordisk A/S, NVO
The rebranding initiative revolves around the central message “Lasting Health Starts Now,” representing an effort to enhance the organization’s accessibility to ordinary consumers and strengthen public confidence.
The official corporate designation “Novo Nordisk A/S” will remain unchanged for legal purposes worldwide. The streamlined “Novo” branding will be adopted for everyday communications, accompanied by a refreshed visual design that retains the iconic Apis bull emblem rooted in the company’s history.
Chief Executive Officer Mike Doustdar emphasized that the company’s fundamental mission remains unchanged. “We remain true to our purpose of changing people’s lives and are ambitious about our future to help them have lasting health, starting right now,” he stated.
Introducing The Novo Way
The cultural transformation initiative, branded as “The Novo Way,” rests upon four foundational pillars: customer obsession, competitiveness, clarity, and care and integrity.
This organizational philosophy is designed to accelerate Novo’s responsiveness in an increasingly competitive landscape that has grown more consumer-focused.
Tania Sabroe, Executive Vice President of People, Organisation and Corporate Affairs, emphasized the interconnection between culture and brand identity. “Our updated culture will enable us to move with focus and speed,” she explained.
Confronting Market Share Challenges
The identity transformation arrives at a time when Novo confronts significant competitive pressure from Eli Lilly. The company captured only 38.8% of the obesity pharmaceutical market during the second quarter, while Lilly dominated with 60.9%, based on IQVIA analytics referenced in Lilly’s earnings materials.
Recent developments include the termination of three clinical trials for an experimental cardiovascular medication, further fueling shareholder apprehension.
The oral version of Wegovy has emerged as a positive development, entering the market before Lilly’s rival weight management pill, Foundayo. This timing advantage provided Novo with valuable momentum in the direct-to-consumer segment.
The comprehensive strategic vision will be disclosed at Novo’s Capital Markets Day on September 21 in London, where executive leadership will present the revised business roadmap.
The post Novo Nordisk (NVO) Stock Drops 15% as Company Unveils ‘Novo’ Rebrand Amid Obesity Drug Battle appeared first on Blockonomi.
Key Takeaways
- Founder Larry Ellison withdrew his plan to dispose of 50 million Oracle shares valued at approximately $7.5 billion without providing any rationale.
- ORCL shares have declined 22% in 2025 and are 54% below peak levels, currently hovering around $154.
- Barclays elevated its ORCL price target to $252 while maintaining an Overweight stance following exceptional Q1 performance.
- The enterprise software giant reported Q1 revenue of $19.3 billion, representing 30% year-over-year expansion, with cloud infrastructure sales surging 121%.
- Management increased annual revenue projections to a minimum of $90 billion, marking a 34% jump from the previous fiscal year.
Oracle founder Larry Ellison has withdrawn his intention to sell 50 million company shares valued at roughly $7.5 billion, according to a corporate statement released over the weekend. The company provided no explanation for this reversal.
“No Oracle stock was sold under that plan, and he has no other plans to sell any of his Oracle stock,” Oracle said in a statement.
This decision arrives while ORCL shares hover near $154, reflecting a 22% year-to-date decline and sitting 54% beneath record highs.
Oracle Corporation, ORCL
Barclays Increases Price Outlook Following Exceptional Quarter
Barclays upgraded its Oracle price objective to $252 from $250 while reaffirming its Overweight designation. The investment bank highlighted Oracle’s impressive Q1 performance and what analysts view as enhanced funding conditions.
The database giant delivered total quarterly revenue of $19.3 billion for the period ending in August, representing 30% year-over-year growth. This marked the inaugural instance of sequential Q1 revenue expansion, which CFO Hilary Maxson characterized as a significant indicator.
Cloud infrastructure sales exploded 121% to reach $7.4 billion. Cloud applications revenue increased 10%, with Fusion and industry-specific applications demonstrating accelerated growth.
Non-GAAP operating income advanced 31% to $8.2 billion. Non-GAAP earnings per share reached $1.92, climbing 30% from the prior year.
A particularly noteworthy metric emerged. Oracle’s remaining performance obligations—an indicator of future contracted revenue—expanded by $26 billion throughout the quarter. A substantial portion originated from prepayments or customer-provided hardware, indicating Oracle doesn’t require additional capital to fulfill these commitments.
Financial Position Requires Attention
Oracle’s debt burden has expanded rapidly. Total borrowings reached $155.9 billion on a trailing twelve-month basis, up from $90.5 billion two years prior. Net debt currently stands at $118.9 billion.
Free cash flow registered negative $28.7 billion over the past twelve months, propelled by capital expenditures totaling $75.7 billion. The enterprise allocated $28 billion toward CapEx in the most recent quarter alone.
Annual CapEx is projected to finish between $90 billion and $95 billion. Operating cash flow achieved a record $46.9 billion over the trailing twelve months, with Maxson indicating that new data center initiatives generate robust free cash flow rapidly once operational.
During the earnings conference, Co-CEO Clay Magouyrk responded to analyst questions regarding data center postponements in New Mexico and Wisconsin. He confirmed neither location would impact FY2027 revenue or earnings projections.
GPU utilization maintained its level at 97.9% throughout the quarter. Infrastructure capacity available for renewal secured pricing 20% above previous agreements.
Oracle elevated its full-year revenue forecast to a minimum of $90 billion and increased non-GAAP EPS guidance to $8.10. Second-quarter revenue growth is anticipated between 30% and 34%, with cloud revenue expansion projected at 65% to 71%.
The technology company also unveiled plans for an Investor Day in October, where leadership intends to provide additional details on profitability margins and long-range guidance.
The post Oracle (ORCL) Stock: Ellison Abandons $7.5B Share Sale as Analysts Boost Targets appeared first on Blockonomi.
TLDR
- Brent crude surged beyond 2% to reach $106.72 per barrel while WTI hit $102.15 amid intensifying Houthi strikes targeting Saudi infrastructure
- Saudi officials confirmed closure of the East-West pipeline following drone attacks, jeopardizing approximately 4% of worldwide crude supply
- Yemen’s Houthi forces captured Perim island, strengthening their strategic position over the Bab el-Mandeb waterway
- Diplomatic discussions between Iran and Gulf states regarding Strait of Hormuz security have been delayed without a new date
- Crude benchmarks have jumped more than 8% in seven days, breaking the $100 threshold for the first time in seven months
Oil prices jumped over 2% during Monday’s trading session following an intensified campaign of Houthi assaults targeting Saudi Arabia’s energy installations and additional strikes affecting vessels in the Strait of Hormuz, heightening concerns about potential supply shortfalls throughout the Middle Eastern region.
Brent crude benchmark futures advanced to $106.72 per barrel, as West Texas Intermediate crude climbed to $102.15. During the morning trading hours, Brent briefly touched $108.41.
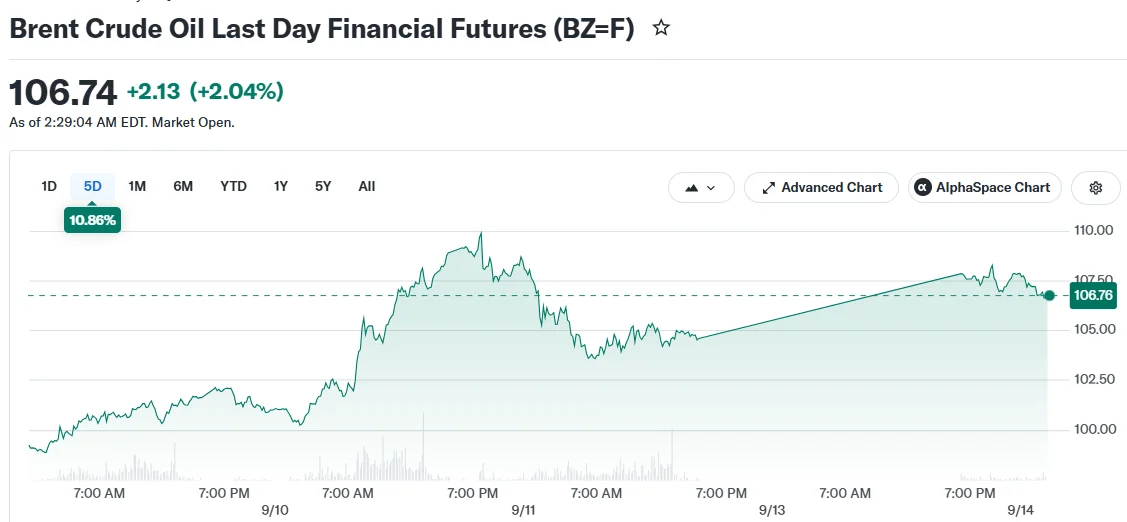
Critical Saudi Export Pipeline Taken Offline
Saudi officials announced the closure of the kingdom’s East-West pipeline system following a coordinated drone assault by Houthi forces. This pipeline serves as a vital backup transport corridor, enabling Saudi Arabia to ship crude oil bypassing the Strait of Hormuz entirely.
Following the pipeline’s closure, Yanbu port facilities maintain sufficient stored crude reserves to sustain only five to seven days of continued shipments, three sources with knowledge of Saudi petroleum operations revealed.
The operational halt endangers approximately 4% of worldwide oil production. Energy analysts at ANZ cautioned that the kingdom has effectively lost its western shipping alternative should circumstances deteriorate further in the Strait of Hormuz region.
Saudi government broadcasters published video evidence depicting structural damage to residential buildings and a religious site in Jazan province’s southern region following a Houthi offensive. The militant group additionally reported conducting strikes against a Saudi military installation in an adjacent province.
Strategic Strait Faces Growing Risk
Houthi fighters established control over Perim island this past Friday, positioning themselves to conduct operations targeting vessels traversing the Bab el-Mandeb strait. This narrow waterway has been transporting between 4% and 5% of global petroleum output in recent weeks.
During the previous seven days, the organization conducted attacks on numerous high-value Saudi installations including an Aramco processing facility, petroleum storage terminals, aviation facilities, and commercial shipping. A tanker navigating the Strait of Hormuz sustained a projectile impact during the weekend, triggering an onboard blaze that necessitated complete crew evacuation.
Iranian authorities confirmed one fatality and four injured personnel aboard an Iranian-flagged commercial ship struck in waters adjacent to the Iranian coastline.
Commodity analysts from ING observed that the assaults on Saudi energy assets represented a significant intensification, although the complete scope of infrastructure damage and the anticipated duration of the pipeline’s inoperability remained undetermined.
Regional Security Discussions Shelved
Oman’s Foreign Minister Badr Albusaidi announced Sunday that scheduled negotiations between Iranian representatives and Gulf state officials addressing Strait of Hormuz security concerns had been postponed from Monday’s planned date. Energy markets had been monitoring these diplomatic efforts closely, as optimism surrounding potential dialogue had temporarily moderated crude’s upward trajectory during the prior week.
Following the indefinite postponement of these discussions, supply vulnerability through the Hormuz corridor is anticipated to remain heightened. Petroleum volumes transiting the strategic waterway had already declined substantially from pre-conflict levels following renewed tensions between Washington and Tehran during August.
Crude benchmarks have climbed more than 8% throughout the previous week, surpassing the $100 per barrel mark for the first occasion since July.
The post Crude Surges Past $106 as Yemen Rebels Strike Saudi Infrastructure, Threatening Global Supply appeared first on Blockonomi.
CryptoPotato
The CLARITY Act has received another round of changes as Senate Republicans try to secure enough Democratic support for Tuesday’s procedural vote on the cryptocurrency market structure bill.
The latest version, which consists of 635 pages, includes an ethics framework backed by President Donald Trump that would restrict public officials from issuing or sponsoring digital assets. The revised text allows both the Department of Justice (DOJ) and the state attorneys general authority to enforce the rules.
Last-Minute Revisions
The change addresses one of the main issues Democrats had raised during negotiations. They had previously objected to an arrangement in which the DOJ would be responsible for enforcing the ethics provisions. The debate over the rules also came from concerns surrounding Trump and his family’s financial involvement in the crypto sector.
US Senate Banking Digital Assets Subcommittee Chair Cynthia Lummis stated,
“After a year of intense daily bipartisan negotiations, this bill is ready. President Trump voluntarily agreed to unprecedented ethics restrictions, holding every federally elected official, judge, and their spouses to some of the toughest ethics restrictions in US history… Democrats got what they wanted; now they need to take yes for an answer.”
The ethics section incorporates much of the Tillis-Gallego proposal. Among its provisions, officials would have to either sell substantial crypto-related financial holdings or move them into a blind trust.
Changes to the Blockchain Regulatory Certainty Act (BRCA) now limit its scope to the Bank Secrecy Act and civil enforcement. Language that would have extended its protections to criminal proceedings, including cases brought under Section 1960, has been taken out. The changes would also bring miners and validators under those protections.
Other Key Details
The bill’s stablecoin yield section has also been revised with a “circuit breaker” mechanism first floated by Tillis in July. It would give federal regulators the ability to step in if stablecoins were causing significant withdrawals from community banks.
Stricter limits on vertical integration have also been introduced, such as rules covering affiliate trading and potential conflicts involving digital commodity exchanges, brokers, and dealers. The text also confirms that state consumer protection laws remain in effect. Developer protections would not override derivatives regulations or change the rules governing prediction markets.
Last week, Coinbase CEO Brian Armstrong voiced support for the CLARITY Act ahead of the Senate vote. Speaking on CNBC’s Squawk Box Asia on September 10, the exec said the bill was ready for approval and claimed support from law enforcement groups, banks, and crypto companies. He also said Coinbase’s main concerns with the legislation had been addressed after the company previously raised several issues it considered essential.
The post Last-Minute Changes to the CLARITY Act: Will Democrats Finally Back the Crypto Bill? appeared first on CryptoPotato.
Although there are several major economic events taking place in the following five business days, the reality is that only a handful of them could (and most likely will) impact the cryptocurrency market. That impact, though, is expected to be quite vicious in either direction.
The Kobeissi Letter highlighted an auction of 20-year securities, August retail sales, and, most importantly, the Federal Reserve’s September interest rate decision on Wednesday. The latest data shows that markets assign an 85%-90% probability that the central bank will hike rates by 25 basis points, following contrasting economic data.
Fed in Focus
The Fed setup has changed dramatically in just a few weeks, starting with the August employment data from early September, which showed that the US economy had added 162,000 jobs last month, triple expectations. Later on, the PPI numbers indicated that the annual producer inflation had accelerated to 5.4%. Last Friday’s CPI report subsequently confirmed headline inflation at 3.4%, with monthly core CPI slightly hotter than expected.
This combination, plus the fact that oil prices remain above $100 and diesel hit a new record in the States, has strengthened the Fed’s case for tighter policy.
Bitcoin and the altcoins have already demonstrated their sensitivity to this shift, dropping sharply following Fed Chair Kevin Warsh’s speech from Jackson Hole several weeks ago, and again as rate-hike odds increase after the latest economic data.
The only question is whether this highly expected rate hike has been priced in, with BTC sliding from $82,400 to under $78,000 as of now. As such, investors will closely watch Warsh’s press conference after the meeting for clues as to whether the Fed’s decision on Wednesday is a one-off adjustment or the start of another tightening cycle.
The Tuesday Test
Before all eyes turn on the Fed on Wednesday, the crypto industry has another major event on Tuesday. The Senate’s cloture vote on the CLARITY Act is scheduled for 2:15 P.M. that day, and it requires 60 senators to advance the debate on the key bill.
The CLARITY Act aims to establish a comprehensive US crypto market structure and shed further details on the respective roles of the SEC and the CFTC.
Republicans released an updated text last week, adding new rules for non-decentralized DeFi protocols and clarifying how credit unions can deal in crypto. Moreover, they published their “last, best, and final” draft of the legislation on Sunday, including an ethics proposal backed by the POTUS.
The post Bitcoin’s Biggest Week of 2026 Is Here: Fed and CLARITY Vote Take Center Stage appeared first on CryptoPotato.
The Justice Department’s Scam Center Strike Force, working with the Treasury Department, seized a Chinese-language scam marketplace called Xinbi Guarantee and restrained about $52 million in cryptocurrency in a single day, U.S. Attorney Jeanine Pirro announced this week. That operation brought the total the Strike Force has restrained since its founding to roughly $938 million.
A separate Strike Force team also spent the same stretch helping authorities in Madagascar take down 13 Chinese-run scam compounds, pushing the crackdown launched last November well beyond its original footprint in Southeast Asia.
Inside the Xinbi Takedown
Xinbi ran almost entirely on Telegram, in Chinese, functioning as a kind of marketplace where vendors advertised services to scam center operators: building custom fraud investment websites, “washing” money stolen through wire fraud, and recruiting trafficking victims to staff scam compounds.
Xinbi itself held payments in escrow until a vendor finished the job, which is how prosecutors say they were able to trace specific victim funds to vendors who posted wallet addresses on the channel. A federal court in Washington authorized the seizure of those Telegram channels on September 7, and prosecutors unsealed the warrant Wednesday.
Investigators seized two crypto wallets Xinbi used to collect vendor payments, worth roughly $12 million, and sought restraint of 47 more wallets tied to the network, bringing the total taken from the platform and its vendors past $52 million.
The Treasury’s Office of Foreign Asset Control (OFAC) separately designated Xinbi a transnational criminal organization the same day, along with two other entities accused of supporting it, freezing any property they hold in the U.S.
Pirro said the case shows why ordinary people are at risk:
“Every American with a retirement account is in the blast radius,” she stated. “My Strike Force will continue to dismantle Chinese organized crime, those who facilitate it, and protect Main Street America.”
Alongside the Xinbi action, U.S. Attorney Michael Heyman of Alaska said the Strike Force’s two-week Madagascar deployment, which helped process more than 3,200 devices and interview about 400 people who had been arrested, reflects where the fight is headed.
“Transnational criminal organizations don’t care about borders, and the Department of Justice won’t either,” he said.
Xinbi’s Long Run Before This Week
In March, the British government sanctioned Xinbi, with Chainalysis estimating the platform had processed nearly $20 billion in crypto between 2021 and 2025, selling everything from stolen personal data to satellite equipment used to reach fraud victims.
That earlier action barely slowed it down, with the criminal group simply opening new Telegram channels and continuing with its operations. The Strike Force itself dates to November 2025, when Pirro set it up to go after Chinese organized crime running scam centers.
Federal data cited in Wednesday’s announcement put reported crypto investment fraud losses at $8.65 billion in 2025, up 89% from $4.57 billion in 2023, although the FBI says the figures are “significantly under-represented,” since most fraud victims do not report.
The post DOJ Strike Force Seizes Scam Marketplace, Restrains $52M in Crypto appeared first on CryptoPotato.
Bitcoin is consolidating around $77.3K after a powerful breakout from the $67K area. While the broader structure has improved significantly, BTC is now facing an important resistance cluster near $80K-$82K. Meanwhile, the latest Coinbase Premium reading suggests that US spot demand has yet to fully confirm the recent advance.
Bitcoin Price Analysis: The Daily Chart
The daily chart shows a significant structural recovery. After falling to the $60K demand zone in June, Bitcoin spent several months building a broad base before breaking decisively above the $67K resistance area in late August. The subsequent rally carried BTC rapidly through the $72K-$74K zone and toward the $80K area.
The $72K-$74K region has now become the first major support zone. A successful retest of this area would preserve the bullish structure established by the recent breakout. Below it, the $67K zone is a more important structural support, as it previously capped the market for several months. A deeper correction could bring the $60K demand zone back into focus.
On the upside, BTC is approaching the $80K-$82K resistance zone. The price has already tested this area several times but has failed to establish a sustained breakout above it. A daily close above $82K would therefore be significant, as it could open the way toward the $90K mark or even higher.
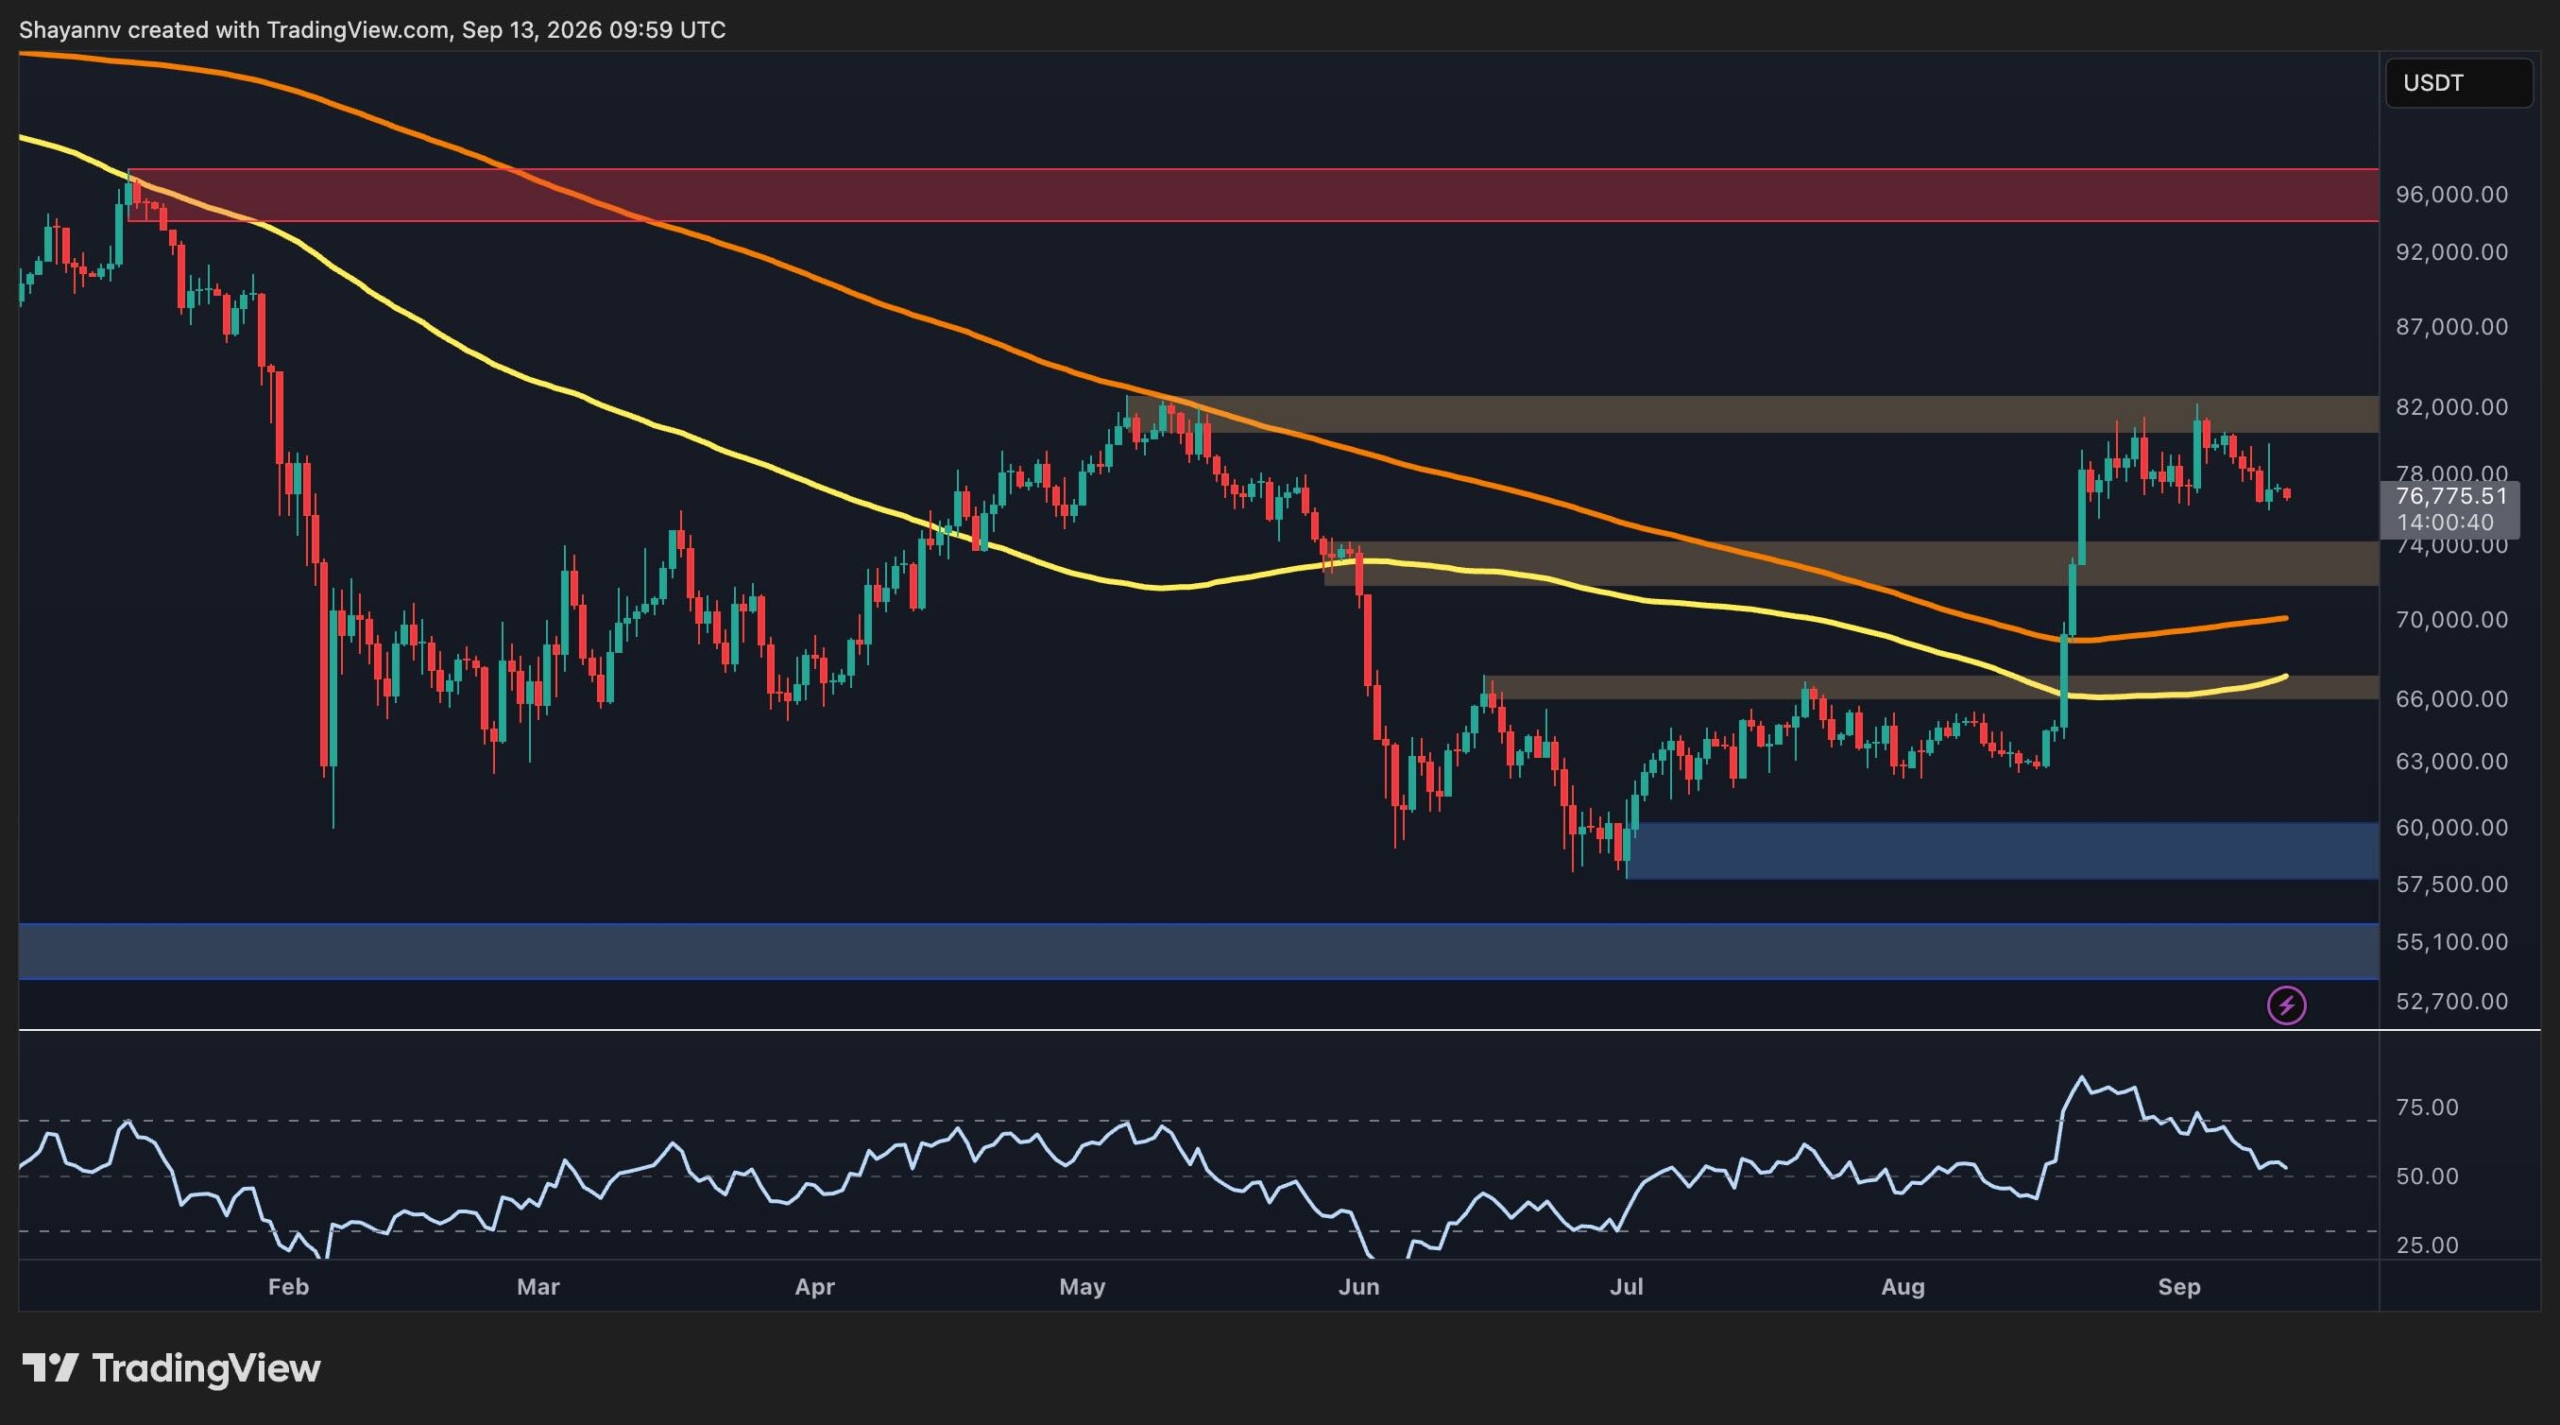
BTC/USDT 4-Hour Chart
The 4-hour chart provides a clearer view of the latest move. Bitcoin spent much of the summer trading sideways between roughly $60K and $67K before staging a sharp breakout. The move through the $67K resistance zone accelerated dramatically, taking BTC through $74K.
After reaching the $80K-$82K area, however, the rally has lost momentum. BTC is currently trading around $76.8K and has formed a relatively broad consolidation below resistance. This can be interpreted as a potential continuation range following the breakout, provided the lower boundary remains intact.
The immediate support is located around the same daily $72K-$74K zone. This area is particularly important because it represents the previous resistance zone that BTC cleared during the breakout. Holding it would maintain the sequence of higher highs and higher lows on the 4-hour timeframe.
The main resistance remains $80K-$82K. A clean breakout and sustained trading above this zone would signal that buyers are regaining control and could bring the next major daily resistance around $95K into consideration. Conversely, repeated rejection followed by a break below $72K could trigger a deeper retracement toward $67K.

On-Chain Analysis
The Coinbase Premium Index provides an important caveat to the technical picture. The metric measures the price difference between Bitcoin on Coinbase and other major exchanges and is commonly used as a proxy for US-based spot buying pressure. Positive readings generally indicate stronger demand on Coinbase, while negative readings suggest comparatively weaker US spot demand.
The latest reading on the chart is around -0.02, with the index back in negative territory. This is notable because BTC has simultaneously remained well above the levels seen before the late-August breakout.
The divergence suggests that the recent price strength has not been accompanied by a sustained surge in Coinbase buying pressure. In other words, while the technical structure has improved, the latest premium data does not yet provide strong confirmation of aggressive US spot accumulation.
Historically, within the period shown, the Coinbase Premium spent considerable time below zero during BTC’s decline toward the $60K area, while stronger positive readings appeared during several recovery phases. The current negative reading, therefore, warrants some caution as Bitcoin approaches the $80K-$82K resistance zone.
For the bullish scenario to strengthen, a renewed move of the Coinbase Premium into positive territory alongside a breakout above $82K would provide more convincing confirmation. If BTC instead loses $72K while the premium remains negative, it would increase the probability that the recent rally is undergoing a deeper correction rather than immediately transitioning into another leg higher.

The post Bitcoin Price Analysis: BTC Faces a Make-or-Break Week – What’s the Most Likely Scenario? appeared first on CryptoPotato.
Although the upcoming vote on the Digital Asset Market Clarity Act is not a final passage vote, it still holds significance for the broader crypto market as senators will decide whether to advance debate on the legislation. Cloture requires 60 votes, meaning that even if all Republicans support it, they would still need assistance from some Democrats or independents.
XRP could be among the most intertwined crypto assets with the bill, which is why a potential failure could weigh on its price quite considerably. As such, we asked ChatGPT about its take on the matter and what could happen to the cross-border token.
Why CLARITY Matters for XRP
The bill aims to create a comprehensive federal crypto market structure, including clearer responsibilities for the two main watchdogs – the SEC and the CFTC, and rules for exchanges, brokers, dealers, and digital commodities. This is particularly relevant for the cross-border token following Ripple’s years-long regulatory battle with the SEC.
After the conclusion of the lawsuit that began in late 2020, the regulator identified XRP as a digital commodity. As such, the legislation would make the broader regulatory framework more durable by codifying it into federal law, since history has shown that the SEC’s allegiance shifts quickly with each new administration.
Overall, even though a failure on the CLARITY Act’s vote next week would remove a potential bullish catalyst, it wouldn’t erase all of XRP’s regulatory progress experienced in the past year and a half.
But Still – Will XRP Tumble?
From a technical standpoint, XRP is currently near $1.40, above the key support at $1.34-$1.35, but it hasn’t reclaimed the crucial resistance at $1.40. If cloture fails but BTC and the broader crypto market remain stable, ChatGPT envisioned a 7% to 10% initial reaction for Ripple’s token, which would materialize with a dip to $1.20-$1.25.
A more aggressive selloff could drive the asset south toward $1.10, especially if markets interpret the result as evidence that comprehensive US crypto legislation could be delayed well after the midterms.
The dark horse comes a day later, when the Federal Reserve will conclude its September 15-16 FOMC meeting. A failed CLARITY Act vote followed by a hawkish Fed decision could turn an XRP-specific regulatory disappointment into a broader crypto selloff. In that scenario, the AI platform predicted a more painful decline toward $1.00.
On the plus side, ChatGPT said a lack of progress on the CLARITY Act alone wouldn’t be as strong a catalyst to drive XRP below $1.00.
The post What Happens to XRP if the CLARITY Act Vote Fails on September 15? AI Maps the Downside appeared first on CryptoPotato.